Checkmarx alternatives
12 products compared · Updated November 1, 2026
The short answer
For teams already on GitHub, GitHub Projects offers lightweight issue tracking without leaving the codebase, but it lacks security scanning. GitLab includes SAST in its free tier and integrates security into merge requests, making it a strong fit for existing GitLab users. Snyk provides a free plan and transparent credit-based pricing, ideal for small development teams wanting to start without a sales call. For broader code quality and security, SonarQube is a developer-first option with quality gates and support for 45+ languages.
Your shortlist, at a glance
Read the comparisons ↓- VVeracodeNot publishedEnterprise security teams that need low-noise findings and AI-assisted remediation across a large application portfolio.
- FFortifyNot publishedTeams already standardized on OpenText products that need a traditional SAST tool and are willing to evaluate Fortify through sales conversations.
 SonarQubeFrom $34/mo per 100k LEngineering teams that want code quality and security checks in one tool, with self-managed or cloud options and AI agent support.
 SnykFree. Team $25/moDevelopment teams of up to 10 developers who want to start with a free plan and scale to enterprise credits without a sales call.
 GitLabFrom $12/user/moTeams already on GitLab that want application security testing inside their existing DevOps pipeline.
 SemgrepFrom $30/contributor/mEngineering teams that want fast, low-noise SAST and SCA scanning with AI-assisted triage, especially those using GitHub or GitLab.
- AAppScanNot publishedEnterprises already using HCLSoftware products that need application security testing with SAST, DAST, and SCA capabilities.
- PPrisma CloudNot publishedCloud-first teams that need code security plus infrastructure and runtime protection in one platform.
- AAqua SecurityCustom quoteCloud native teams that need runtime protection and enforcement for containers, Kubernetes, and AI workloads across hybrid and multicloud environments.
 MendPer dev, custom quoteTeams building AI-powered applications that need security across both traditional code and AI components, with runtime guardrails.
- CContrast SecurityNot publishedTeams that prioritize runtime protection and want to see which vulnerabilities are actually under attack
 GitHub ProjectsFree / $4 / $21 per usDevelopment teams on GitHub that want issue tracking and project boards without leaving their code repository.
About Checkmarx and its alternatives
Checkmarx is an agentic application security platform that scans code, dependencies, containers, and AI components, with AI-powered triage and remediation. It is known for its unified code-to-cloud coverage and custom pricing tailored to each organization.
When comparing alternatives, weigh pricing structure (per user, per contributor, or custom quotes), deployment options (SaaS, self-hosted, or on-prem), integration with your existing DevOps tools, and the breadth of security features (SAST, SCA, DAST, runtime). Also consider contract terms, such as free tiers, credit-based models, and whether you need a sales conversation to get a quote.
Explore the alternatives
- VNot published
1.Veracode
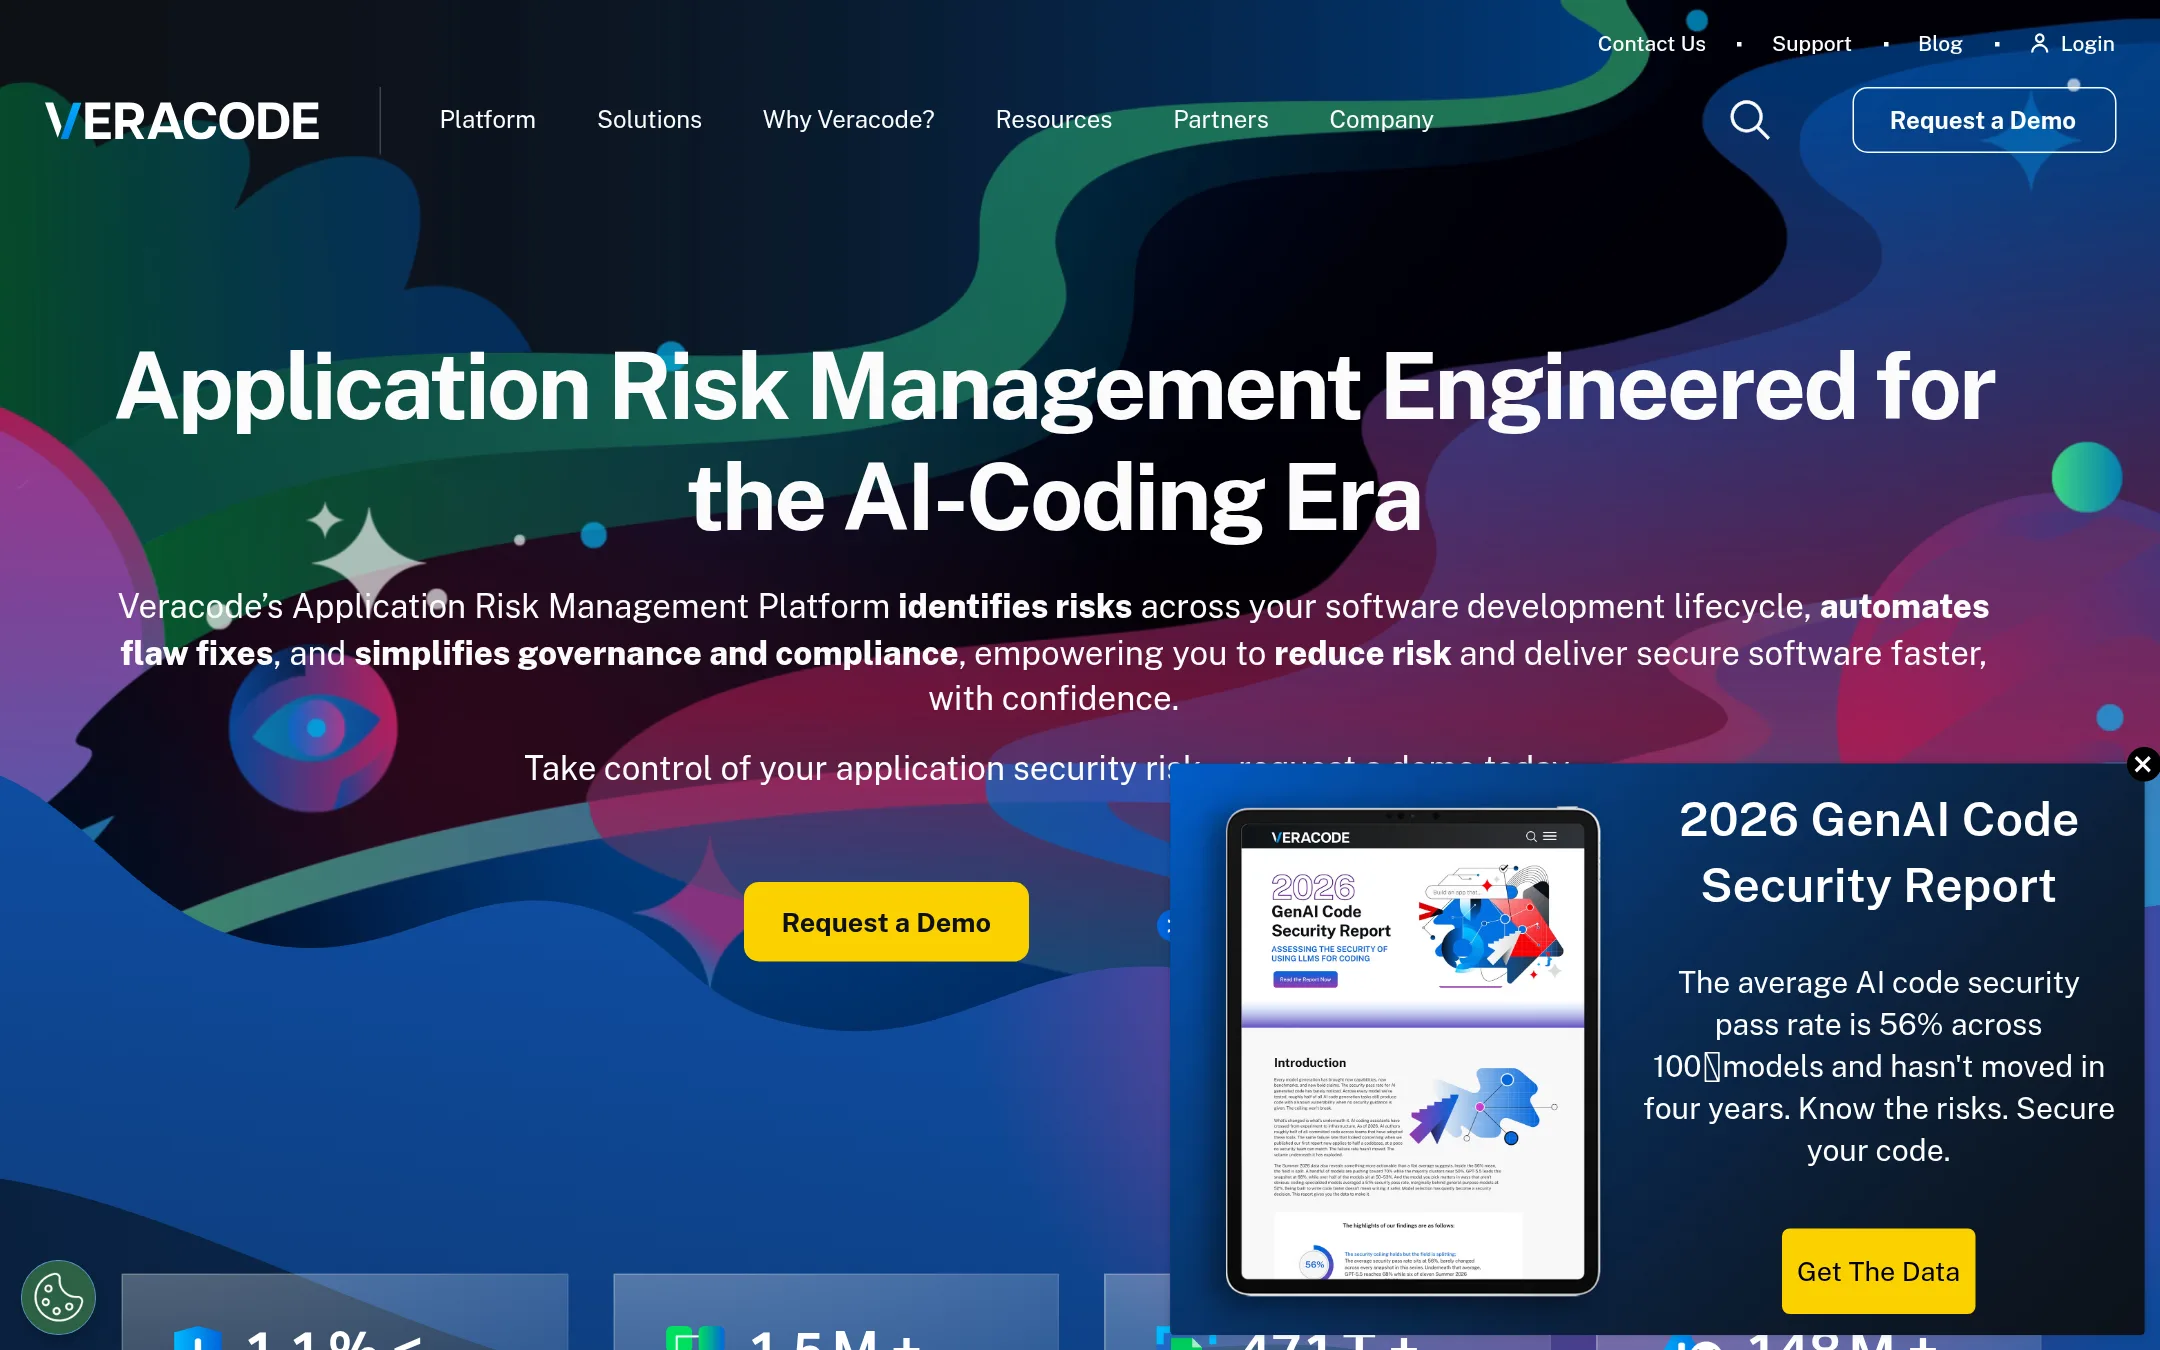
Best for: Enterprise security teams that need low-noise findings and AI-assisted remediation across a large application portfolio.
- Pricing
- Not published
- Category
- Other
Veracode is an application risk management platform that scans code, dependencies, and containers, and offers AI-driven fixes. You would choose it over Checkmarx if you want a platform with a strong focus on low false positives and enterprise-scale scanning, especially if your team needs help fixing flaws faster.
Where it is strong
- Low false-positive rate, so teams focus on real risks.
- Scans code, dependencies, and containers in one platform.
- AI-driven fixes integrated into developer workflows.
Where it falls short
- No published pricing, so you must contact sales for a quote.
- May be more enterprise-focused, with less flexibility for smaller teams.
- Pricing:
- Pricing is not published on the site.
- FNot published
2.Fortify
Best for: Teams already standardized on OpenText products that need a traditional SAST tool and are willing to evaluate Fortify through sales conversations.
- Pricing
- Not published
- Category
- Other
Fortify is an application security testing platform from OpenText. Its website was unreachable when we checked, so we could not verify current capabilities, integrations, or pricing. If you are already in the OpenText ecosystem and want a SAST-focused tool, it may be worth exploring, but Checkmarx offers a broader code-to-cloud platform with AI-powered remediation.
Where it is strong
- Long-standing SAST vendor with enterprise heritage.
- Part of the OpenText portfolio, which may bundle with other OpenText tools.
- Supports a wide range of languages and frameworks historically.
Where it falls short
- Website was unreachable, so we could not verify current features or roadmap.
- No public pricing or self-serve trial. You must contact sales.
- Pricing:
- Pricing is not published on the site.
- From $34/mo per 100k L
3.SonarQube
Best for: Engineering teams that want code quality and security checks in one tool, with self-managed or cloud options and AI agent support.
- Pricing
- From $34/mo per 100k L
- Category
- Developer Tools
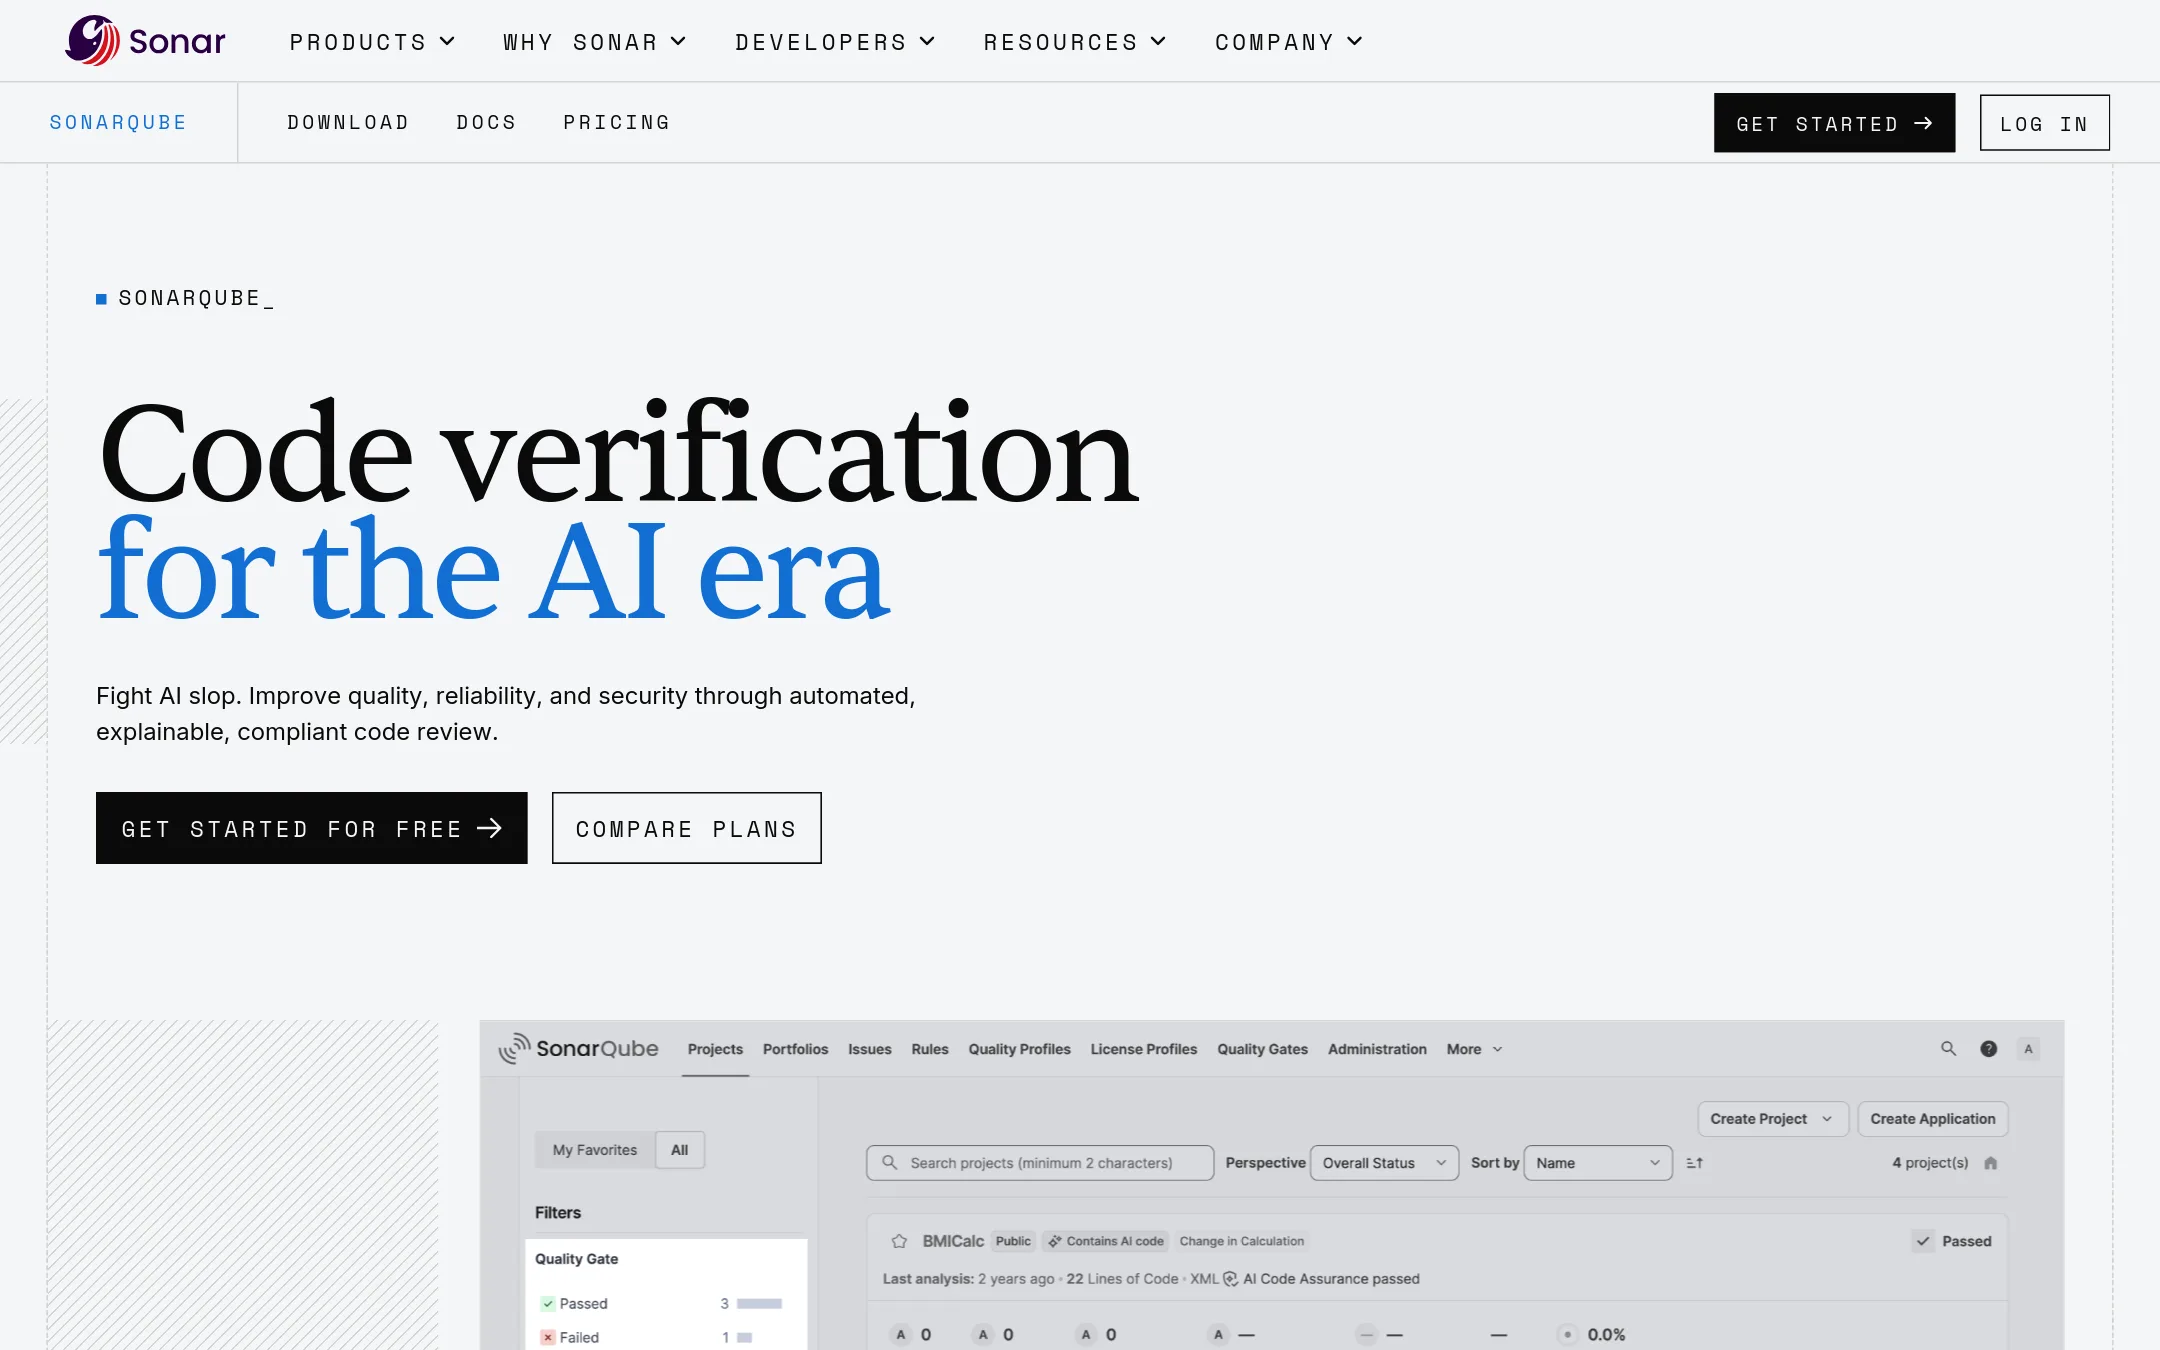
SonarQube is a code quality and security platform that reviews every pull request for bugs, vulnerabilities, and maintainability issues across 45+ languages. Teams that want a developer-first tool with strong governance and quality gates, rather than a dedicated AppSec platform, would choose it over Checkmarx.
Where it is strong
- Supports 45+ languages, including mobile and mainframe.
- Quality gates enforce standards and provide auditable evidence.
- Works with coding agents via MCP, CLI, and IDE plugins.
Where it falls short
- Advanced security features (SCA, secrets) require the Advanced Security add-on.
- Enterprise features like security reports are only in the Enterprise edition.
- Pricing:
- Pricing starts at $34 monthly for analysis of up to 100k lines of code, with a free tier for private projects up to 50k LoC.
- Switching from Checkmarx:
- Moving from Checkmarx means shifting from a dedicated AppSec platform to a code quality and security tool, so you'll need to reconfigure your security policies and quality gates.
- Free. Team $25/mo
4.Snyk
Best for: Development teams of up to 10 developers who want to start with a free plan and scale to enterprise credits without a sales call.
- Pricing
- Free. Team $25/mo
- Category
- Security & Privacy
Snyk is an AI-native security platform that scans code, dependencies, containers, and infrastructure as code. It's a good fit if you want a developer-friendly tool with a free tier and transparent credit-based pricing, rather than Checkmarx's package-based custom quotes.
Where it is strong
- Free tier includes SCA, SAST, IaC, and Container scanning.
- Credit-based enterprise pricing is transparent and flexible.
- Integrates with IDEs, CLI, and source code managers.
Where it falls short
- Evo capabilities like AI Pentesting require an Enterprise subscription.
- Team plan is limited to 10 developers, so larger teams must go enterprise.
- Pricing:
- Free plan at $0/month. Team plan starts at $25/month for up to 10 developers. Enterprise uses credits at $1 per credit, with rates like 1.0 credits per active contributor per day for Code.
- Switching from Checkmarx:
- Moving from Checkmarx to Snyk means adopting a credit-based model and a different scanning interface, but the free tier lets you test without commitment.
- From $12/user/mo
5.GitLab
Best for: Teams already on GitLab that want application security testing inside their existing DevOps pipeline.
GitLab is a DevSecOps platform that includes source control, CI/CD, and security scanning in one place. You would choose it over Checkmarx if you want security built into your existing GitLab workflow rather than as a separate tool. It's a fit for teams already using GitLab who want to avoid adding another vendor.
Where it is strong
- SAST is included in the Free plan, so you can start without paying.
- Security findings appear directly in merge requests, so developers see them in context.
- Pricing is per user with clear tiers, unlike Checkmarx's custom quotes.
Where it falls short
- Security scanning is limited to GitLab's built-in tools, which may not match Checkmarx's breadth (e.g., DAST, API Security).
- Advanced security features like DAST and compliance require the Ultimate plan, which is more expensive.
- Pricing:
- Free plan includes SAST for up to 5 users. Paid plans start at $12 per user/month for Premium and $24 per user/month for Ultimate, with GitLab Credits included for AI features.
- Switching from Checkmarx:
- Moving from Checkmarx to GitLab means replacing your SAST and SCA scanning with GitLab's built-in tools, so you'll need to reconfigure your CI/CD pipelines and retrain developers on new workflows.
- From $30/contributor/m
6.Semgrep
Best for: Engineering teams that want fast, low-noise SAST and SCA scanning with AI-assisted triage, especially those using GitHub or GitLab.
- Pricing
- From $30/contributor/m
- Category
- Developer Tools
Semgrep is a developer-friendly AppSec platform that combines SAST, SCA, and secrets detection with AI-assisted triage and remediation. It's a good fit if you want high-signal results with fewer false positives and a tool that works directly in your CI/CD and IDE. Choose it over Checkmarx if you prefer a more extensible, rule-based approach and need transparent per-contributor pricing.
Where it is strong
- High signal with AI-assisted triage that reduces false positives by up to 80%
- Works in CLI, CI/CD, and IDEs, plus PR checks in GitHub, GitLab, Bitbucket, and Azure
- Free tier available for small teams
Where it falls short
- Pricing is per contributor, which can get expensive for large teams
- Some advanced features like on-prem SCM support are only in the Enterprise plan
- Pricing:
- Free tier scans up to 10 repositories with 10 contributors. Paid plans start at $30 per contributor per month for Code or Supply Chain, and $15 per contributor per month for Secrets.
- Switching from Checkmarx:
- Moving from Checkmarx involves reconfiguring your CI/CD pipelines and IDE integrations, and you'll need to map your existing rules and policies to Semgrep's rule format.
- ANot published
7.AppScan
Best for: Enterprises already using HCLSoftware products that need application security testing with SAST, DAST, and SCA capabilities.
- Pricing
- Not published
- Category
- Other
AppScan is HCLSoftware's application security testing suite, covering static analysis, dynamic testing, and software composition analysis. Choose it over Checkmarx if you are already invested in HCL's broader enterprise software portfolio and want an AppSec tool that integrates with that ecosystem. It is also a strong option for teams that value Gartner recognition and need a vendor with a long history in the security testing space.
Where it is strong
- Recognized as a Leader in the 2025 Gartner Magic Quadrant for Application Security Testing.
- Part of a large enterprise software portfolio, so it can integrate with other HCL tools.
- Includes SAST, DAST, and SCA in one suite, covering multiple testing types.
Where it falls short
- Pricing is not transparent. You must contact sales for a quote.
- Less focused on AI-driven agentic security features compared to Checkmarx's newer offerings.
- Pricing:
- Pricing is not published on the site. The pricing page returns a 404 error.
- PNot published
8.Prisma Cloud
Best for: Cloud-first teams that need code security plus infrastructure and runtime protection in one platform.
- Pricing
- Not published
- Category
- Other
Prisma Cloud is a cloud-native application protection platform (CNAPP) that secures applications from code to cloud, including runtime protection. Choose it over Checkmarx if your priority is securing cloud infrastructure and workloads across multicloud and hybrid environments, not just application code.
Where it is strong
- Covers code, infrastructure, and runtime in one platform
- AI-powered risk prioritization and Copilot for faster fixes
- SaaS and self-hosted deployment options
Where it falls short
- No published pricing, requires a custom quote
- Broader cloud focus may be overkill for teams that only need application code scanning
- Pricing:
- Pricing is not published on the site.
- ACustom quote
9.Aqua Security
Best for: Cloud native teams that need runtime protection and enforcement for containers, Kubernetes, and AI workloads across hybrid and multicloud environments.
- Pricing
- Custom quote
- Category
- Other
Aqua Security is a cloud native application protection platform that focuses on runtime security for containers, Kubernetes, serverless, and AI workloads. It correlates code and image risk with live workload behavior, so teams can prioritize real exposure and enforce policy at the point of execution. Choose Aqua over Checkmarx if your priority is protecting running cloud workloads rather than static code analysis.
Where it is strong
- Runtime enforcement blocks attacks at execution, not just alerts
- Risk ranked by live workload behavior, so teams focus on real exposure
- Works in air gapped and disconnected environments
Where it falls short
- Pricing not published, requires a trial or demo
- Less emphasis on SAST and code-level static analysis compared to Checkmarx
- Pricing:
- Pricing is based on the number of code repositories for Dev Security and on the number of workloads for Cloud Security. No specific dollar amounts are published.
- Switching from Checkmarx:
- Moving from Checkmarx to Aqua means shifting focus from code scanning to runtime protection, and you will need to map your CI/CD and cloud environments to Aqua's repository and workload-based pricing.
- Per dev, custom quote
10.Mend
Best for: Teams building AI-powered applications that need security across both traditional code and AI components, with runtime guardrails.
Mend unifies application security and AI security in one platform, covering source code, open-source dependencies, containers, and AI components like models and agents. Choose it over Checkmarx if you need continuous AI behavioral testing and runtime protection for AI features, not just static analysis.
Where it is strong
- Covers both AppSec and AI security in one platform
- Automated red teaming for AI behavioral risks
- Runtime in-app protection for production AI interactions
Where it falls short
- No published pricing, requires a sales conversation
- AI security features may be more than teams needing only SAST/SCA
- Pricing:
- Pricing is not published on the site. It is quoted per contributing developer.
- Switching from Checkmarx:
- Moving from Checkmarx involves replacing SAST/SCA workflows with Mend's equivalents and adding its AI security modules, which may require new policies and training for developers.
- CNot published
11.Contrast Security
Best for: Teams that prioritize runtime protection and want to see which vulnerabilities are actually under attack
- Pricing
- Not published
- Category
- Other
Contrast Security uses runtime instrumentation to observe application behavior and block attacks in real time, rather than relying on static scanning. Choose it if you want to focus on verified, exploitable vulnerabilities and reduce false positives, especially with AI-generated code.
Where it is strong
- Runtime visibility into real attacks, not just static predictions
- Low false positive rate, measured by an enterprise customer across 21,000 vulnerabilities
- Blocks attacks in real time, reducing CVE triage workload
Where it falls short
- No pricing details available, so budgeting requires a sales call
- Runtime approach may not cover all static analysis needs that Checkmarx provides
- Pricing:
- Pricing is not published on the site.
- Free / $4 / $21 per us
12.GitHub Projects
Best for: Development teams on GitHub that want issue tracking and project boards without leaving their code repository.

- Pricing
- Free / $4 / $21 per us
- Category
- Productivity & Project Management
GitHub Projects is a project management layer built into GitHub, so it keeps planning and tracking next to the code. You would choose it over Checkmarx if your team already lives in GitHub and needs lightweight issue tracking, not application security scanning.
Where it is strong
- Native integration with GitHub repos and pull requests
- Free tier includes unlimited private repositories
- Supports issues, projects, and basic automation
Where it falls short
- No SAST, SCA, or DAST scanning capabilities
- Not a security tool. Lacks vulnerability detection and remediation
- Pricing:
- Free for individuals. Team is $4 per user per month. Enterprise is $21 per user per month.
- Switching from Checkmarx:
- Moving from Checkmarx to GitHub Projects means giving up all security scanning. You would need a separate AppSec tool.
See more comparisons in Security & Privacy alternatives.
FAQ
Questions about Checkmarx alternatives
What is the best free option for a small team?
Snyk offers a free plan that includes SCA, SAST, IaC, and Container scanning for up to 10 developers. GitLab's Free plan includes SAST for up to 5 users. SonarQube has a free tier for private projects up to 50k lines of code.
Which alternative has the most transparent pricing?
Snyk publishes a free tier and a Team plan at $25/month for up to 10 developers, with enterprise credits at $1 per credit. Semgrep lists per-contributor pricing starting at $30 per month. GitLab has clear per-user tiers starting at $12 per user/month.
Which tool is best for teams already using GitHub?
GitHub Projects is built into GitHub and offers issue tracking and project boards, but it lacks security scanning. For security, Semgrep integrates with GitHub PR checks and offers a free tier, while Snyk also integrates with GitHub and provides a free plan.
Which alternative provides runtime protection?
Aqua Security focuses on runtime protection for containers and Kubernetes, with enforcement at execution. Contrast Security uses runtime instrumentation to block attacks in real time. Prisma Cloud covers runtime protection for cloud workloads.
Are there any alternatives with no published pricing?
Yes, Mend, Veracode, Aqua Security, Fortify, AppScan, Prisma Cloud, and Contrast Security do not publish pricing on their sites. You must contact sales for a custom quote, which may be less transparent than tools like Snyk or Semgrep.
Last updated November 1, 2026.