Snyk alternatives
12 products compared · Updated November 1, 2026
The short answer
For teams that want automated code review with security checks on every pull request, DeepSource is a strong alternative. SonarQube suits teams needing rigorous code quality and governance with auditable quality gates. Enterprises that need unified AppSec and AI security with runtime protection should consider Mend.
Your shortlist, at a glance
Read the comparisons ↓ GitHub ProjectsFree / $4 per user/moDevelopment teams already using GitHub that want simple issue tracking and project boards next to their code.
- VVeracodeNot publishedLarge enterprises with complex application portfolios that need unified risk visibility and automated remediation across the SDLC.
 CheckmarxCustom quoteEnterprises that need a broad AppSec platform with SAST, SCA, API security, and AI governance, and are willing to go through a sales consultation for custom pricing.
 SonarQubeFrom $34/mo per 100k LTeams that need rigorous code quality and security verification with strong governance and auditability, particularly those running self-managed infrastructure.
- OOpenTextNot publishedLarge enterprises that need to secure and govern information across content, data, and applications, not just code.
- AAqua SecurityCustom quoteSecurity teams running cloud native workloads in production who need runtime protection and policy enforcement, not just code and dependency scanning.
 CodacySee websiteCode quality, security & AI policy enforcement for fast-moving dev teams
 CodeAnt AISee websiteAI Code Health Platform
 CorgeaSee websiteCorgea finds, and fixes insecure code and packages autonomously.
 DeepSourceNot publishedEngineering teams that want automated code review with security checks on every pull request, especially those using AI coding assistants.
 EscapeSee websiteThe only DAST that works with modern stack and tests business logic
 Gecko SecuritySee websiteThe AI Security Engineer to Find and Fix Vulnerabilities
About Snyk and its alternatives
Snyk is an AI-native security platform that secures code, dependencies, containers, and infrastructure as code. It is known for developer-friendly scanning, IDE and CI/CD integrations, and a credit-based enterprise pricing model.
When comparing alternatives, weigh pricing structure, whether it is per user, per line of code, or custom. Consider regions and deployment options, such as self-managed or air-gapped. Check integrations with your existing tools and AI coding assistants. Evaluate support and contract terms, especially if pricing is not public.
Explore the alternatives
- Free / $4 per user/mo
1.GitHub Projects
Best for: Development teams already using GitHub that want simple issue tracking and project boards next to their code.

- Pricing
- Free / $4 per user/mo
- Category
- Productivity & Project Management
GitHub Projects is a lightweight project management layer built into GitHub, so teams that already live in pull requests and issues can track work without leaving their code. Choose it over Snyk when your priority is planning and tracking development work, not scanning for vulnerabilities. Snyk focuses on security. GitHub Projects focuses on workflow.
Where it is strong
- Native integration with GitHub issues and pull requests.
- Free tier includes unlimited repositories and Dependabot updates.
- Enterprise plan includes Copilot and advanced security features.
Where it falls short
- No vulnerability scanning or security-focused features like Snyk.
- Project management features are basic compared to dedicated tools.
- Pricing:
- Free for unlimited public and private repositories. Team is $4 per user per month. Enterprise is $21 per user per month.
- Switching from Snyk:
- Moving from Snyk to GitHub Projects means shifting from security scanning to project tracking, so you would need a separate security tool for vulnerability management.
- VNot published
2.Veracode
Best for: Large enterprises with complex application portfolios that need unified risk visibility and automated remediation across the SDLC.
- Pricing
- Not published
- Category
- Other
Veracode is an application risk management platform that scans code, dependencies, containers, and runtime signals, with AI-driven fix suggestions. Choose it over Snyk when you need enterprise-scale scanning with a low false-positive rate and strong governance features for compliance.
Where it is strong
- Low false-positive rate, so teams focus on real risks
- Scans code, dependencies, containers, and runtime signals
- AI-driven fixes integrated into developer workflows
Where it falls short
- No public pricing, requires contacting sales
- May be heavier than Snyk for small teams or individual developers
- Pricing:
- Pricing is not published on the site.
- Custom quote
3.Checkmarx
Best for: Enterprises that need a broad AppSec platform with SAST, SCA, API security, and AI governance, and are willing to go through a sales consultation for custom pricing.
- Pricing
- Custom quote
- Category
- Security & Privacy
Checkmarx One is a unified AppSec platform that covers SAST, SCA, API security, and more, with AI-powered agents for triage and remediation. Choose it over Snyk if you need a broad, enterprise-grade platform with strong static analysis and AI supply chain visibility, and you prefer a custom quote over Snyk's self-serve plans.
Where it is strong
- Covers SAST, SCA, API security, and AI inventory in one platform.
- AI-powered triage and remediation assist reduce false positives and speed fixes.
- Hybrid scanning combines rules-based precision with Anthropic's AI for high fidelity.
Where it falls short
- No self-serve pricing. You must contact sales for a custom quote.
- May be more complex to set up than Snyk's simpler, developer-friendly plans.
- Pricing:
- Pricing is not published on the site. Checkmarx One is priced per package and tailored to your environment, with quotes usually provided within one business day.
- Switching from Snyk:
- Moving from Snyk to Checkmarx One involves a sales consultation to tailor the package, and you'll need to migrate your scanning workflows and integrate with your CI/CD and IDE tools.
- From $34/mo per 100k L
4.SonarQube
Best for: Teams that need rigorous code quality and security verification with strong governance and auditability, particularly those running self-managed infrastructure.
- Pricing
- From $34/mo per 100k L
- Category
- Developer Tools
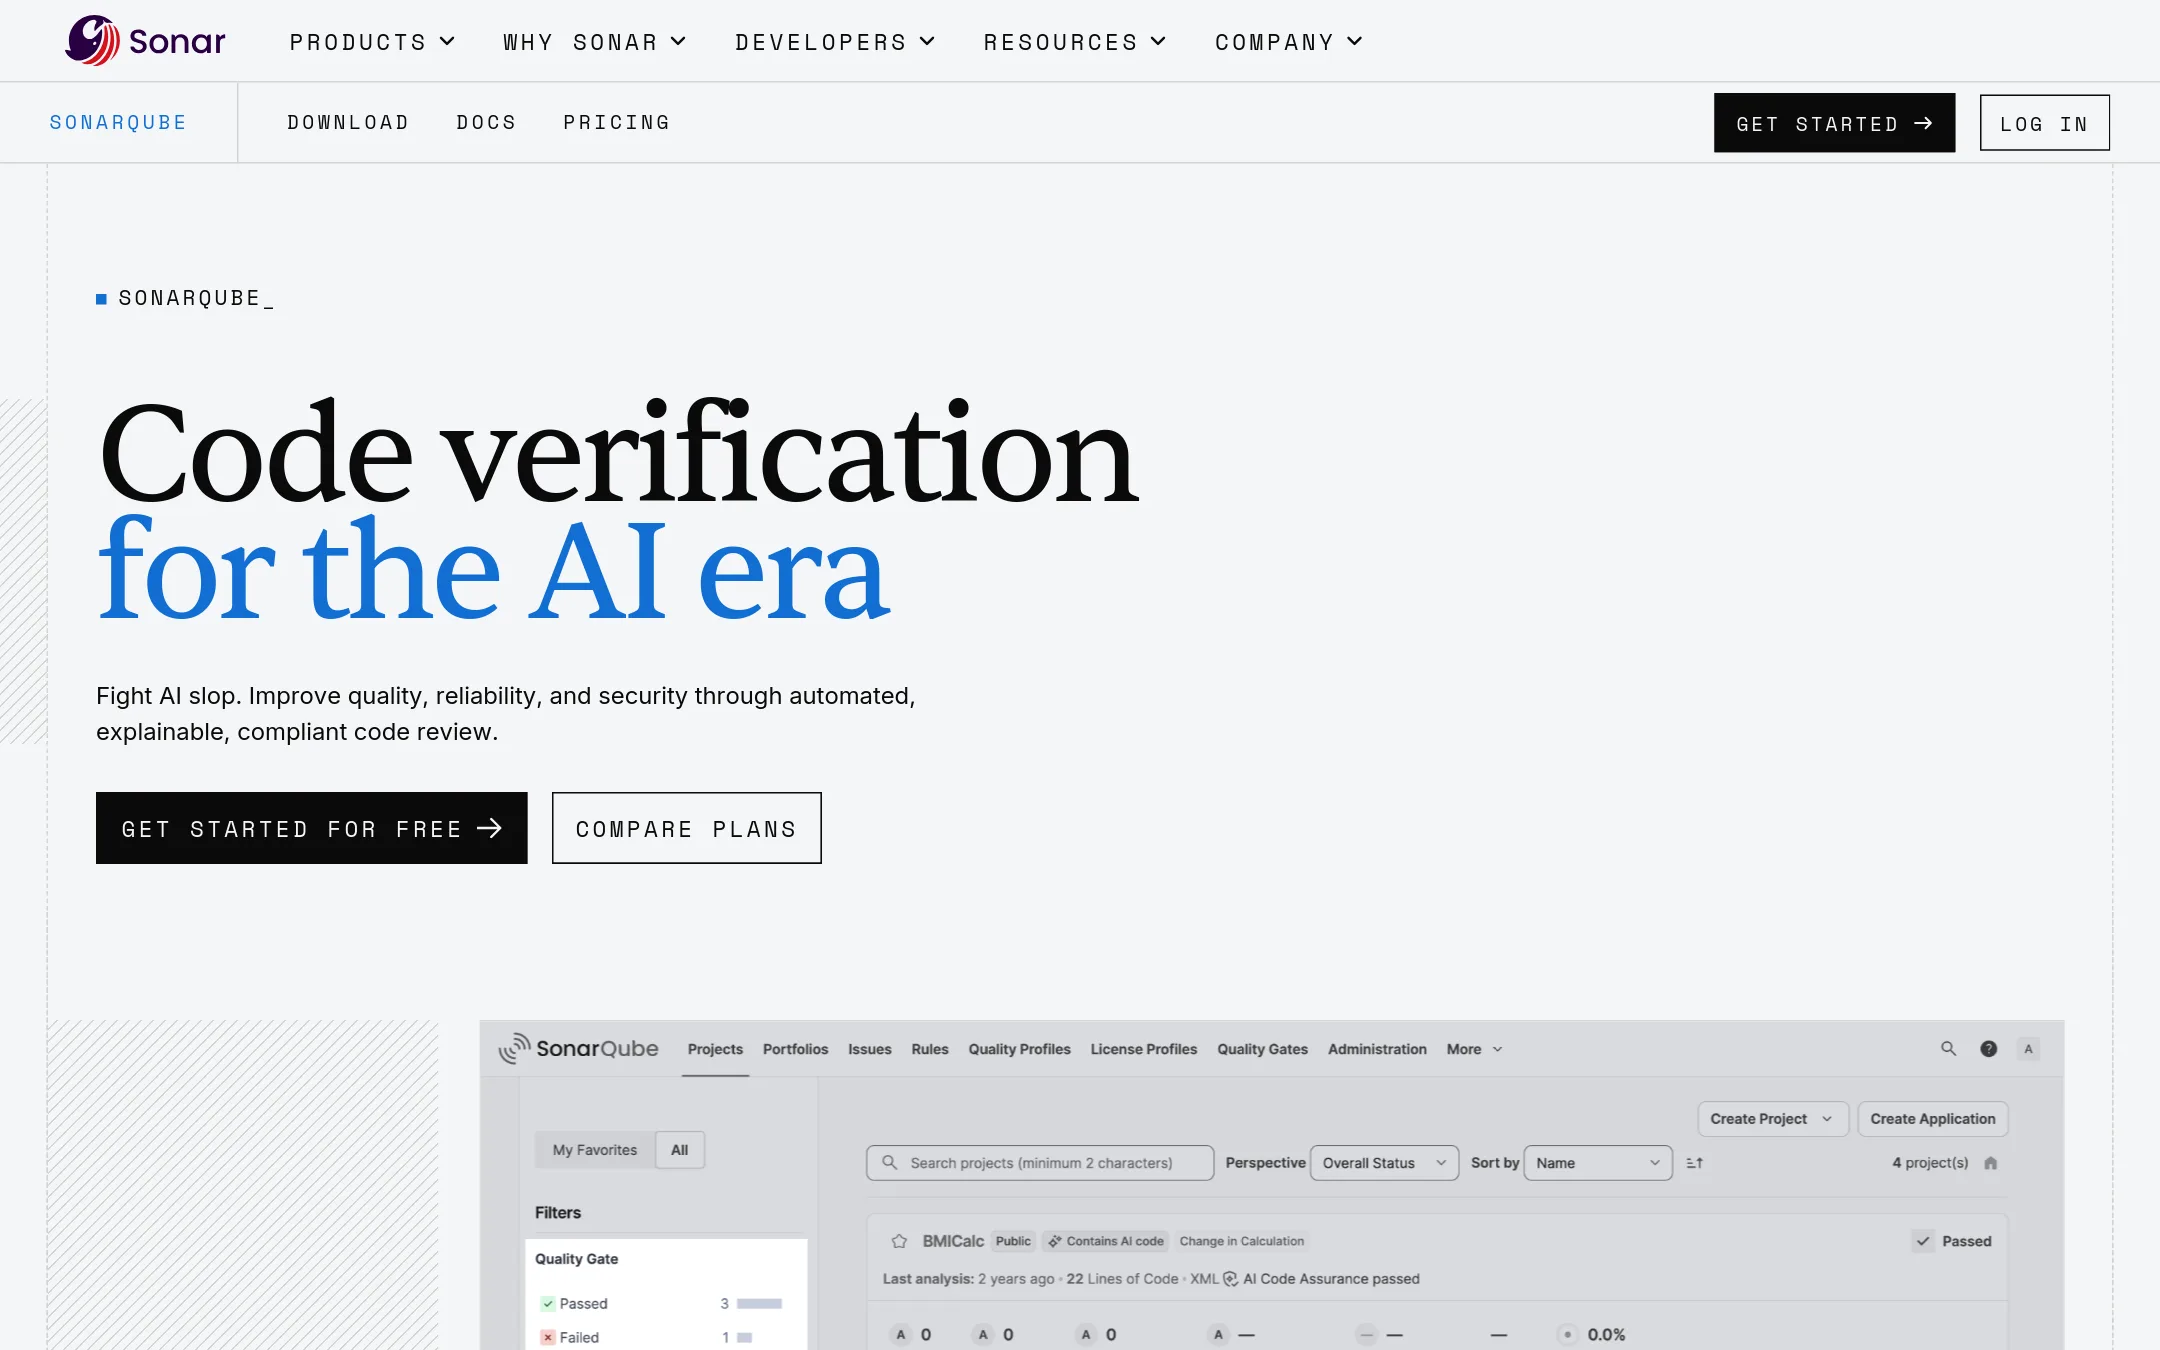
SonarQube is a code quality and security platform that verifies code written by humans and AI agents against standards you define. Choose it instead of Snyk when you need deep static analysis, architecture governance, and auditable quality gates across 45+ languages, especially for self-managed or air-gapped environments.
Where it is strong
- Covers 45+ languages with SAST, taint analysis, secrets detection, SCA, and IaC scanning.
- Quality gates with time-stamped evidence for every merge, useful for audits.
- Works with coding agents like Claude Code, Cursor, and Copilot via MCP server.
Where it falls short
- Pricing is based on lines of code, which can be unpredictable for large or growing codebases.
- Advanced security features like SCA and secrets detection require the Advanced Security add-on.
- Pricing:
- SonarQube Cloud starts at $34 monthly for up to 100k lines of code, with a free tier up to 50k LOC. Self-hosted Server editions are priced per instance per year based on LOC.
- Switching from Snyk:
- Moving from Snyk means reconfiguring your CI/CD and IDE integrations, and you'll need to map Snyk's test limits to SonarQube's LOC-based billing.
- ONot published
5.OpenText
Best for: Large enterprises that need to secure and govern information across content, data, and applications, not just code.
- Pricing
- Not published
- Category
- Other
OpenText is a broad enterprise information management platform covering content management, cybersecurity, and B2B integration. You would choose it over Snyk if you need to manage and secure data across the entire enterprise, not just code, and want a single vendor for multiple information management needs.
Where it is strong
- Covers a wide range of information management needs beyond code security.
- Trusted by 120k+ organizations, including 98 of the top 100 global companies.
- Offers AI-ready data governance and compliance frameworks.
Where it falls short
- Not a dedicated developer-first security tool like Snyk.
- Pricing is not transparent and likely requires a sales engagement.
- Pricing:
- Pricing is not published on the site.
- ACustom quote
6.Aqua Security
Best for: Security teams running cloud native workloads in production who need runtime protection and policy enforcement, not just code and dependency scanning.
- Pricing
- Custom quote
- Category
- Other
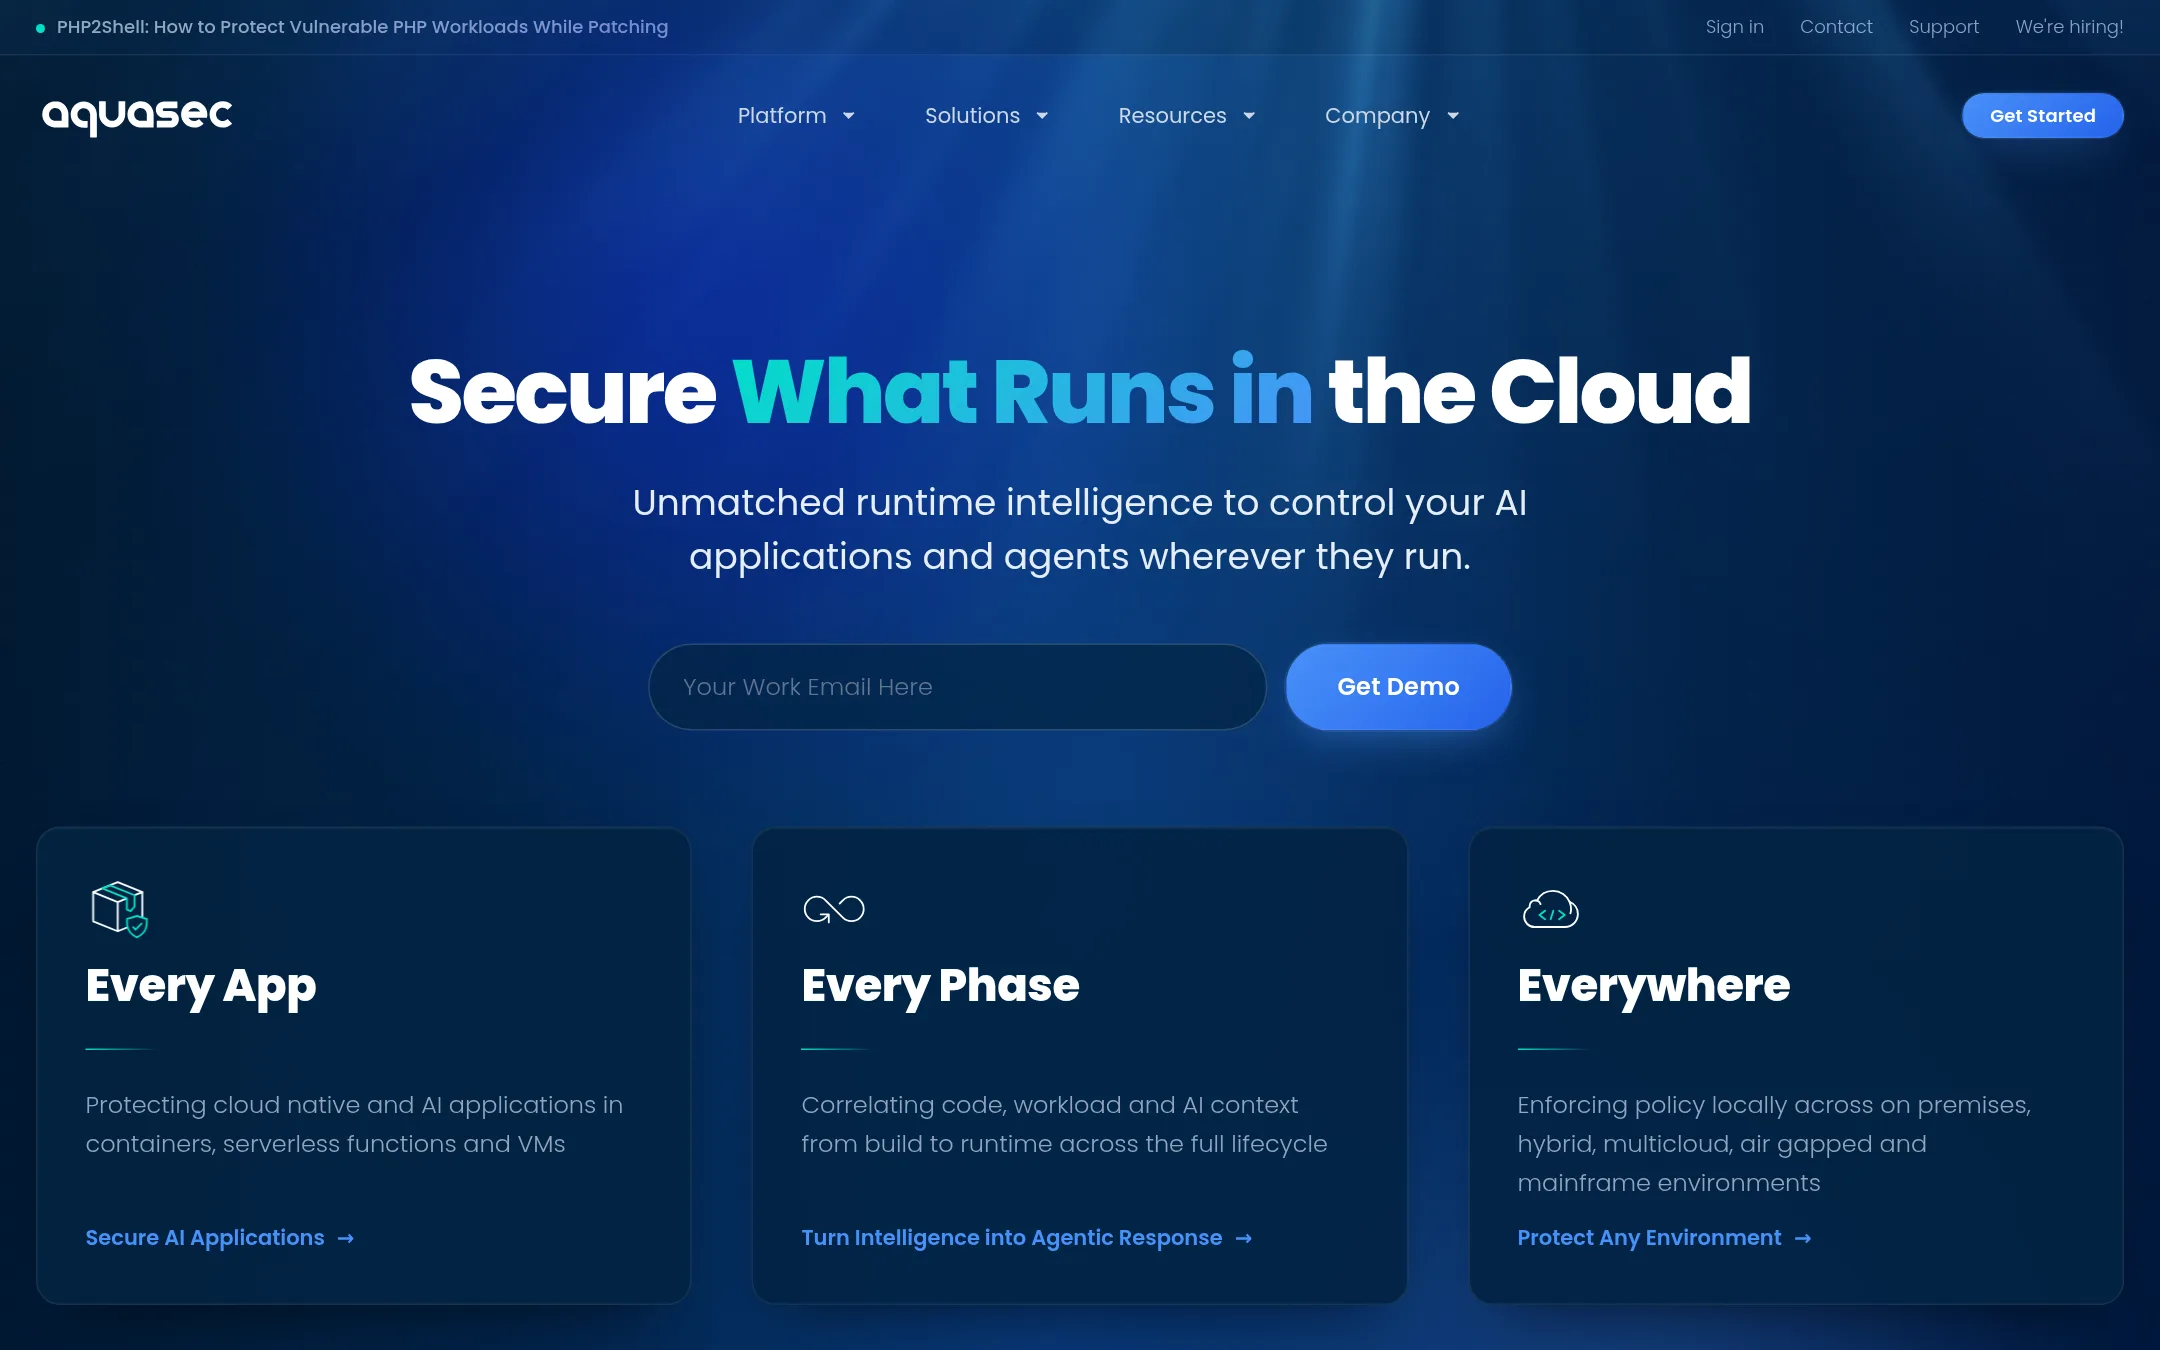
Aqua Security is a cloud native application protection platform that focuses on runtime security for containers, Kubernetes, serverless, and VMs. Choose it over Snyk when you need inline enforcement and threat detection in production, not just scanning at build time. It correlates code and image risk with live workload behavior to prioritize real exposure.
Where it is strong
- Runtime detection and response blocks attacks at execution, not just alerts
- Risk ranked by live workload behavior, so teams focus on real exposure
- Works across on-prem, hybrid, multicloud, and air-gapped environments
Where it falls short
- Pricing is not published, requiring a sales conversation
- Runtime focus may be overkill for teams that only need code and dependency scanning
- Pricing:
- Pricing is based on the number of code repositories for Dev Security and on the number of workloads (e.g., EC2 instances, Lambda functions) for Cloud Security. No specific dollar amounts are published.
- Switching from Snyk:
- Moving from Snyk means adding runtime agents and workload-based pricing, which is a different model than per-developer or per-test pricing.
- See website
7.Codacy
Developer Tools
Code quality, security & AI policy enforcement for fast-moving dev teams
- See website
8.CodeAnt AI
Developer Tools
AI Code Health Platform
- See website
9.Corgea
Security & Privacy
Corgea finds, and fixes insecure code and packages autonomously.
- Not published
10.DeepSource
Best for: Engineering teams that want automated code review with security checks on every pull request, especially those using AI coding assistants.
- Pricing
- Not published
- Category
- Developer Tools
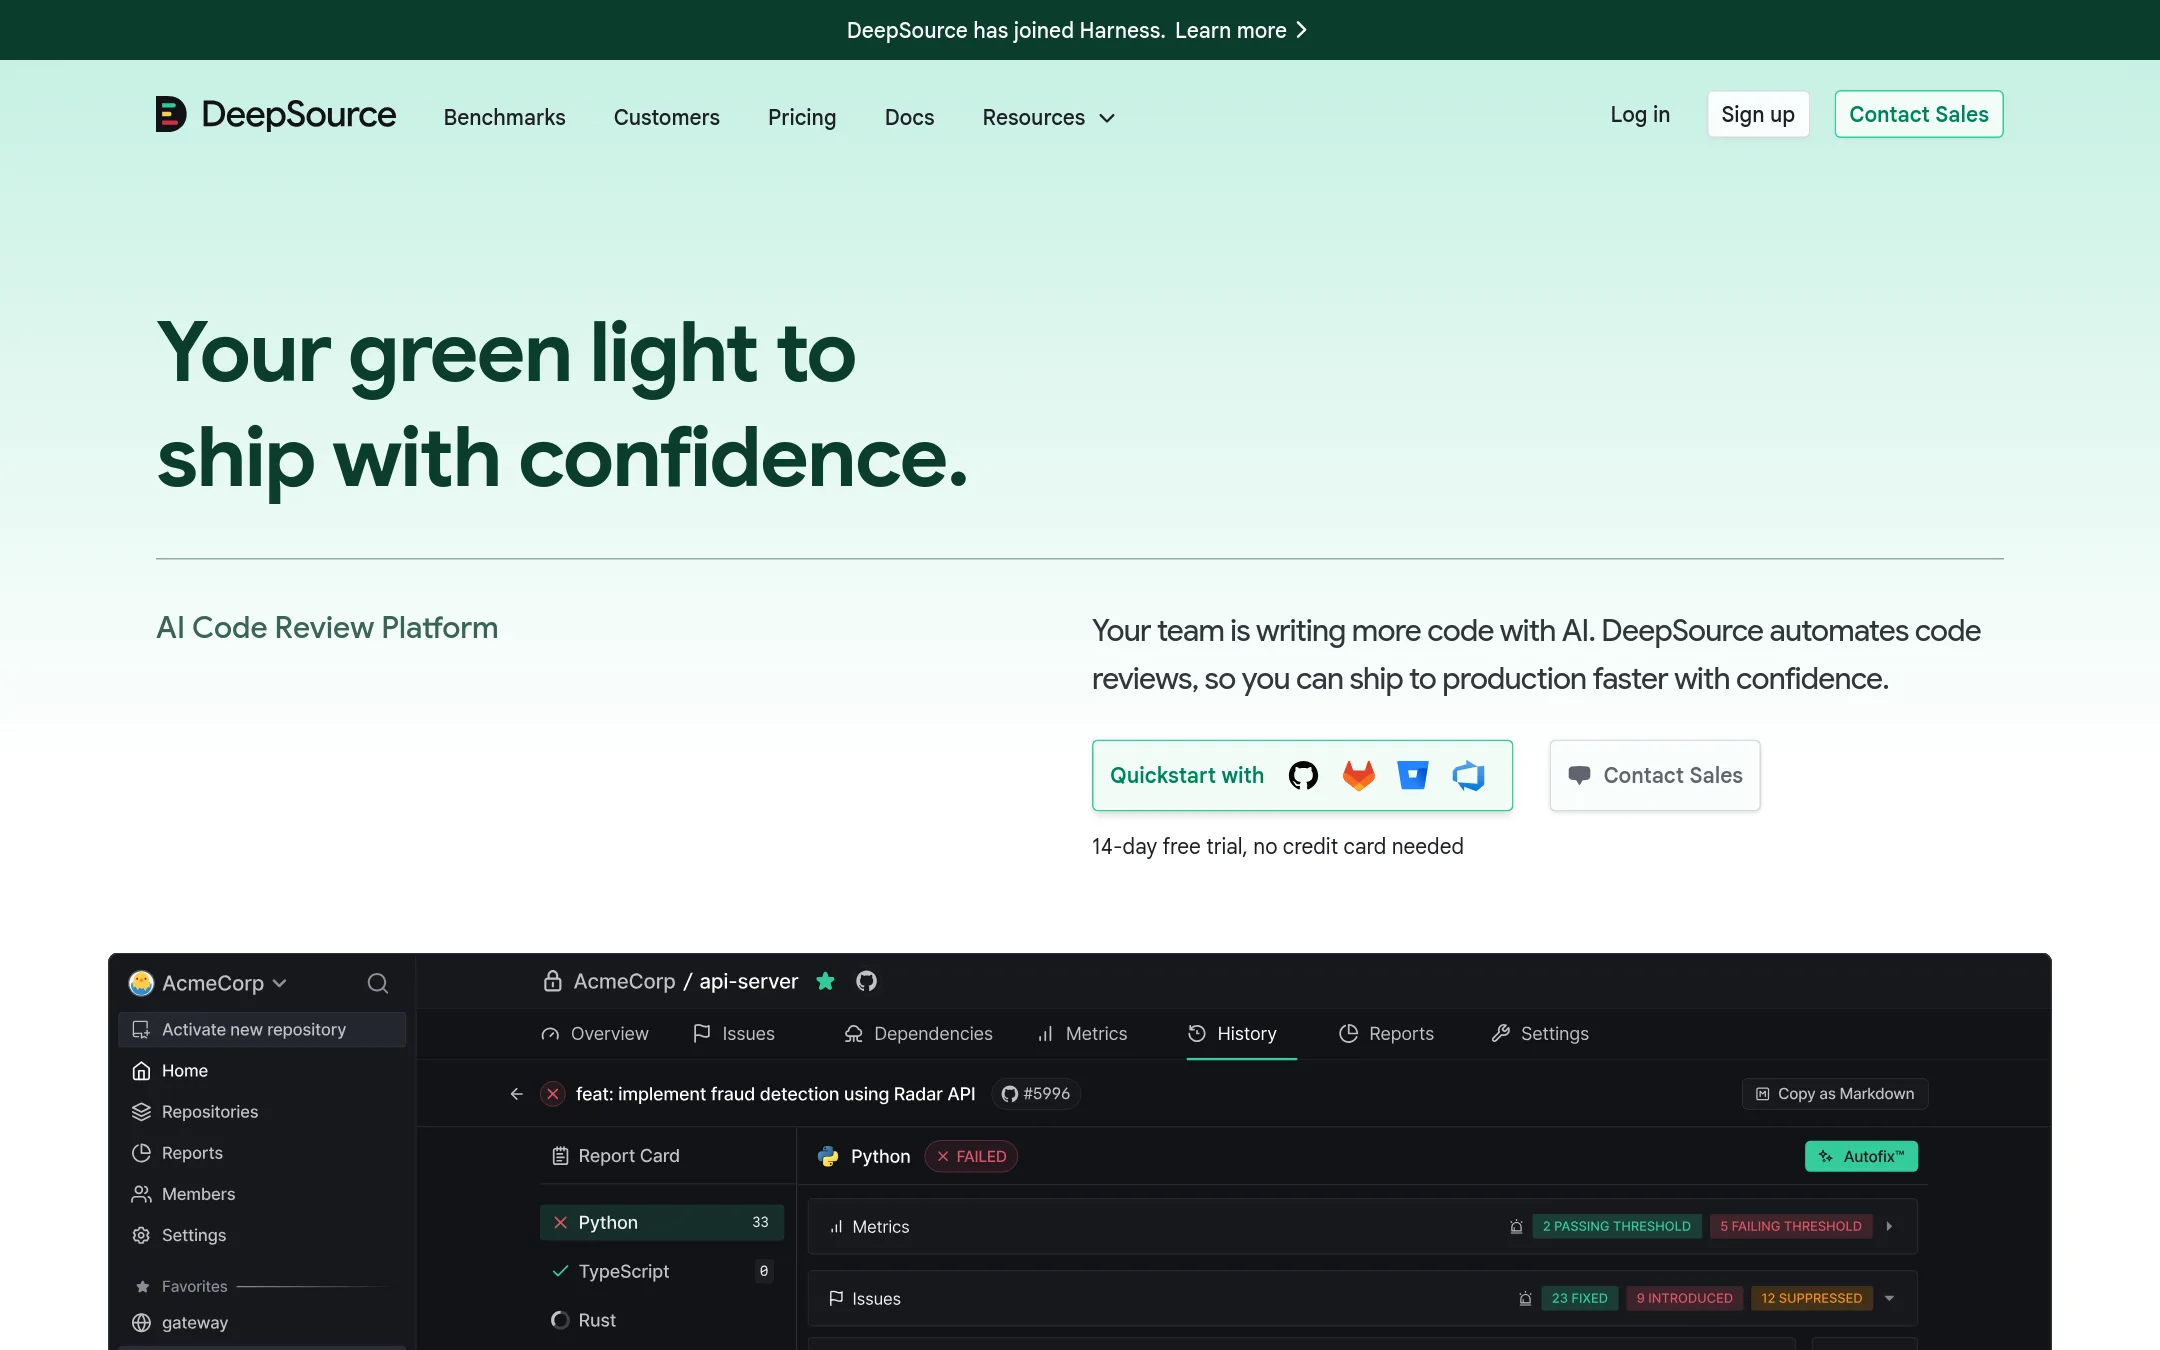
DeepSource is an AI code review platform that catches security issues, bugs, and anti-patterns on pull requests using 5,000+ deterministic rules plus an AI agent. It also scans for secrets, OSS vulnerabilities, and IaC misconfigurations. Choose it over Snyk if you want a broader code review tool that covers quality and security in one place, rather than a dedicated application security platform.
Where it is strong
- High-signal, low false-positive issues with structured feedback on PRs
- Autofix generates verified patches for many issues
- Secrets detection validated against 165+ providers
Where it falls short
- Pricing details are not public, so cost comparison requires a sales call
- No dedicated container or IaC security scanning beyond Terraform and CloudFormation
- Pricing:
- Pricing is not published on the site. A 14-day free trial with up to $50 in bundled AI Review credits is available, no credit card required.
- Switching from Snyk:
- Moving from Snyk means shifting from a security-first platform to a broader code review tool, so you would need to set up DeepSource's PR gates and review workflows from scratch.
- See website
11.Escape
Security & Privacy
The only DAST that works with modern stack and tests business logic
- See website
12.Gecko Security
Security & Privacy
The AI Security Engineer to Find and Fix Vulnerabilities
See more comparisons in Security & Privacy alternatives.
FAQ
Questions about Snyk alternatives
Which alternative is best for small teams or individual developers?
SonarQube has a free tier up to 50k lines of code and a low-cost cloud plan. GitHub Projects is free for unlimited repositories, but it does not scan for vulnerabilities. DeepSource offers a free trial with bundled credits, but pricing is not public.
Which alternatives have transparent pricing?
SonarQube publishes pricing starting at $34 monthly for up to 100k lines of code. GitHub Projects has clear per-user pricing. DeepSource, Mend, Checkmarx, Veracode, Aqua Security, and OpenText do not publish pricing and require contacting sales.
Which alternatives support self-managed or air-gapped environments?
SonarQube offers self-hosted Server editions. Aqua Security works across on-prem, hybrid, multicloud, and air-gapped environments. Other alternatives may not explicitly mention air-gapped support on their sites.
Which alternatives cover AI-generated code and AI agents?
SonarQube works with coding agents like Claude Code, Cursor, and Copilot via MCP server. Mend covers AI components like models and agents, including automated red teaming. Checkmarx includes AI inventory and AI-powered triage.
Which alternative is best for runtime protection in production?
Aqua Security focuses on runtime security for containers, Kubernetes, serverless, and VMs, blocking attacks at execution. Mend offers runtime in-application protection. Snyk also has runtime scanning, but these alternatives emphasize it more.
Last updated November 1, 2026.