Codacy alternatives
9 products compared · Updated November 1, 2026
The short answer
The strongest alternatives to Codacy are DeepSource for AI-assisted teams needing low-noise reviews, SonarQube for enterprises requiring self-hosted compliance, and Snyk for security-first teams focused on supply chain. DeepSource suits AI-heavy workflows, SonarQube fits strict governance needs, and Snyk is best for deep security scanning.
Your shortlist, at a glance
Read the comparisons ↓ SonarQubeFrom $34/mo (100k LOC)Enterprises that need self-hosted code verification with strict compliance and audit trails, or teams that want a single standard applied to both human and AI-written code.
 SnykFrom $25/moTeams that need a security-first platform to validate AI-generated code and manage vulnerabilities across dependencies, containers, and infrastructure.
 GitLabFrom $12/user/moTeams that want a single platform for source control, CI/CD, and security scanning, especially those already using GitLab or needing self-managed deployment.
 SemgrepFrom $30/contributor/mSecurity-conscious engineering teams that need high-signal SAST, SCA, and secrets scanning with AI-assisted triage and remediation.
 CodeClimateFrom $20/contributor/mEngineering leaders who want to use AI assistants to get context-aware answers about their organization's delivery and staffing.
- VVeracodeNot publishedLarge enterprises that need unified application security risk management across code, dependencies, containers, and runtime, with strong compliance and governance features.
 DeepSourceNot publishedTeams that rely heavily on AI-assisted coding and need automated, low-noise code reviews with pre-generated fixes and compliance mapping.
 GreptileSee websiteAI code review agent with complete context of your codebase
 EllipsisSee websiteAI code reviews & bug fixes
About Codacy and its alternatives
Codacy is a code quality and security platform that scans code, containers, and runtime, with AI guardrails for AI-assisted development. It is known for fast scans, low-noise PR feedback, and centralized AI coding policies.
When comparing alternatives, weigh pricing structure (per user, per LOC, or credit-based), deployment options (cloud vs. self-managed), integrations with your Git and IDE tools, support and contract terms, and whether the tool covers code quality, security, or both.
Explore the alternatives
- From $34/mo (100k LOC)
1.SonarQube
Best for: Enterprises that need self-hosted code verification with strict compliance and audit trails, or teams that want a single standard applied to both human and AI-written code.
- Pricing
- From $34/mo (100k LOC)
- Category
- Developer Tools
SonarQube is a code quality and security platform that verifies code across 45+ languages, with SAST, SCA, secrets detection, and quality gates. You would choose it over Codacy if you need self-managed deployment inside your perimeter, air-gapped support, or enterprise-grade governance with auditable evidence for every merge decision.
Where it is strong
- Supports 45+ languages, including enterprise ones like COBOL and ABAP in the Enterprise plan
- Offers both cloud and self-managed (Server) editions, including air-gapped
- Quality gates provide time-stamped, auditable evidence for every merge decision
Where it falls short
- Advanced Security features (SCA, secrets, IaC) require the Enterprise plan
- Pricing is based on lines of code, which can get expensive for large codebases
- Pricing:
- Pricing starts at $34 monthly for analysis of up to 100k LOC, with a free tier for private projects up to 50k LOC. Self-hosted editions are priced per instance per year based on LOC.
- Switching from Codacy:
- Moving from Codacy involves reconfiguring quality profiles and CI/CD integrations, and mapping your existing rules to SonarQube's language-specific profiles.
- From $25/mo
2.Snyk
Best for: Teams that need a security-first platform to validate AI-generated code and manage vulnerabilities across dependencies, containers, and infrastructure.
- Pricing
- From $25/mo
- Category
- Security & Privacy
Snyk is an AI-native security platform that scans code, dependencies, containers, and infrastructure as code, with a focus on securing AI-generated code and governing development agents. Choose Snyk over Codacy if your priority is deep security scanning across the full software supply chain, especially for AI-assisted development, rather than broader code quality and policy enforcement.
Where it is strong
- Free plan includes SCA, SAST, IaC, and container scanning.
- Team plan is affordable for small teams at $25/month.
- Enterprise credits can be used across any capability, offering flexibility.
Where it falls short
- Advanced AI features like AI Pentesting require an Enterprise subscription.
- Test limits on the Free plan may be restrictive for larger projects.
- Pricing:
- Free plan at $0/month, Team plan starting at $25/month for up to 10 developers, and Enterprise pricing with a credit-based model where 1 credit = $1.
- Switching from Codacy:
- Moving from Codacy to Snyk means shifting focus from code quality metrics to security scanning, so you'll need to reconfigure your CI/CD pipelines and adjust your review workflows to prioritize vulnerability detection.
- From $12/user/mo
3.GitLab
Best for: Teams that want a single platform for source control, CI/CD, and security scanning, especially those already using GitLab or needing self-managed deployment.
GitLab is a full DevSecOps platform that includes source control, CI/CD, and security scanning, so it replaces both your code repository and your code quality tool. Choose it over Codacy if you want one platform for planning, coding, and shipping, and you are willing to manage your own pipelines and security policies.
Where it is strong
- Includes source control, CI/CD, and security scanning in one platform
- Free tier supports up to 5 users and 400 compute minutes
- Self-managed and dedicated options for data residency and compliance
Where it falls short
- Security scanning features are mostly in the Ultimate tier, which is more expensive
- AI features require purchasing GitLab Credits add-on, not included in base plans
- Pricing:
- Free plan for up to 5 users. Premium at $12 per user/month. Ultimate at $24 per user/month. GitLab Dedicated and Flex pricing are custom.
- Switching from Codacy:
- Moving from Codacy to GitLab means migrating your repositories and setting up CI/CD pipelines, and you will need to configure security scanning rules within GitLab's own framework.
- From $30/contributor/m
4.Semgrep
Best for: Security-conscious engineering teams that need high-signal SAST, SCA, and secrets scanning with AI-assisted triage and remediation.
- Pricing
- From $30/contributor/m
- Category
- Developer Tools
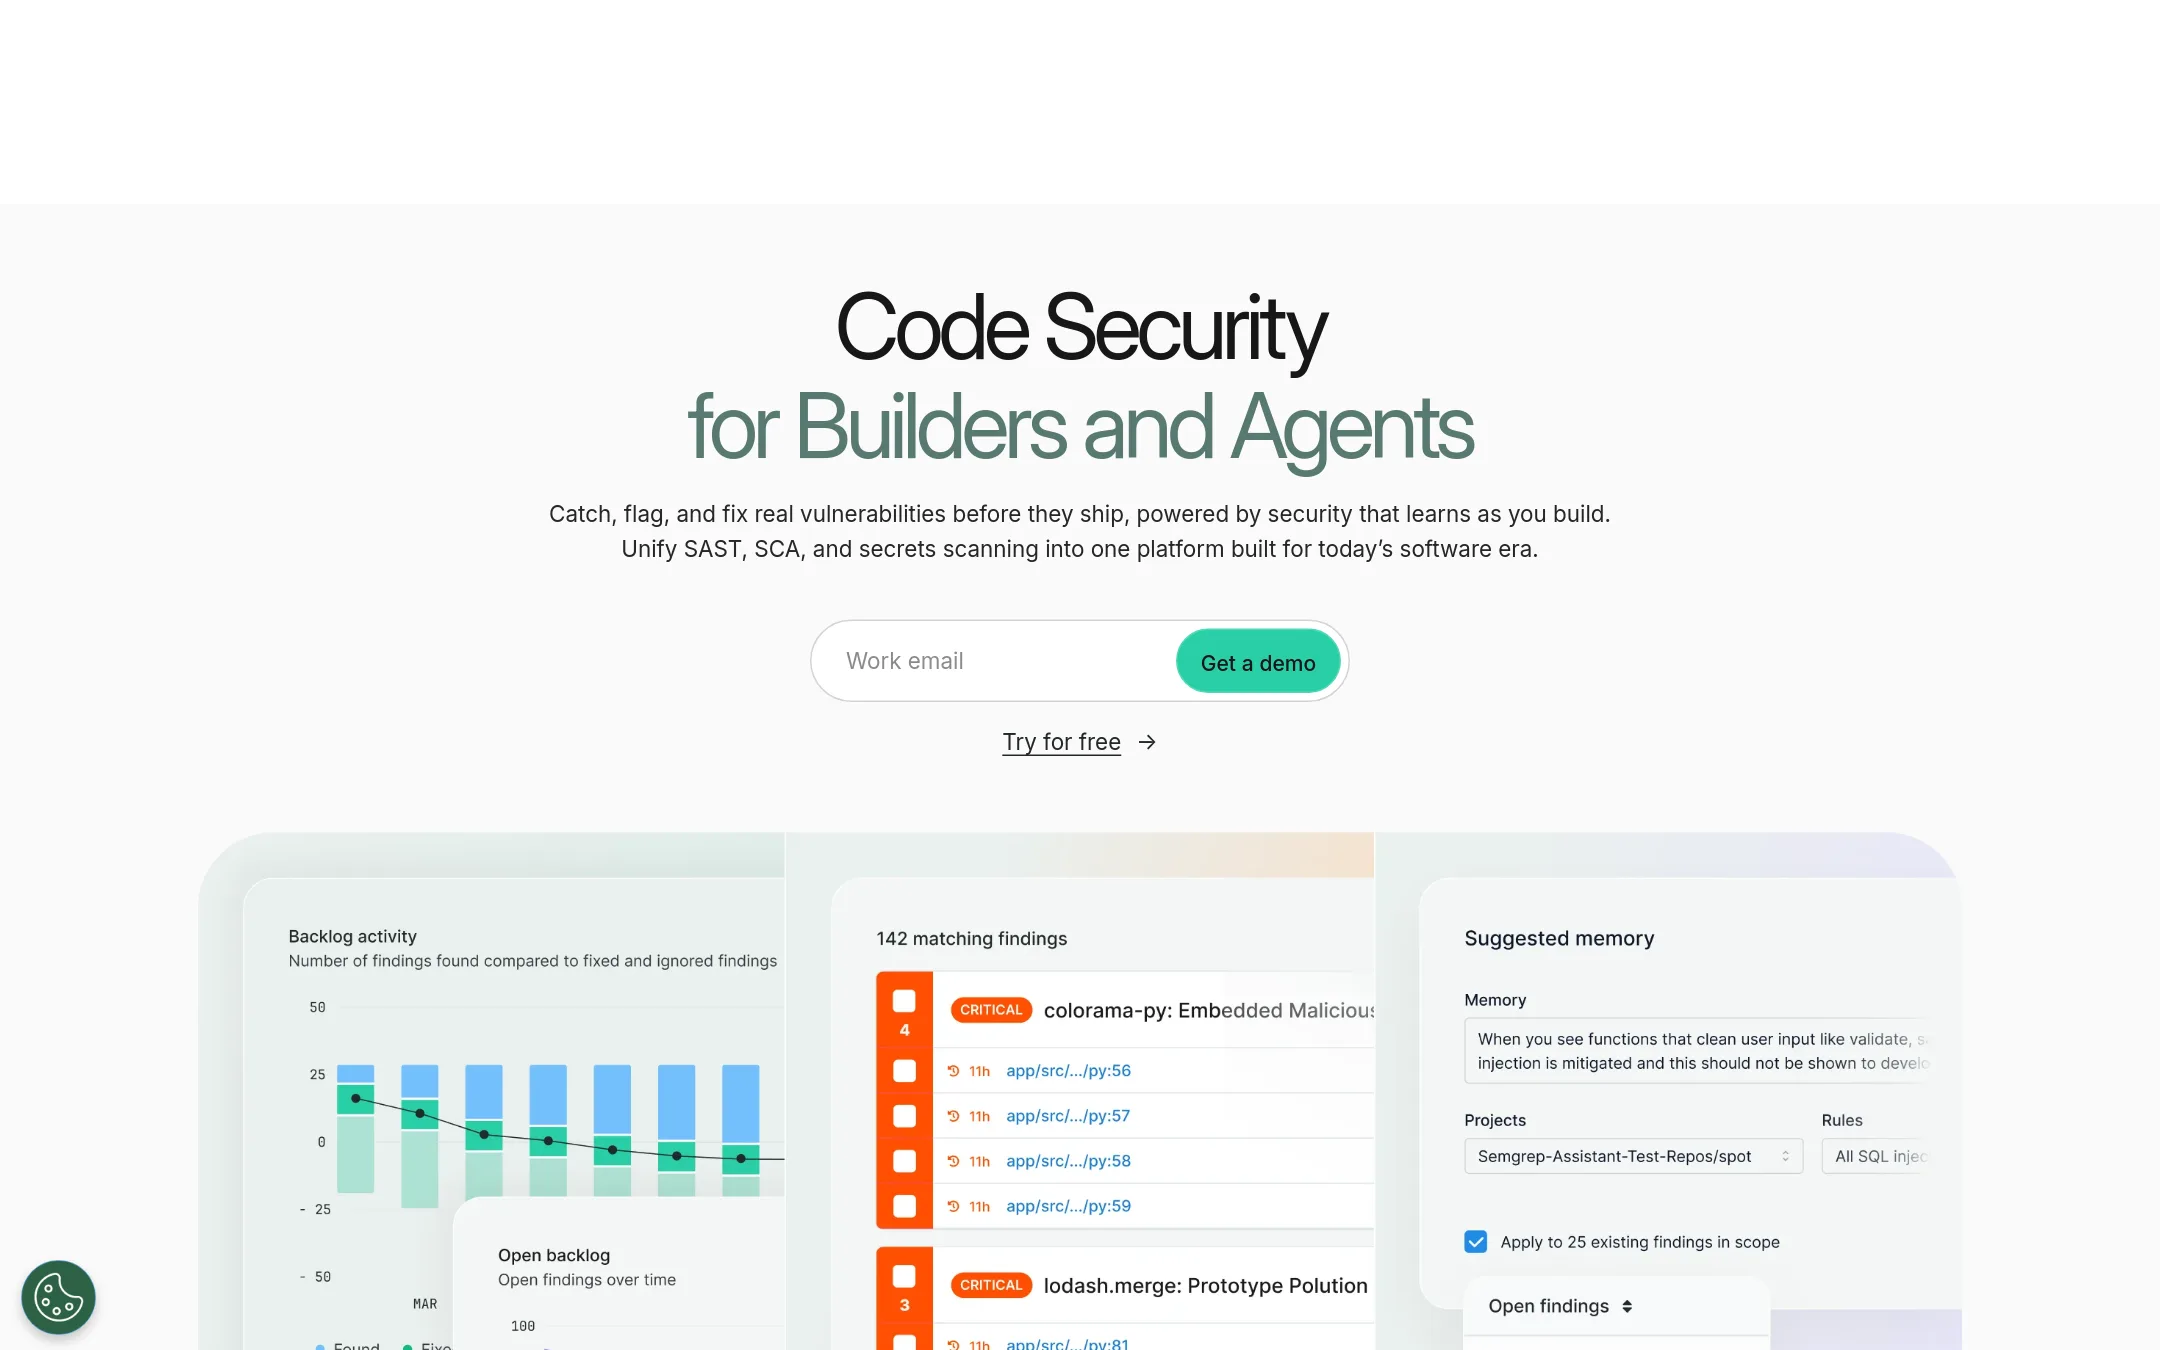
Semgrep is a security-focused platform that combines SAST, SCA, and secrets scanning with AI-assisted detection and remediation. Choose it over Codacy when your priority is application security with low false positives, especially for teams that want to triage and fix vulnerabilities directly in PRs and IDEs.
Where it is strong
- AI-powered detection and triage reduces false positives significantly
- Integrates with GitHub, GitLab, Bitbucket, Azure, and IDEs like VS Code and JetBrains
- Includes malware protection and zero-day incident detection
Where it falls short
- Pricing is per contributor, which can get expensive for large teams
- Focuses on security, so it lacks the broader code quality metrics and coverage automation Codacy offers
- Pricing:
- Free tier scans up to 10 repositories with 10 contributors. Paid plans start at $30/month per contributor for Code or Supply Chain, and $15/month per contributor for Secrets.
- Switching from Codacy:
- Moving from Codacy involves reconfiguring your CI/CD pipelines and PR checks, as Semgrep uses its own rule sets and AI features, but the core scanning workflow is similar.
- From $20/contributor/m
5.CodeClimate
Best for: Engineering leaders who want to use AI assistants to get context-aware answers about their organization's delivery and staffing.
- Pricing
- From $20/contributor/m
- Category
- Developer Tools
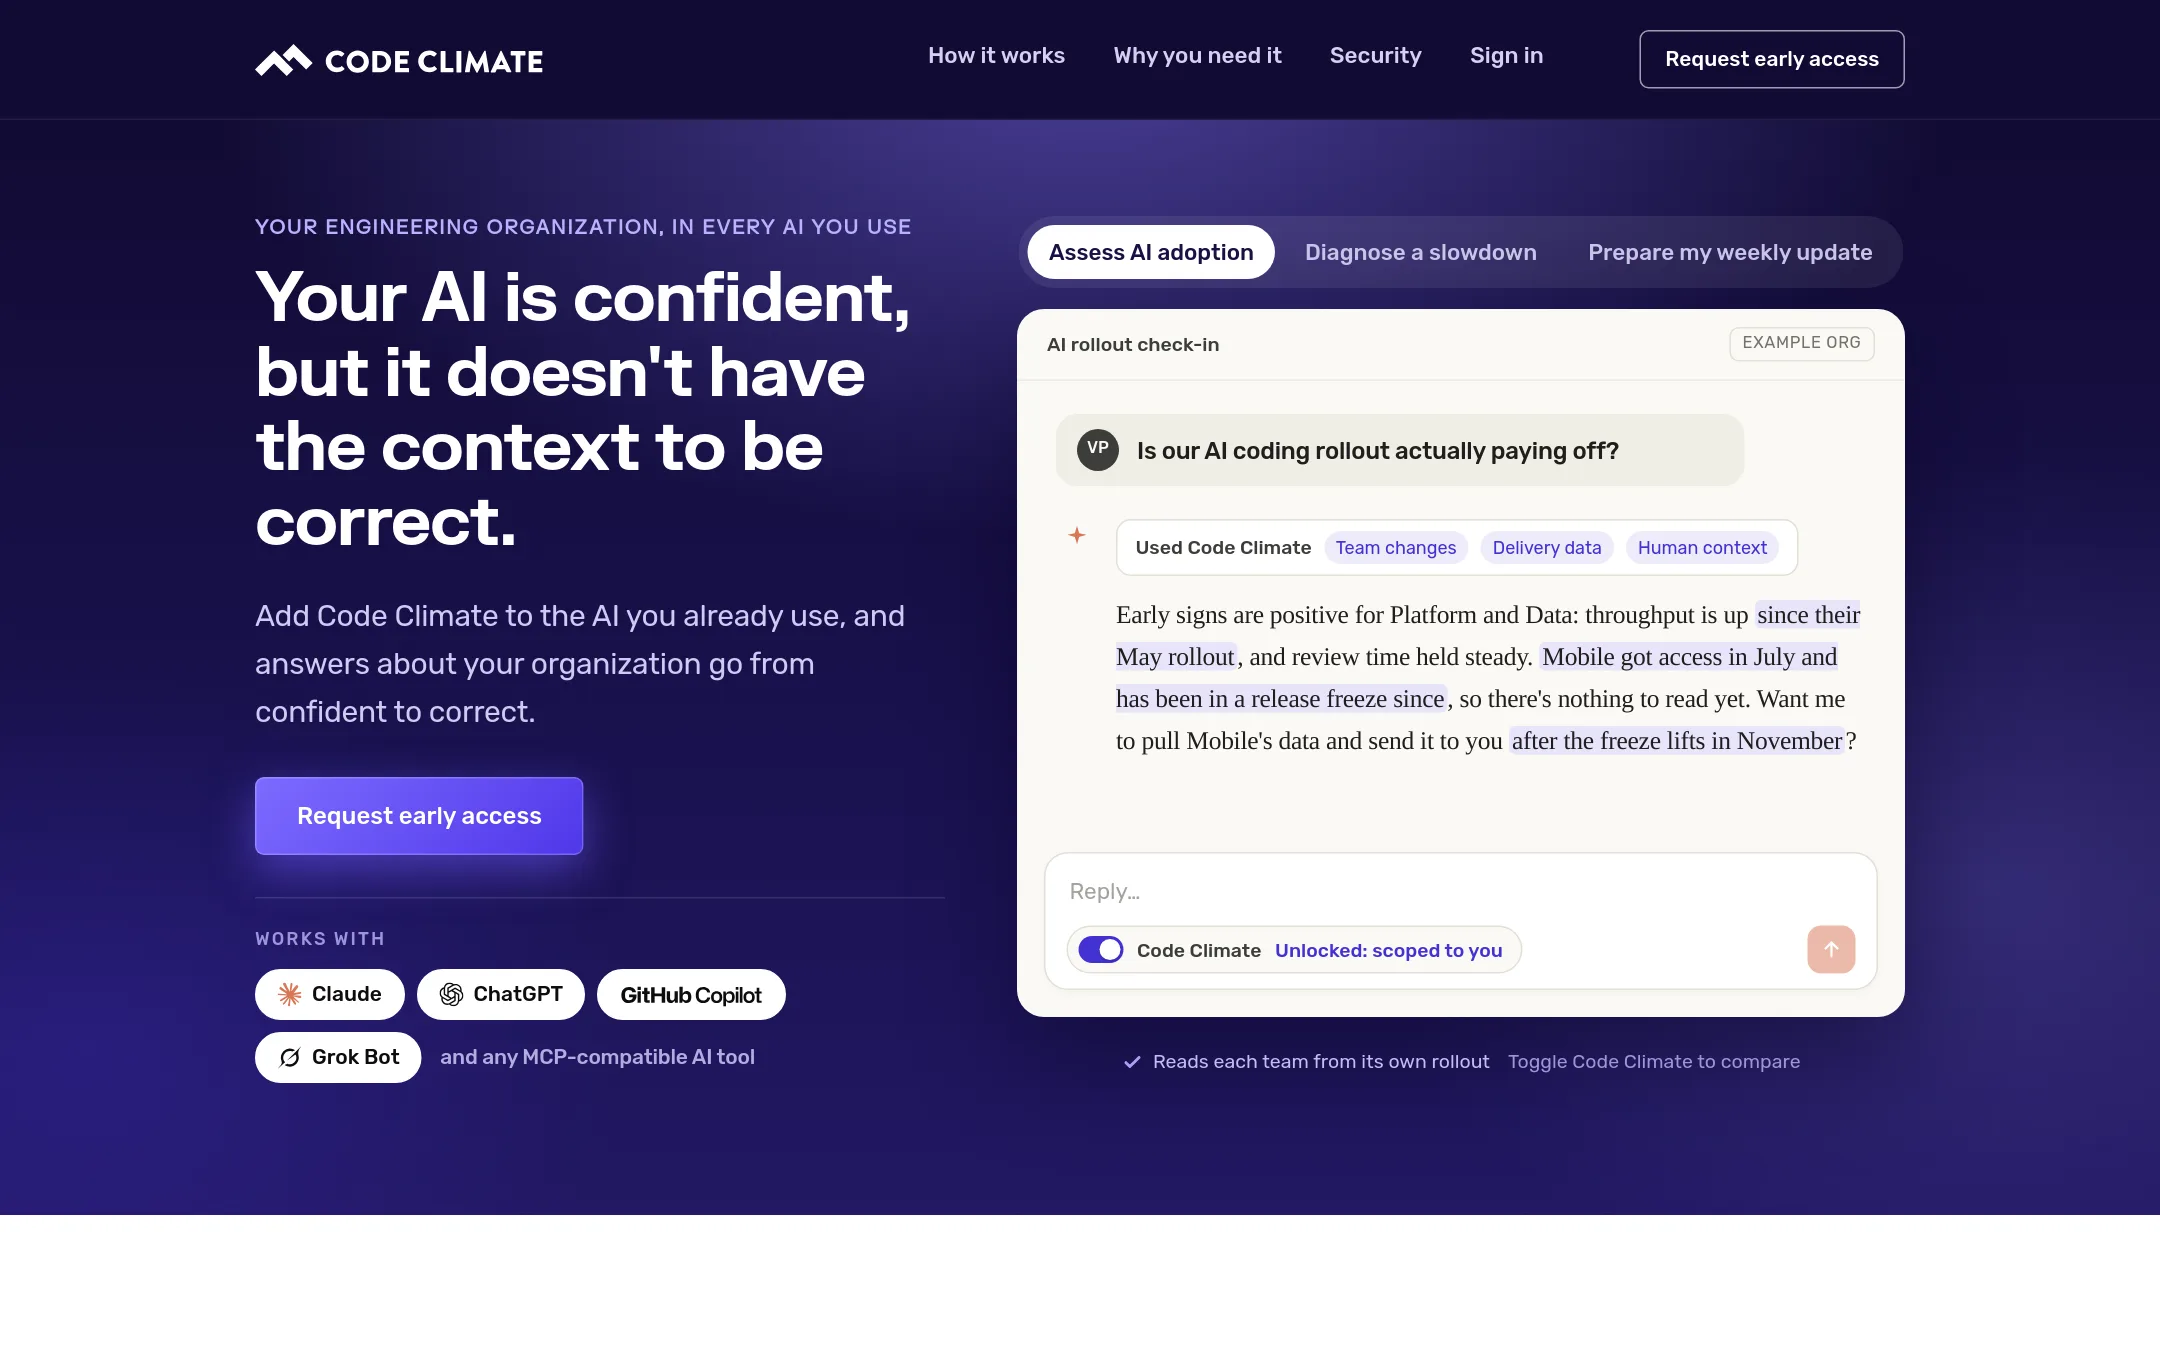
CodeClimate is an engineering intelligence platform that connects your AI tools to your org's data, so you can ask questions about teams, delivery, and initiatives and get answers before your next meeting. Choose it over Codacy if your bottleneck is leadership decisions and resource planning, not code quality scans.
Where it is strong
- Gives AI tools (Claude, ChatGPT, Copilot) org context via MCP
- SOC 2 Type II, SSO, and role-based access
- Free plan for unlimited private contributors
Where it falls short
- Focus is on org-level decisions, not code quality or security scanning
- Pricing is per contributor, which can add up for large teams
- Pricing:
- Free plan includes 1,000 analysis minutes/month. Pro is $20 per contributor per month. Enterprise is $30 per contributor per month with annual plans priced two months free.
- VNot published
6.Veracode
Best for: Large enterprises that need unified application security risk management across code, dependencies, containers, and runtime, with strong compliance and governance features.
- Pricing
- Not published
- Category
- Other
Veracode is an application risk management platform focused on security across the entire SDLC, from code to runtime. Choose it over Codacy if you need enterprise-grade governance, compliance reporting, and supply chain security at scale, rather than a developer-focused code quality and AI policy tool.
Where it is strong
- Scans code, dependencies, containers, and runtime for a full risk picture
- AI-driven fixes and low false-positive rate help developers prioritize real issues
- Built for enterprise governance, compliance, and policy enforcement
Where it falls short
- Pricing is not public, likely enterprise-focused and expensive
- Heavier focus on security than on code quality metrics like test coverage or duplication
- Pricing:
- Pricing is not published on the site.
- Not published
7.DeepSource
Best for: Teams that rely heavily on AI-assisted coding and need automated, low-noise code reviews with pre-generated fixes and compliance mapping.
- Pricing
- Not published
- Category
- Developer Tools
DeepSource is an AI code review platform that combines static analysis with AI agents to catch bugs, security issues, and anti-patterns on pull requests. It also offers Autofix patches, secrets detection, and dependency vulnerability scanning. Choose DeepSource over Codacy if you want a high-signal, low false-positive review engine with structured feedback that can feed directly into your AI coding agent via MCP.
Where it is strong
- 5,000+ deterministic rules plus an AI review agent for high-signal, low false-positive findings
- Autofix provides verified, pre-generated patches for most issues
- Compliance reports mapped to OWASP Top 10 and SANS Top 25
Where it falls short
- Pricing is not transparent. You must contact sales for Team or Enterprise plans
- No runtime testing or container image scanning, which Codacy offers
- Pricing:
- Pricing is not published on the site. A 14-day free trial includes up to $50 in bundled AI Review credits, no credit card required.
- Switching from Codacy:
- Moving from Codacy involves reconfiguring your CI/CD pipeline to use DeepSource's GitHub, GitLab, or Bitbucket integrations, and setting up your own quality gates and coverage thresholds.
- See website
8.Greptile
Developer Tools
AI code review agent with complete context of your codebase
- See website
9.Ellipsis
Developer Tools
AI code reviews & bug fixes
See more comparisons in Developer Tools alternatives.
FAQ
Questions about Codacy alternatives
Which alternative is best for teams using AI coding assistants?
DeepSource is the strongest choice for AI-heavy workflows, offering deterministic rules plus an AI review agent and Autofix patches. It integrates with AI agents via MCP, so findings feed directly into your coding tools. Snyk also focuses on securing AI-generated code, but with a security-first lens.
What is the most cost-effective option for small teams?
GitLab offers a free tier for up to 5 users and 400 compute minutes, making it a low-cost entry point. Snyk's Team plan starts at $25/month for up to 10 developers, which is affordable for small teams. CodeClimate's free plan includes 1,000 analysis minutes per month.
Which alternative supports self-hosted or air-gapped deployment?
SonarQube offers self-managed (Server) editions, including air-gapped support, and GitLab has self-managed and dedicated options. These are suitable for enterprises with strict data residency or compliance requirements. Codacy itself only offers cloud-hosted scans, so these alternatives fill that gap.
How do pricing models differ among these alternatives?
Pricing varies: GitLab charges per user per month, SonarQube charges per lines of code, Snyk uses a credit-based model for Enterprise, and CodeClimate charges per contributor. DeepSource and Veracode do not publish pricing, so you must contact sales. Consider your team size and codebase size when comparing.
Which alternative is best for enterprise compliance and governance?
SonarQube provides quality gates with time-stamped, auditable evidence for every merge decision, ideal for strict compliance. Veracode offers enterprise-grade governance and compliance reporting across the SDLC. GitLab also supports self-managed deployment and audit logs, but security features are mostly in the higher Ultimate tier.
Last updated November 1, 2026.