ComplyDo alternatives
6 products compared · Updated November 13, 2026
The short answer
The three strongest alternatives to ComplyDo are Vanta, Drata and Secureframe. Vanta suits startups and mid-market SaaS companies that need SOC 2 or ISO 27001 quickly with continuous monitoring. Drata suits startups and mid-size SaaS teams that want SOC 2, ISO 27001 or GDPR evidence collected automatically from cloud and HR tools. Secureframe suits software companies pursuing SOC 2 or ISO 27001 that want automated evidence collection and continuous monitoring.
Your shortlist, at a glance
Read the comparisons ↓ VantaNot publishedStartups and mid-market SaaS companies that need SOC 2 or ISO 27001 quickly and want continuous monitoring.
 DrataNot publishedStartups and mid-size SaaS teams that need SOC 2, ISO 27001 or GDPR evidence collected automatically from their cloud and HR tools
 SecureframeFrom $7,500/yearSoftware companies pursuing SOC 2 or ISO 27001 that want automated evidence collection and continuous monitoring
 HyperproofNot publishedSecurity and compliance teams that manage several frameworks at once and want a common control set across the business
- SScrut AutomationNot publishedGrowing SaaS companies that need SOC 2 or ISO 27001 readiness and a faster route through security questionnaires
- EErambaNot publishedSecurity and compliance teams that want self-hosted, open source GRC with a flat annual fee and no per-user limits
About ComplyDo and its alternatives
ComplyDo is a global compliance platform for enterprises. Its site says it maps internal controls against regulations such as DORA and NIS2, tracks regulatory changes through horizon scanning, and manages gaps, product documentation and audit evidence across entities.
When comparing alternatives in this category, weigh the pricing structure, since some vendors publish prices and others require a sales demo. Check which regions and regulations each tool covers, how many integrations it connects to, what support is offered, and the terms of the contract.
Explore the alternatives
- Not published
1.Vanta
Best for: Startups and mid-market SaaS companies that need SOC 2 or ISO 27001 quickly and want continuous monitoring.
- Pricing
- Not published
- Category
- Security & Privacy
Vanta automates SOC 2, ISO 27001, HIPAA, GDPR and several other frameworks, with continuous monitoring, a Trust Center and an AI agent that drafts policies and completes questionnaires. Teams pick it over ComplyDo when the main job is getting audit-ready and answering customer security reviews, especially for startups and mid-market companies with a security focus rather than a broad regulatory map.
Where it is strong
- Covers SOC 2, ISO 27001, HIPAA, GDPR, ISO 42001 and FedRAMP among other frameworks.
- The Vanta Agent drafts policies and completes security questionnaires.
- Includes a public Trust Center to share your security posture with prospects.
Where it falls short
- Its focus is security and privacy frameworks, so product compliance and horizon scanning of new regulations are not part of the listed featu
- Pricing requires a demo request, so you cannot compare costs before talking to sales.
- Pricing:
- Pricing is not published on the site.
- Not published
2.Drata
Best for: Startups and mid-size SaaS teams that need SOC 2, ISO 27001 or GDPR evidence collected automatically from their cloud and HR tools
- Pricing
- Not published
- Category
- Security & Privacy
Drata is a compliance automation platform that connects to your tools, collects audit evidence on its own, and monitors controls continuously. Founders pick it over ComplyDo when the main job is getting SOC 2, ISO 27001 or similar certified and keeping evidence current, rather than mapping regulations like DORA or NIS2 across product documentation.
Where it is strong
- Collects audit evidence automatically from connected tools and monitors controls continuously
- Covers many frameworks, including ISO 27001, ISO 42001, GDPR, HIPAA and PCI DSS, with control mapping across them
- Includes a Trust Center and AI-drafted questionnaire answers to cut sales back-and-forth
Where it falls short
- Its emphasis is security and audit readiness, so regulatory horizon scanning and product compliance checks are not shown on the site
- The site does not list the number or detail of integrations beyond saying it connects to hundreds of tools
- Pricing:
- Pricing is not published on the site.
- From $7,500/year
3.Secureframe
Best for: Software companies pursuing SOC 2 or ISO 27001 that want automated evidence collection and continuous monitoring
- Pricing
- From $7,500/year
- Category
- Security & Privacy
Secureframe automates compliance for SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, NIST and CMMC by collecting evidence, monitoring controls and tracking risk in one place. A company would pick it over ComplyDo if its main need is passing a specific security or privacy audit and keeping evidence current, rather than mapping internal controls across regulations and entities.
Where it is strong
- Automated evidence collection and continuous control monitoring across 300+ native integrations.
- Covers SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, NIST and CMMC, with a purpose-built defense tier.
- Includes a Trust Center and questionnaire automation to speed up customer security reviews.
Where it falls short
- The listed starting price is high for very early-stage teams, and pricing for higher tiers is not fully shown on the page.
- It is oriented toward security audits, so it offers less on multi-entity group compliance and regulatory horizon scanning than ComplyDo.
- Pricing:
- Secureframe lists packages starting at $7,500/year, with Fundamentals and Complete tiers and a custom-priced Defense tier for CMMC.
- Not published
4.Hyperproof
Best for: Security and compliance teams that manage several frameworks at once and want a common control set across the business
- Pricing
- Not published
- Category
- Security & Privacy
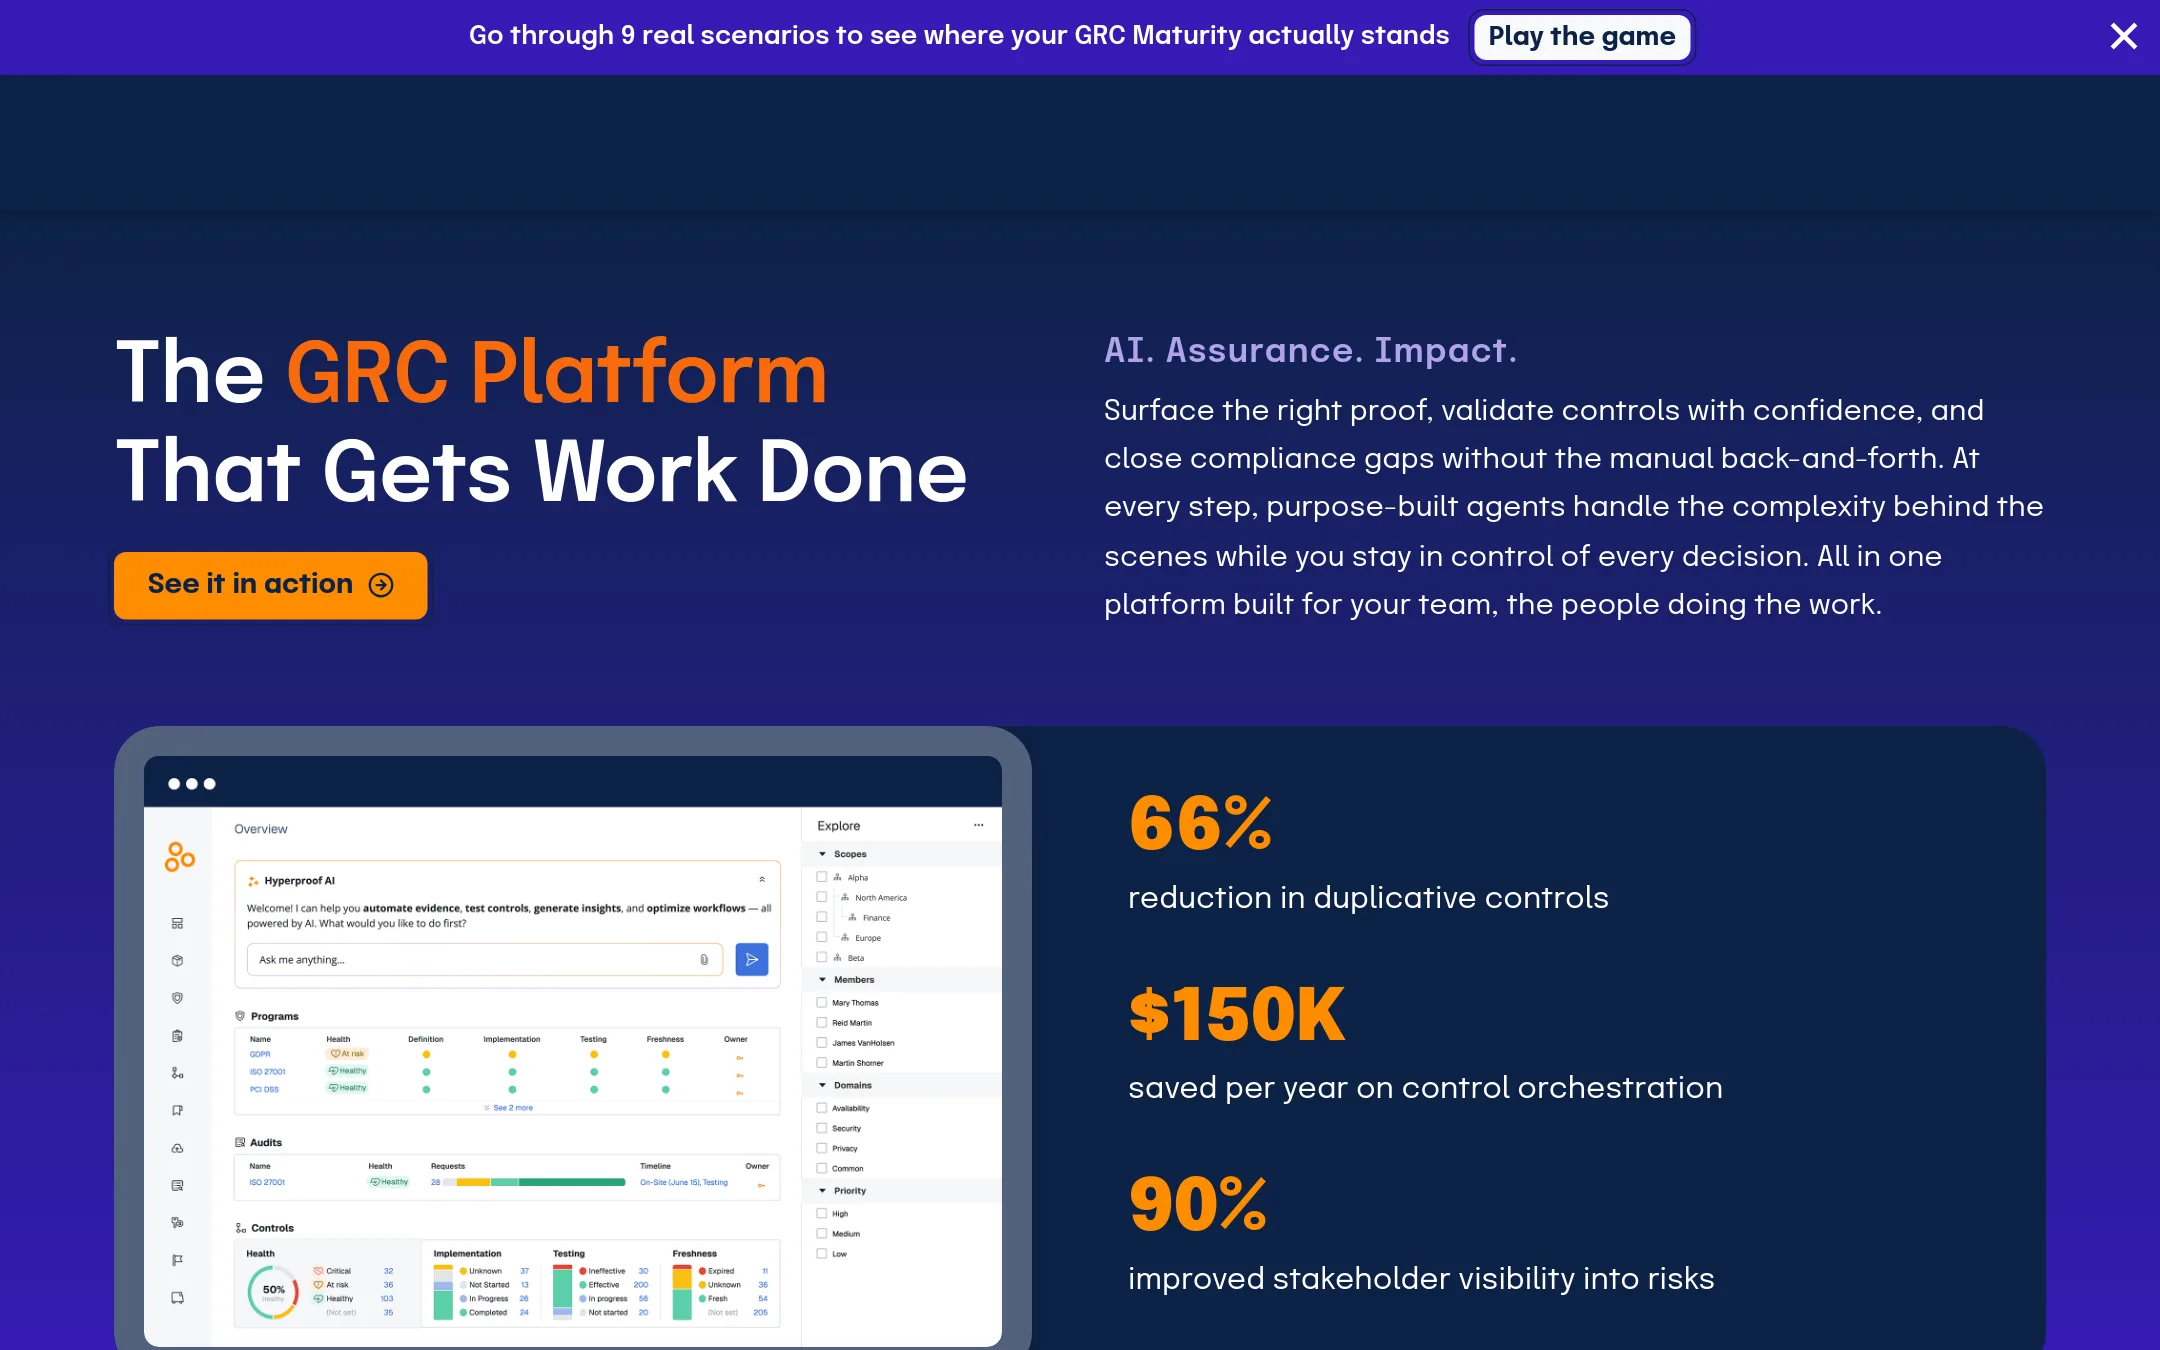
Hyperproof is a GRC platform that centralizes controls, risks, audits, policies, third-party risk and a trust center in one place. Teams pick it over ComplyDo when the main job is running continuous compliance across many frameworks, with a large pre-built library of more than 160 frameworks and a common control set that avoids duplicate work.
Where it is strong
- 160+ pre-built frameworks, the largest library the site cites
- Common control set reduces duplicate controls, with the site citing a 66% reduction
- Covers risk, audit, trust center and third-party risk alongside compliance
Where it falls short
- The site does not describe regulation horizon scanning or product compliance checks the way ComplyDo does
- Its strengths sit in framework and control management, so teams focused on EU product regulation may find less built for that
- Pricing:
- Pricing is not published on the site.
- SNot published
5.Scrut Automation
Best for: Growing SaaS companies that need SOC 2 or ISO 27001 readiness and a faster route through security questionnaires
- Pricing
- Not published
- Category
- Other
Scrut Automation is a compliance platform built around AI agents, which they call Teammates. The Teammates draft policies, collect evidence from 150+ integrations, check vendor risk, and prepare audit packages, with a human reviewing each output. Teams pick it over ComplyDo when the main need is continuous evidence collection and audit prep across many frameworks, and when they want questionnaire answers and a trust center built from live compliance data.
Where it is strong
- Pulls evidence automatically from AWS, GitHub, Okta and 150+ other tools
- Covers 70+ frameworks and can reuse up to 80% of existing controls through a unified control framework
- Includes a trust center and drafts security questionnaire answers from live compliance data
Where it falls short
- The site emphasizes security and audit work, so regulatory horizon scanning and product compliance checks are not described
- Heavy reliance on AI agents means teams need to review outputs closely before publishing
- Pricing:
- Pricing is not published on the site.
- ENot published
6.Eramba
Best for: Security and compliance teams that want self-hosted, open source GRC with a flat annual fee and no per-user limits
- Pricing
- Not published
- Category
- Other
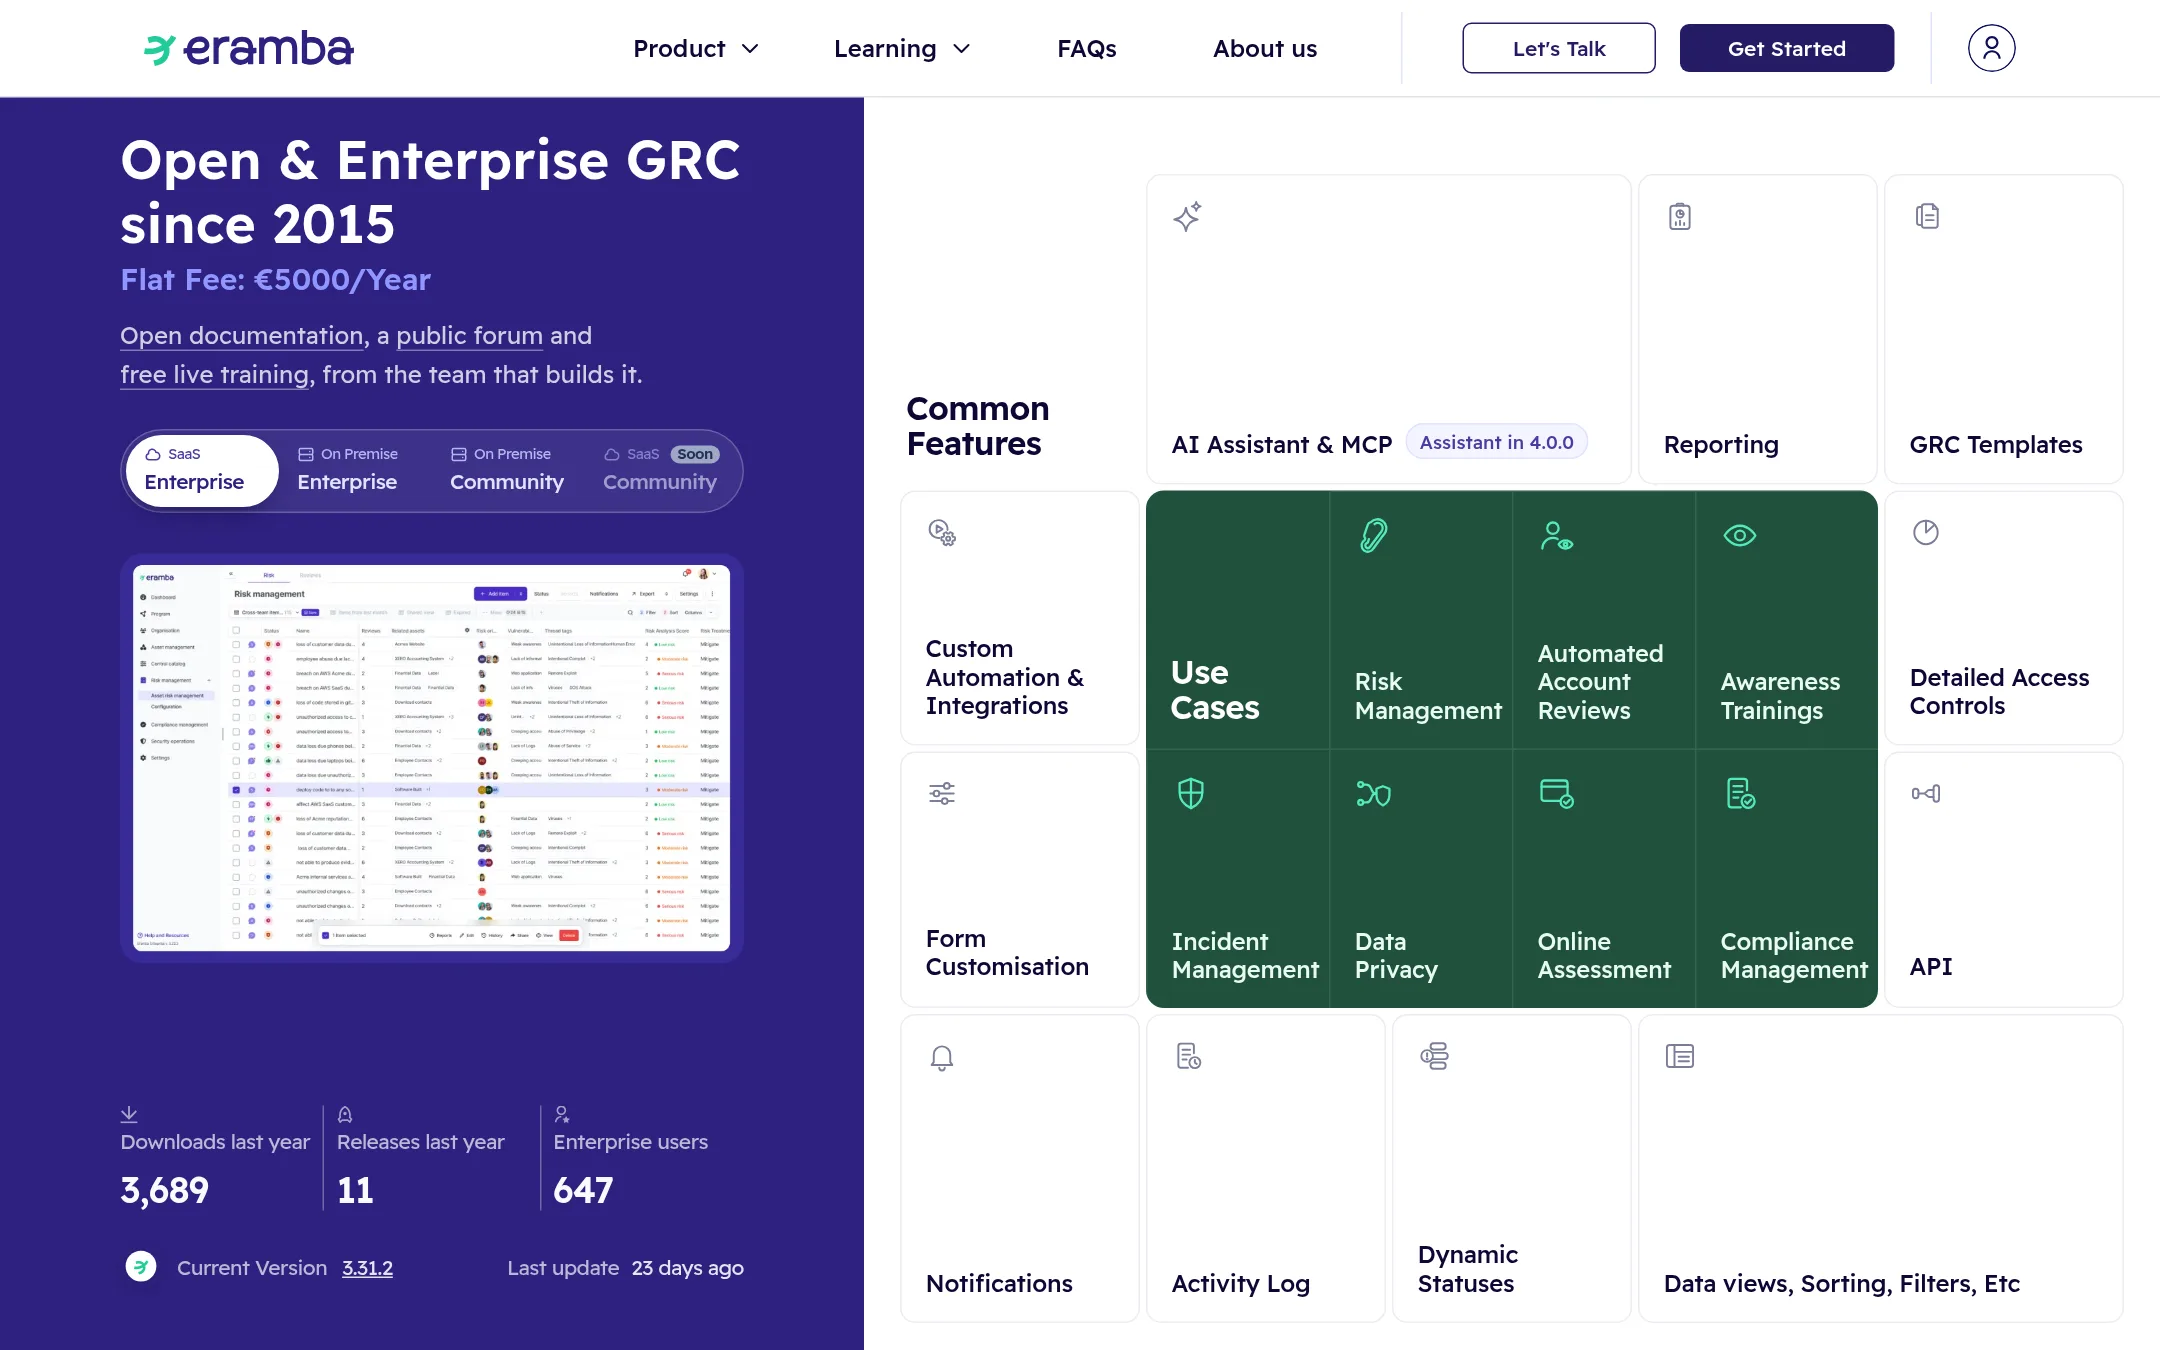
Eramba is an open source GRC platform covering risk, compliance, incidents and privacy. Teams choose it over ComplyDo when they want to self-host, want a flat yearly fee instead of per-user or per-framework pricing, or prefer a tool they can read and extend. Its free Community edition lets a team test it before committing.
Where it is strong
- One flat yearly fee covers unlimited users and all included modules
- A free Community edition with no user or time limit to try first
- Open documentation, a public forum and free live training from the core team
Where it falls short
- Covers risk, compliance, incidents and privacy, but the site does not show the regulatory mapping depth ComplyDo advertises, such as 50+ reg
- No horizon scanning, product compliance or AI assistant features are described on the site
- Pricing:
- Pricing is not published on the site.
See more comparisons in Finance & Accounting alternatives.
FAQ
Questions about ComplyDo alternatives
What is ComplyDo best known for?
According to its site, ComplyDo is known for mapping internal controls against 50+ regulations, including DORA and NIS2, and for horizon scanning that flags new regulations on the day they are published. It also covers product compliance checks and multi-entity management for groups.
Which alternative is best for getting SOC 2 or ISO 27001 quickly?
Vanta suits startups and mid-market SaaS companies that need SOC 2 or ISO 27001 quickly and want continuous monitoring. Drata and Secureframe are also built around automated evidence collection for these audits.
Which alternatives publish their pricing?
Secureframe lists packages starting at $7,500 per year. Vanta, Drata, Hyperproof, Scrut Automation and Eramba do not publish pricing on their sites, so you will need to request a demo or quote to compare costs.
Is there a self-hosted or open source option?
Yes. Eramba is an open source GRC platform that covers risk, compliance, incidents and privacy, and can be self-hosted. It charges one flat yearly fee covering unlimited users and offers a free Community edition to test first.
Which alternative is best for managing many frameworks at once?
Hyperproof suits security and compliance teams that manage several frameworks at once, citing a library of more than 160 pre-built frameworks and a common control set. Scrut Automation is another option, covering 70+ frameworks and reusing up to 80% of existing controls.
Last updated November 13, 2026.