Delve alternatives
8 products compared · Updated November 20, 2026
The short answer
Vanta suits startups and mid-market teams that want compliance, risk and vendor reviews in one platform. Secureframe suits defense contractors that need CMMC 2.0 and CUI protection. Thoropass suits growing companies that need a licensed auditor to attest to several frameworks, such as SOC 2 and ISO 27001 together.
Your shortlist, at a glance
Read the comparisons ↓ VantaNot publishedStartups and mid-market security teams that want compliance, risk and vendor reviews managed in one platform
 DrataNot publishedGrowing companies that need one system to run compliance, vendor risk and policy management across several frameworks
 SecureframeFrom $7,500/yearDefense contractors that need CMMC 2.0 compliance and CUI protection
- SSprintoNot publishedGrowing SaaS teams that want continuous compliance monitoring and unified risk management in one platform
- SScrut AutomationNot publishedGrowing companies that need ongoing GRC across several frameworks and want evidence collection, risk tracking and vendor review in one platform
 HyperproofNot publishedEnterprise security and compliance teams that manage many frameworks and need a shared control set across business units
- TThoropassNot publishedGrowing companies that need a licensed auditor to attest to several frameworks, such as SOC 2 and ISO 27001 together
- CComp AINot publishedStartups and growing companies that need SOC 2, ISO 27001, HIPAA or GDPR and want automated evidence collection with audit and pentest included
About Delve and its alternatives
Delve is a compliance platform that uses AI agents to collect evidence, draft controls and answer security questionnaires. According to its site, it is known for automating compliance busywork, for 1:1 Slack access to security experts, and for a free trust report that helps companies share their compliance documentation with prospects.
When comparing alternatives in this category, weigh the pricing structure first, since many vendors do not publish prices and require a demo or sales call. Check which frameworks and regions each product covers, how many integrations it offers for automated evidence collection, and whether it includes a trust center, questionnaire automation and third-party risk management. Also compare the support model, including whether you get human experts or only software, and the contract terms and add-on fees.
Explore the alternatives
- Not published
1.Vanta
Best for: Startups and mid-market security teams that want compliance, risk and vendor reviews managed in one platform
- Pricing
- Not published
- Category
- Security & Privacy
Vanta automates compliance for frameworks such as SOC 2, ISO 27001, HIPAA, GDPR and FedRAMP, with continuous monitoring, a trust center and an AI agent for drafting policies and questionnaires. Teams pick it over Delve when they want a broader platform that also covers risk, third-party risk and AI governance in one place.
Where it is strong
- Covers many frameworks, including SOC 2, ISO 27001, HIPAA, GDPR, ISO 42001 and FedRAMP
- Adds risk, third-party risk and AI governance modules beyond core compliance
- Includes a trust center for sharing security posture with customers
Where it falls short
- Pricing requires a demo request, so costs are not visible upfront
- Optional add-ons are priced separately from the base plan
- Pricing:
- Pricing is not published on the site. The pricing page asks you to book a demo for a personalized plan, and one add-on is listed at 144 per year with 25 per year included.
- Not published
2.Drata
Best for: Growing companies that need one system to run compliance, vendor risk and policy management across several frameworks
- Pricing
- Not published
- Category
- Security & Privacy
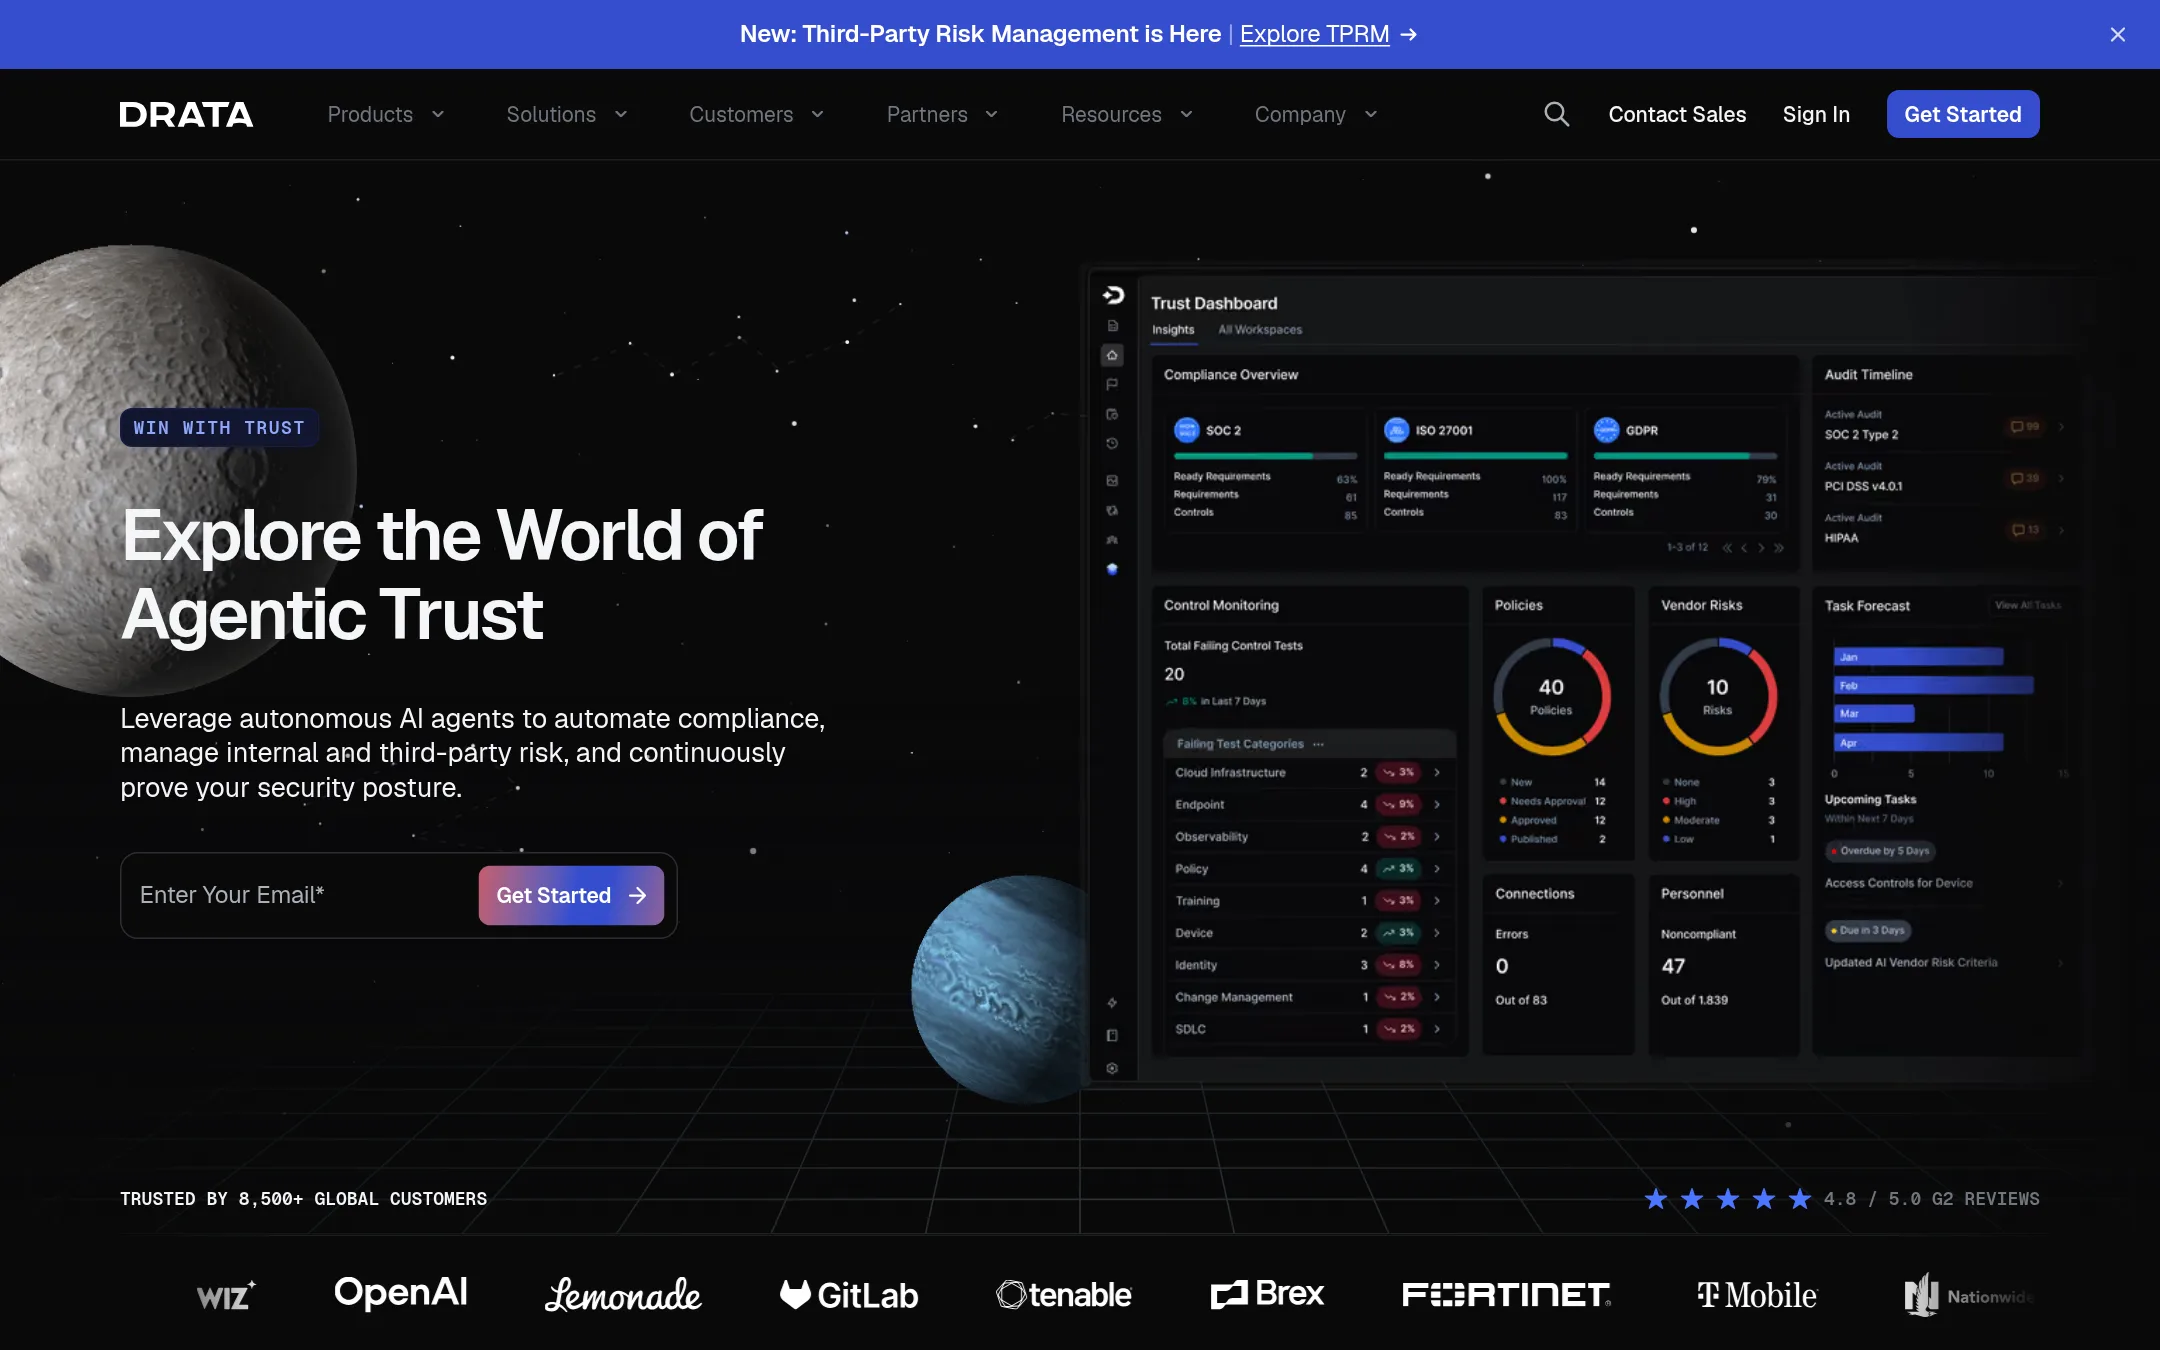
Drata is an AI-native compliance platform that automates control mapping, evidence collection and continuous monitoring across frameworks like SOC 2, ISO 27001, GDPR, HIPAA and PCI DSS. Teams often pick it over Delve when they want a broader GRC system that also covers internal risk, third-party risk and governance of AI agents.
Where it is strong
- Maps controls once and reuses them across many frameworks such as ISO 27001, GDPR and HIPAA
- Includes third-party risk management and AI-driven vendor assessments
- Trust Center and questionnaire automation help sales and security share the same answers
Where it falls short
- Pricing is not published, so budgeting requires a sales conversation
- The site emphasizes broad GRC scope, which may be more than a small startup needs for a first SOC 2
- Pricing:
- Pricing is not published on the site.
- From $7,500/year
3.Secureframe
Best for: Defense contractors that need CMMC 2.0 compliance and CUI protection
- Pricing
- From $7,500/year
- Category
- Security & Privacy
Secureframe automates evidence collection, continuous monitoring, and policy work for SOC 2, ISO 27001, HIPAA, GDPR, and CMMC, with a trust center for sharing your security posture. Teams pick it over Delve when they need defense or CMMC support, a larger integration library, or built-in third-party risk management.
Where it is strong
- Covers CMMC, SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, and NIST
- Offers 300+ native integrations for automated evidence collection
- Includes a trust center, questionnaire automation, and third-party risk management
Where it falls short
- Starting price is $7,500 per year, which is high for early-stage startups
- Advanced features such as SSO, SCIM, and custom integrations sit in higher tiers
- Pricing:
- Pricing starts at $7,500 per year for the Fundamentals package, and the Complete and CMMC tiers are priced higher.
- SNot published
4.Sprinto
Best for: Growing SaaS teams that want continuous compliance monitoring and unified risk management in one platform
- Pricing
- Not published
- Category
- Other
Sprinto is an autonomous trust platform for compliance, risk and GRC, with real-time monitoring and continuous compliance. Teams pick it when they want ongoing control monitoring and unified risk management in one place, rather than a compliance partner with Slack support.
Where it is strong
- Real-time monitoring of controls
- Continuous compliance rather than point-in-time checks
- Covers risk management alongside compliance
Where it falls short
- The site does not describe Slack-based expert support like Delve offers
- Pricing is not published, so cost comparison needs a sales conversation
- Pricing:
- Pricing is not published on the site.
- SNot published
5.Scrut Automation
Best for: Growing companies that need ongoing GRC across several frameworks and want evidence collection, risk tracking and vendor review in one platform
- Pricing
- Not published
- Category
- Other
Scrut Automation is a compliance platform that uses AI agents to draft policies, collect evidence from over 150 integrations, flag control drift, and answer security questionnaires. A team would pick it over Delve when they want continuous monitoring, a live risk register, vendor risk management and a trust center alongside compliance, or when they already work in MCP-compatible tools like Claude or Cursor.
Where it is strong
- Pulls evidence automatically from 150+ tools, including AWS, GitHub and Okta
- Maps controls across 70+ frameworks and lets teams reuse existing controls
- Includes a live risk register, vendor risk assessment and a branded trust center
Where it falls short
- The site does not say how Scrut handles human-led compliance support the way Delve offers 1:1 Slack access to security experts
- Its homepage lists a broad set of products, so a small team may find it heavier to set up than a single-purpose tool
- Pricing:
- Pricing is not published on the site.
- Not published
6.Hyperproof
Best for: Enterprise security and compliance teams that manage many frameworks and need a shared control set across business units
- Pricing
- Not published
- Category
- Security & Privacy
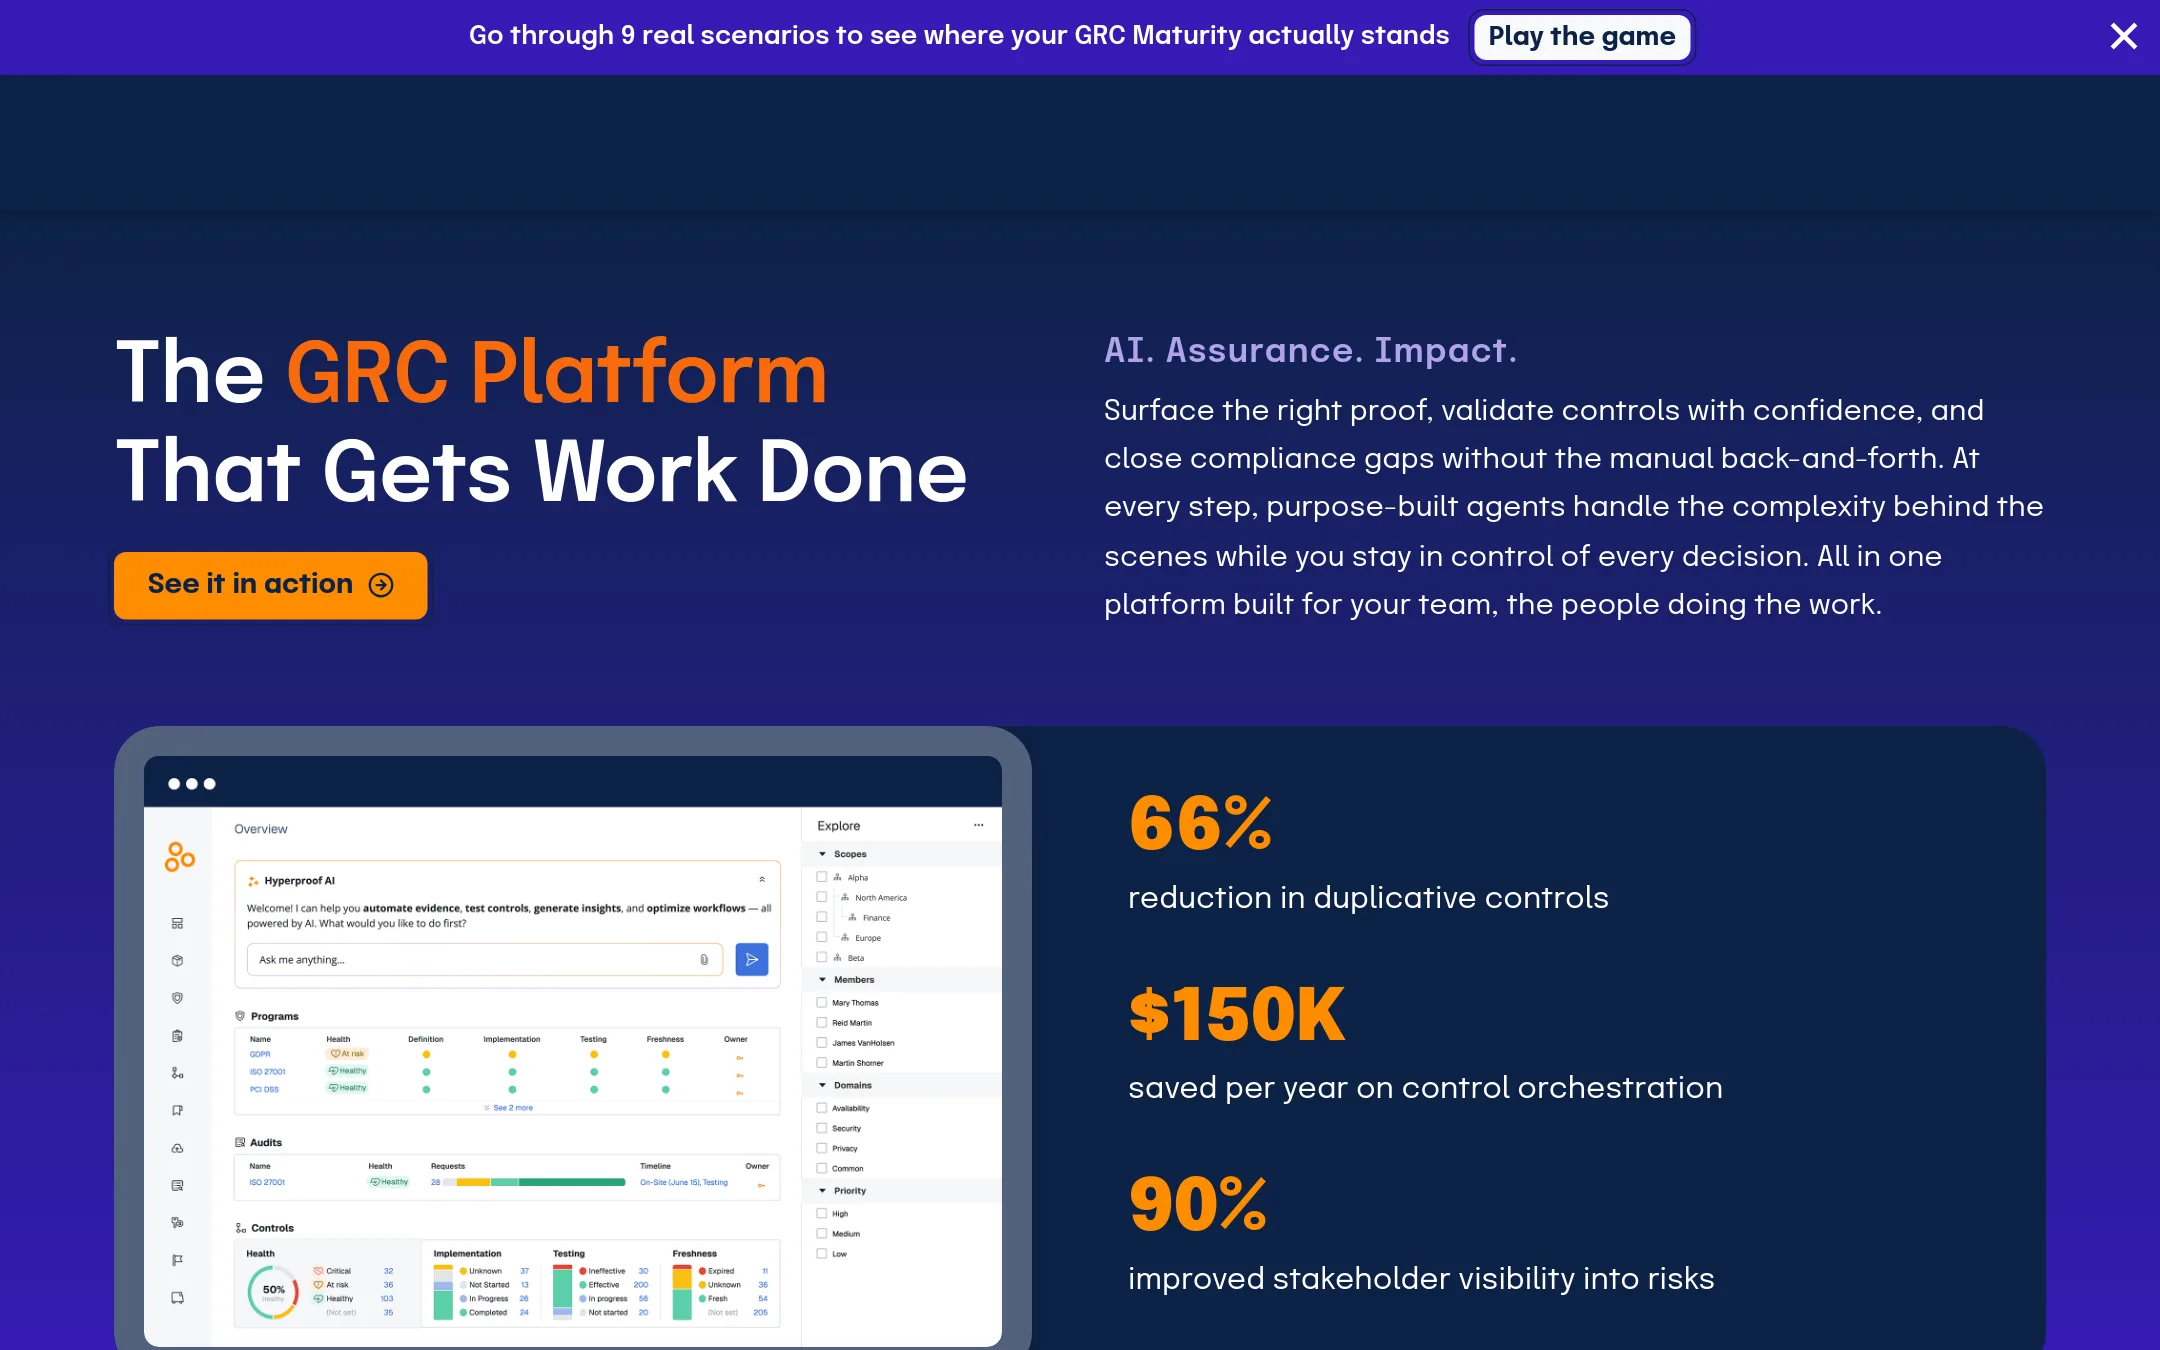
Hyperproof is a GRC platform covering compliance, risk, audit, trust, third-party risk and governance from one place, with AI agents that map controls and gather proof. Teams pick it over Delve when they run many frameworks across several business units and want a shared control set, or when they need a platform that a FedRAMP-bound organization can use.
Where it is strong
- Lists over 160 pre-built frameworks in its library.
- Maps one control set to many frameworks to cut duplicate work, which the site claims reduces duplicative controls by 66%.
- Runs in a FedRAMP Certified Class C (Rev5) environment.
Where it falls short
- Its pitch is a platform for internal GRC teams, not the hands-on expert Slack support Delve advertises.
- The site does not describe a free trust report or a startup-focused onboarding path.
- Pricing:
- Pricing is not published on the site.
- TNot published
7.Thoropass
Best for: Growing companies that need a licensed auditor to attest to several frameworks, such as SOC 2 and ISO 27001 together
- Pricing
- Not published
- Category
- Other
Thoropass is an audit firm backed by a platform, so it delivers the audit itself rather than only organizing your prep. Choose it over Delve when you want a licensed auditor to issue the attestation and to reuse evidence across SOC 2, ISO 27001, HIPAA, PCI DSS and other frameworks.
Where it is strong
- A licensed audit firm performs the independent assessment, not just a software tool
- Evidence and controls are mapped across overlapping frameworks to cut duplicate work
- Covers HITRUST, PCI DSS and HIPAA on one platform
Where it falls short
- Pricing is not shown on the site, so you need to request a quote
- The site does not describe Slack-based expert support the way Delve does
- Pricing:
- Pricing is not published on the site.
- CNot published
8.Comp AI
Best for: Startups and growing companies that need SOC 2, ISO 27001, HIPAA or GDPR and want automated evidence collection with audit and pentest included
- Pricing
- Not published
- Category
- Other
Comp AI automates SOC 2, ISO 27001, HIPAA and GDPR work with 580+ integrations, and its site says more than 1,000 companies use it. Teams pick it when they want audit-ready compliance handled by automation, with audit and pentest included.
Where it is strong
- Covers SOC 2, ISO 27001, HIPAA and GDPR
- Connects to 580+ integrations for evidence collection
- Includes audit and pentest in the offering
Where it falls short
- Pricing depends on scope and requires a sales call to see
- The site does not describe a free trust report like Delve's
- Pricing:
- Pricing is not published on the site.
See more comparisons in Security & Privacy alternatives.
FAQ
Questions about Delve alternatives
Which alternative is best for a startup pursuing its first SOC 2?
Vanta and Comp AI both target startups and growing companies that need SOC 2, with automated evidence collection and audit support. Comp AI also states that audit and pentest are included in its offering. Pricing for both requires a sales conversation, so request quotes before deciding.
Which alternative should a defense contractor consider?
Secureframe is built for defense contractors that need CMMC 2.0 compliance and CUI protection. It also covers SOC 2, ISO 27001, HIPAA and NIST. Its Fundamentals package starts at $7,500 per year, and advanced features sit in higher tiers.
Which alternative gives a licensed auditor who issues the attestation?
Thoropass is an audit firm backed by a platform, so a licensed auditor performs the independent assessment rather than only organizing your preparation. It covers SOC 2, ISO 27001, HIPAA, PCI DSS and HITRUST. Pricing is not shown on the site, so you will need to request a quote.
Which alternative fits an enterprise that manages many frameworks across business units?
Hyperproof lists over 160 pre-built frameworks and maps one control set across them to reduce duplicate work. It runs in a FedRAMP Certified Class C (Rev5) environment. Its pitch is a platform for internal GRC teams rather than hands-on expert support, and pricing is not published.
Is pricing available for these alternatives?
Only Secureframe publishes a starting price, at $7,500 per year for its Fundamentals package. Vanta lists one add-on at 144 per year, but its base pricing requires a demo request. The other entries, including Drata, Hyperproof, Sprinto, Thoropass, Scrut Automation and Comp AI, do not publish pricing on their sites.
Last updated November 20, 2026.