
Flashpoint alternatives
12 products compared · Updated November 2, 2026
The short answer
For AI-native threat intelligence with autonomous response, Cyble is the strongest alternative. For automated OSINT-to-briefing workflows with deep citations, Feedly is the best fit. For real-time physical security and executive protection alerts, ThreatConnect is the top choice.
Your shortlist, at a glance
Read the comparisons ↓ Recorded FutureCustom quoteSecurity teams that want automated, machine-speed threat intelligence across cyber operations, digital risk, third-party risk, and payment fraud.
 CrowdStrikeFrom $4.99/endpoint/moSecurity teams that want endpoint protection, identity security, and threat intelligence in one platform, rather than a standalone intelligence feed.
 AnomaliNot publishedEnterprise SOCs and public-sector teams that want to automate triage and response with governed AI agents while keeping human approval for consequential actions.
 Digital Shadows (now ReliaQuest)Not publishedSecurity operations teams that want to automate Tier 1 and Tier 2 alert handling and reduce mean time to contain threats.
 Intel 471Not publishedSecurity teams that want HUMINT-centric threat intelligence and 700+ ready-built hunt packages tied to active threat actors.
 CybleNot publishedEnterprises and government agencies that want AI-native threat intelligence with dark web monitoring, attack surface management, and autonomous response in one platform.
 FeedlyNot publishedCTI teams that need to quickly research threats and generate tailored briefings for stakeholders, with AI grounded in current sources.
 OverwatchSee websiteEnterprise software for strategic, risk, and cyber fraud intelligence
 TRM LabsSee websiteTRM is building a safer financial system for billions of people.
 ChainalysisSee websiteBlockchain intelligence for investigations, risk, and security
 EllipticSee websiteBlockchain analytics for crypto compliance, risk management and investigations.
 Group-IBNot publishedSecurity and fraud teams that want unified cyber and fraud protection with shared data and detection logic.
About Flashpoint and its alternatives
Flashpoint is a threat intelligence platform known for industry-best data from open and dark web sources, expert analyst insight, and AI-enhanced analysis. It covers cyber threat intelligence, vulnerability intelligence, physical security, fraud prevention, and national security, trusted by global organizations.
When comparing alternatives, weigh pricing structure (per endpoint vs. custom quotes), regional availability, integrations with your existing security stack, support quality, and contract terms. Most alternatives do not publish pricing, so expect sales conversations and consider whether you need a full platform or a focused intelligence feed.
Explore the alternatives
- Custom quote
1.Recorded Future
Best for: Security teams that want automated, machine-speed threat intelligence across cyber operations, digital risk, third-party risk, and payment fraud.
- Pricing
- Custom quote
- Category
- Security & Privacy
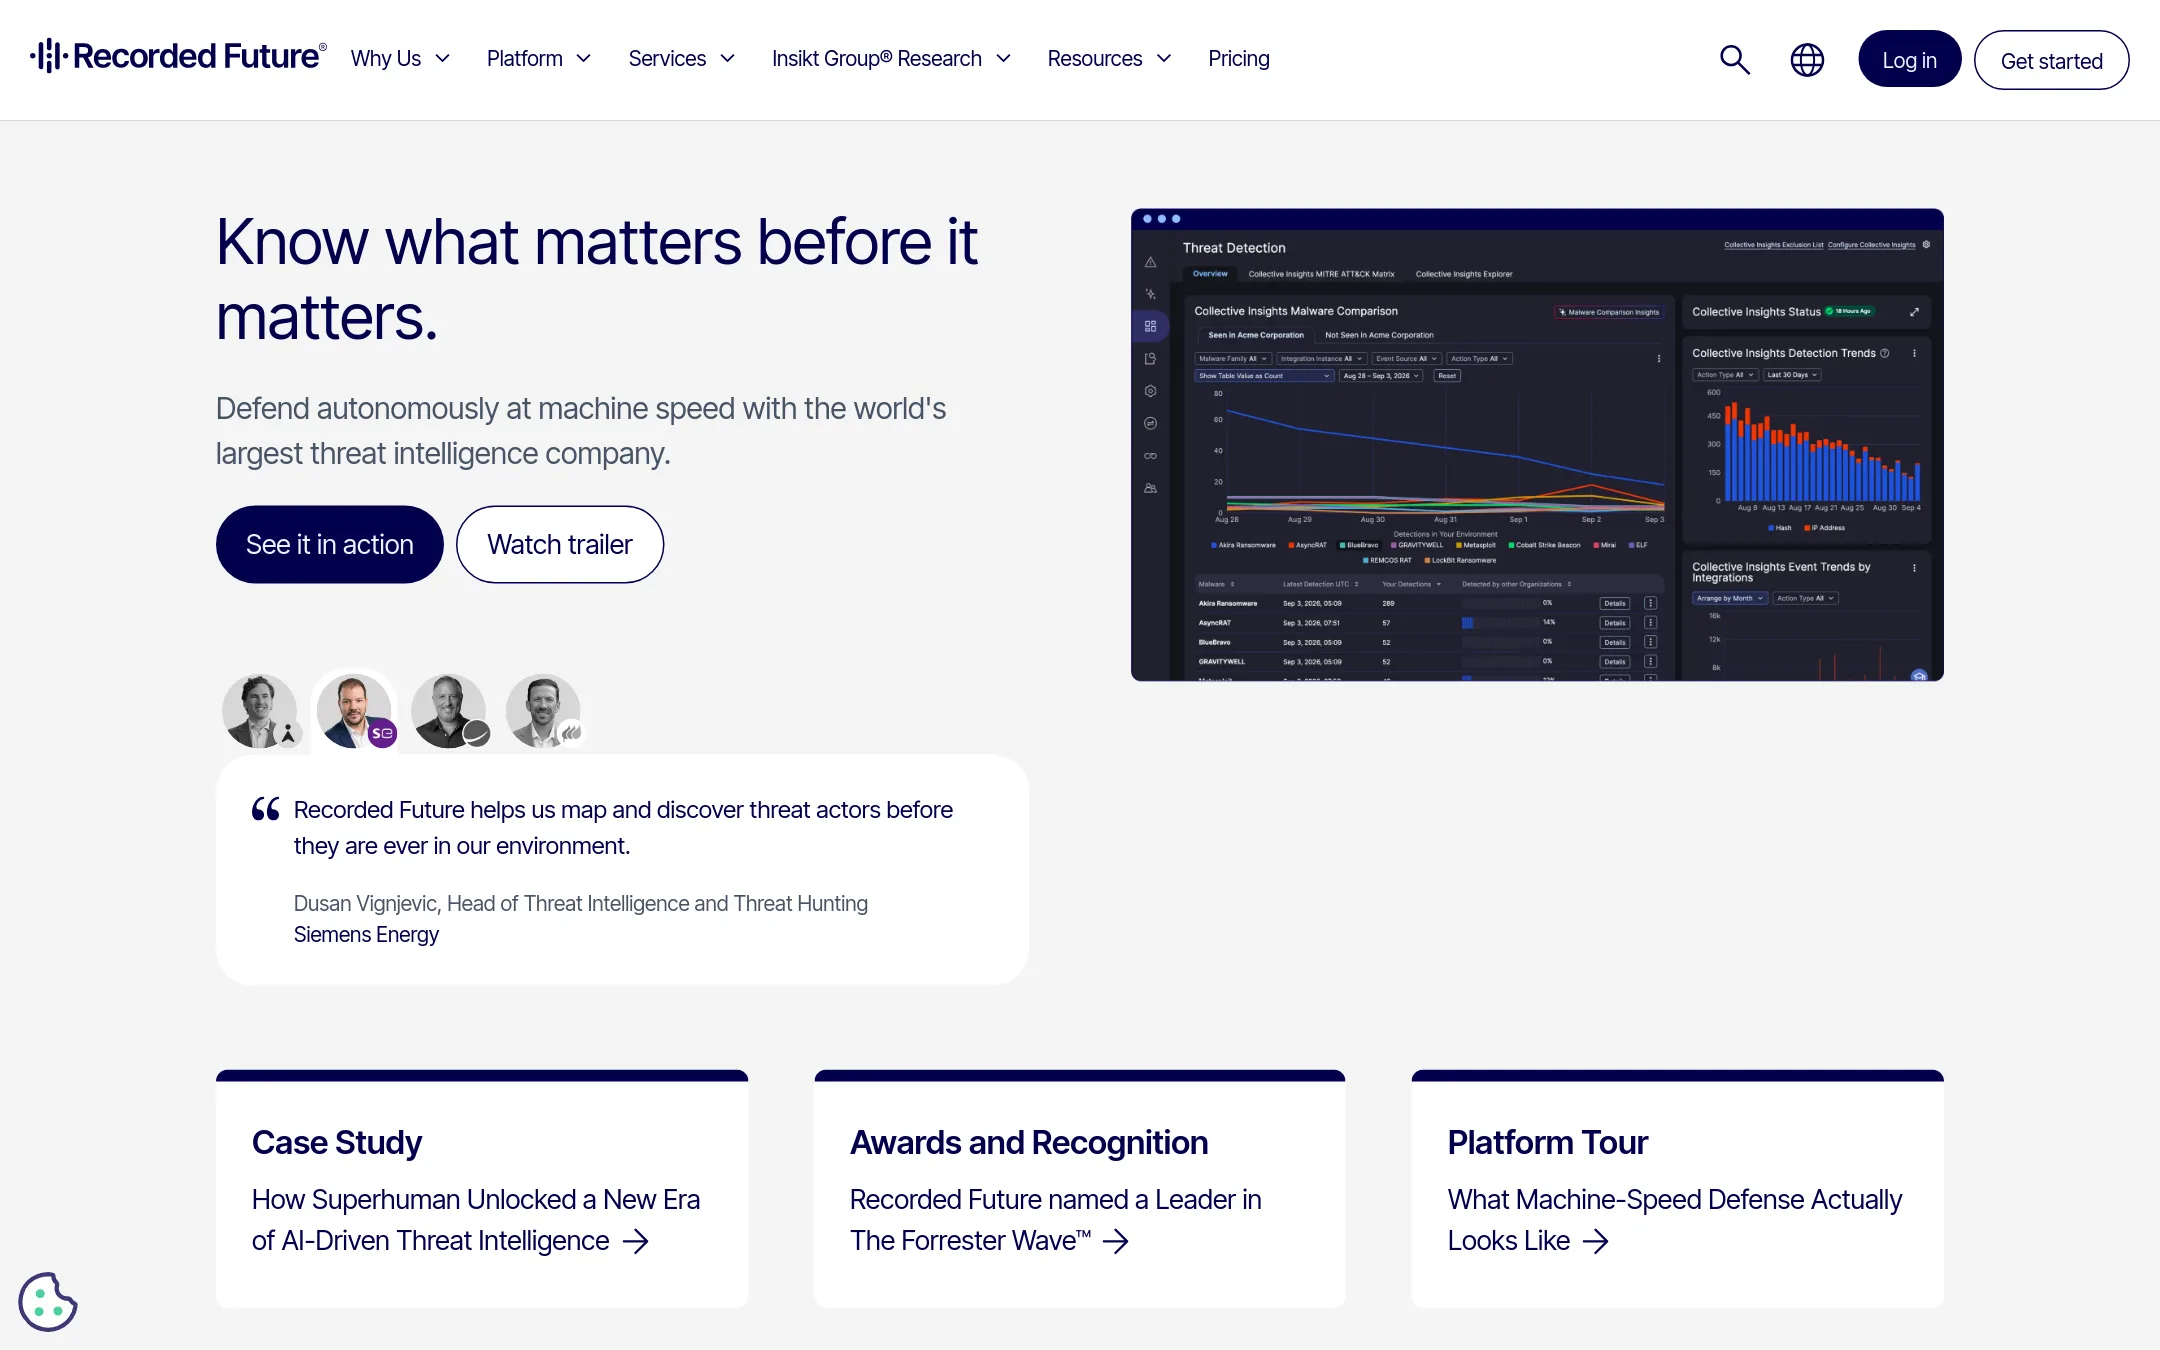
Recorded Future is a threat intelligence platform that focuses on machine-speed defense and autonomous action. Choose it over Flashpoint if you want a platform that turns intelligence into automated detections and integrates deeply across your security stack, rather than relying primarily on analyst-curated reports.
Where it is strong
- Intelligence Graph correlates signals across dark web, open web, and adversary infrastructure
- Autonomous Threat Operations deploys detections across your stack in minutes
- 100+ native integrations for security tools
Where it falls short
- Pricing is not transparent and requires contacting sales
- May be overkill for small teams that only need basic threat intel
- Pricing:
- Pricing is not published on the site. It depends on the package, organization size, add-ons, and capacity.
- From $4.99/endpoint/mo
2.CrowdStrike
Best for: Security teams that want endpoint protection, identity security, and threat intelligence in one platform, rather than a standalone intelligence feed.
- Pricing
- From $4.99/endpoint/mo
- Category
- Security & Privacy
CrowdStrike is an AI-native security platform that stops breaches across endpoints, cloud, identity, and data. Choose it over Flashpoint if you need active prevention and response rather than just threat intelligence, especially if you want a single agent for multiple security functions.
Where it is strong
- Unified platform covers endpoints, cloud, identity, and data
- AI-native detection and response with real-time threat hunting
- Flexible monthly or annual billing with a 15-day free trial
Where it falls short
- Pricing is per endpoint, so costs scale with device count
- Threat intelligence depth may be less than Flashpoint's primary-source dark web data
- Pricing:
- In the United States, pricing starts at $4.99 per endpoint per month for Falcon Go, $7.99 per endpoint per month for Falcon Pro, and $9.99 per endpoint per month for Falcon Enterprise, with annual billing available.
- Not published
3.Anomali
Best for: Enterprise SOCs and public-sector teams that want to automate triage and response with governed AI agents while keeping human approval for consequential actions.
- Pricing
- Not published
- Category
- Other
Anomali is an agentic SOC platform that fuses threat intelligence with telemetry to help security teams make governed decisions at machine speed. Choose it over Flashpoint if you want AI agents to triage, investigate, and recommend actions with approval thresholds and audit trails, rather than a threat intelligence feed with analyst reports.
Where it is strong
- Unifies data from SIEM, EDR, cloud, identity, and email into one intelligence-fused foundation.
- AURA agents triage and investigate, with approval thresholds, rollback, and audit trail.
- Cost decoupled from data volume, scaling to petabyte level.
Where it falls short
- No published pricing, so budgeting requires a sales conversation.
- Heavy focus on large enterprises and public sector, may be overkill for smaller teams.
- Pricing:
- Pricing is not published on the site.
- Not published
4.Digital Shadows (now ReliaQuest)
Best for: Security operations teams that want to automate Tier 1 and Tier 2 alert handling and reduce mean time to contain threats.
- Pricing
- Not published
- Category
- Other
Digital Shadows, now part of ReliaQuest, is a security operations platform that uses agentic AI to automate threat detection, investigation, and response. Choose it over Flashpoint if your team wants an AI-driven SOC platform that handles alerts end-to-end, rather than a threat intelligence feed that requires manual analysis.
Where it is strong
- Agentic AI investigates and resolves alerts autonomously
- Contains threats in under 5 minutes, faster than typical exfiltration time
- Model-agnostic AI layer picks the best model per task
Where it falls short
- Pricing is not transparent and likely enterprise-only
- No standalone threat intelligence offering. Focused on SOC operations
- Pricing:
- Pricing is not published on the site.
- Switching from Flashpoint:
- Moving from Flashpoint means shifting from a threat intelligence data source to a full SOC platform, so you'll need to integrate your existing security tools and workflows into GreyMatter.
- Not published
5.Intel 471
Best for: Security teams that want HUMINT-centric threat intelligence and 700+ ready-built hunt packages tied to active threat actors.
- Pricing
- Not published
- Category
- Security & Privacy
Intel 471 focuses on human intelligence from the criminal underground, with analysts embedded in the same communities where attacks are planned. It suits teams that want pre-attack intelligence and ready-to-use hunt packages, rather than a broad platform covering physical security and fraud. Choose it over Flashpoint if your priority is deep adversary tradecraft and threat hunting.
Where it is strong
- Direct access to closed criminal communities for pre-attack intelligence.
- 700+ hunt packages to speed up threat hunting in your environment.
- Verity471 platform pushes intel into existing automated systems and AI workflows.
Where it falls short
- No public pricing. Likely enterprise-focused.
- Narrower scope than Flashpoint, no physical security or fraud-specific offerings.
- Pricing:
- Pricing is not published on the site.
- Switching from Flashpoint:
- Moving from Flashpoint means shifting from a broad threat intel platform to a more specialized HUMINT-centric approach, so you'll need to re-map your workflows and integrations.
- Not published
6.Cyble
Best for: Enterprises and government agencies that want AI-native threat intelligence with dark web monitoring, attack surface management, and autonomous response in one platform.
- Pricing
- Not published
- Category
- Security & Privacy
Cyble is an AI-native threat intelligence platform that watches the dark web, monitors your attack surface, and can autonomously respond to threats. Choose it over Flashpoint if you want a unified platform that combines threat intel, digital risk protection, and endpoint security with AI-driven analysis and response.
Where it is strong
- AI-native platform with autonomous response capabilities
- Combines threat intel, dark web monitoring, and attack surface management
- Recognized as a Challenger in the 2026 Gartner Magic Quadrant for Cyberthreat Intelligence
Where it falls short
- Pricing is not public, so you need to contact sales for a quote
- May be overkill if you only need basic threat intelligence without endpoint security
- Pricing:
- Pricing is not published on the site.
- Not published
7.Feedly
Best for: CTI teams that need to quickly research threats and generate tailored briefings for stakeholders, with AI grounded in current sources.
- Pricing
- Not published
- Category
- Media & Entertainment
Feedly Threat Intelligence is an AI-driven platform that collects and analyzes threat signals from open and dark web sources, then helps you produce tailored briefings. You would choose it over Flashpoint if you want a faster, more automated workflow for turning OSINT into finished intelligence reports, with deep citations for every AI answer.
Where it is strong
- AI models extract entities, incidents, and TTPs from 10,000+ sources.
- Deep citations trace every AI response back to its original source.
- Integrates with Open CTI, XSOAR, MISP, and Slack without code.
Where it falls short
- Pricing is not transparent. You must contact sales.
- Dark web intel and commercial access are add-ons, not included in base plans.
- Pricing:
- Pricing is not published on the site.
- Switching from Flashpoint:
- Moving from Flashpoint to Feedly involves setting up your own intelligence requirements and tailoring the trial, then configuring integrations and report templates to match your existing deliverables.
- See website
8.Overwatch
Security & Privacy
Enterprise software for strategic, risk, and cyber fraud intelligence
- See website
9.TRM Labs
Security & Privacy
TRM is building a safer financial system for billions of people.
- See website
10.Chainalysis
Security & Privacy
Blockchain intelligence for investigations, risk, and security
- See website
11.Elliptic
Security & Privacy
Blockchain analytics for crypto compliance, risk management and investigations.
- Not published
12.Group-IB
Best for: Security and fraud teams that want unified cyber and fraud protection with shared data and detection logic.
- Pricing
- Not published
- Category
- Security & Privacy
Group-IB is a threat intelligence and anti-fraud platform that combines cyber and fraud detection in one system. Choose it over Flashpoint if you need fraud prevention and threat intelligence in a single platform, with a focus on predicting attacker moves.
Where it is strong
- Combines threat intelligence and fraud protection in one platform
- Shared data lake strengthens detection across all products
- Includes managed XDR with endpoint, network, and email detection
Where it falls short
- Pricing not transparent, requires sales contact
- May be more complex than Flashpoint for pure threat intelligence needs
- Pricing:
- Pricing is not published on the site.
See more comparisons in Security & Privacy alternatives.
FAQ
Questions about Flashpoint alternatives
What is the main difference between Flashpoint and Cyble?
Cyble is an AI-native platform that combines threat intelligence, dark web monitoring, and attack surface management with autonomous response. Flashpoint focuses on primary-source intelligence with analyst expertise. Choose Cyble if you want a unified platform that can act on threats automatically.
Which alternative is best for generating threat briefings quickly?
Feedly is best for CTI teams that need to research threats and produce tailored briefings for stakeholders. Its AI models extract entities and incidents from 10,000+ sources, and every AI answer has deep citations. It integrates with Open CTI, XSOAR, MISP, and Slack without code.
Are there alternatives with published pricing?
Most alternatives do not publish pricing and require contacting sales. CrowdStrike is an exception, with US pricing starting at $4.99 per endpoint per month for Falcon Go, $7.99 for Falcon Pro, and $9.99 for Falcon Enterprise. Others like Cyble, Feedly, Recorded Future, and ThreatConnect do not show prices.
Which alternative is best for physical security and executive protection?
ThreatConnect is the strongest choice for physical security and executive protection. It monitors 1M public data sources in real time for events, threats, and risks, and is trusted by two-thirds of the Fortune 50. It focuses on instant alerts rather than deep dark web intelligence.
Can I get threat intelligence plus endpoint protection in one product?
Yes, CrowdStrike offers endpoint protection, identity security, and threat intelligence in one AI-native platform. It starts at $4.99 per endpoint per month and includes a 15-day free trial. This suits teams that want active prevention and response rather than a standalone intelligence feed.
Last updated November 2, 2026.