Gecko Security alternatives
6 products compared · Updated November 22, 2026
The short answer
The three strongest alternatives to Gecko Security are Snyk, Semgrep and Checkmarx. Snyk suits development teams that want dependency, container and infrastructure-as-code scanning in one platform, with a free tier for small teams. Semgrep suits teams that want a widely used scanner that runs in their own CI and shows fixes in pull requests and IDEs. Checkmarx suits enterprise AppSec programs that need SAST, SCA, DAST and AI governance from one vendor.
Your shortlist, at a glance
Read the comparisons ↓ SnykFrom $25/mo (Team)Development teams of any size that want dependency, container and IaC scanning in one platform, with free access for small teams.
 SemgrepFrom $0 / contributorDevelopment teams that want SAST, dependency and secrets scanning in one platform with fixes shown directly in pull requests and IDEs
 CheckmarxCustom quoteEnterprise AppSec teams that need SAST, SCA, DAST and AI governance from one platform.
- VVeracodeNot publishedLarge enterprises that need governance, compliance reporting and software supply chain visibility across many applications
- AAikido SecurityTiered, plus Custom quEngineering teams that want code, cloud, pentest and runtime security in one platform, with a free starting tier for small repo counts
 GitHub ProjectsFrom $0 per user / moEngineering teams already hosting code on GitHub that want task tracking in the same place as their repositories
About Gecko Security and its alternatives
Gecko Security is an AI security engineer that reads code, infrastructure and design documents together to find vulnerabilities that get exploited, including business logic flaws and multi-step attack chains. According to its site, it ranks findings by the attack path they form, fixes the root cause and every variant in one pull request, and adds guardrails so the same flaw does not return.
When comparing alternatives in this category, weigh the pricing structure first: some vendors publish per-seat or per-repository prices, while others use prepaid credits or quotes, which makes costs harder to predict. Also check which regions and deployment models are supported, such as self-managed or hybrid scanning, which integrations your trackers and AI coding tools need, how support is delivered, and what the contract terms are for trials and annual commitments.
Explore the alternatives
- From $25/mo (Team)
1.Snyk
Best for: Development teams of any size that want dependency, container and IaC scanning in one platform, with free access for small teams.
- Pricing
- From $25/mo (Team)
- Category
- Security & Privacy
Snyk is an AI security platform that scans code, open source dependencies, containers, and infrastructure as code, and now covers AI coding agents and AI-native apps. Teams pick it over Gecko Security when they want broad coverage across dependencies, containers and IaC, plus governance of AI coding agents, rather than deep logic-flaw discovery and root-cause fixing in application code.
Where it is strong
- Free plan covers SCA, SAST, IaC and container scanning for individuals and small teams.
- Covers dependencies, containers and infrastructure as code alongside application code.
- Integrates with IDEs, CLI tools, source code managers, and AI coding assistants such as Claude Code, Cursor and Codex.
Where it falls short
- Enterprise pricing is credit-based and the full rate card is not fixed, so budgeting takes a sales conversation.
- The Team plan does not include the Evo capabilities such as AI Pentesting or coding agent security, which require an Enterprise subscription
- Pricing:
- Free plan costs $0 per month for individual developers and small teams. Team plan starts at $25 per month for up to 10 developers. Enterprise is priced by credits at $1 per credit, with Code at 1.0 credit per active contributor per day and Open Source at a sep
- From $0 / contributor
2.Semgrep
Best for: Development teams that want SAST, dependency and secrets scanning in one platform with fixes shown directly in pull requests and IDEs
- Pricing
- From $0 / contributor
- Category
- Developer Tools
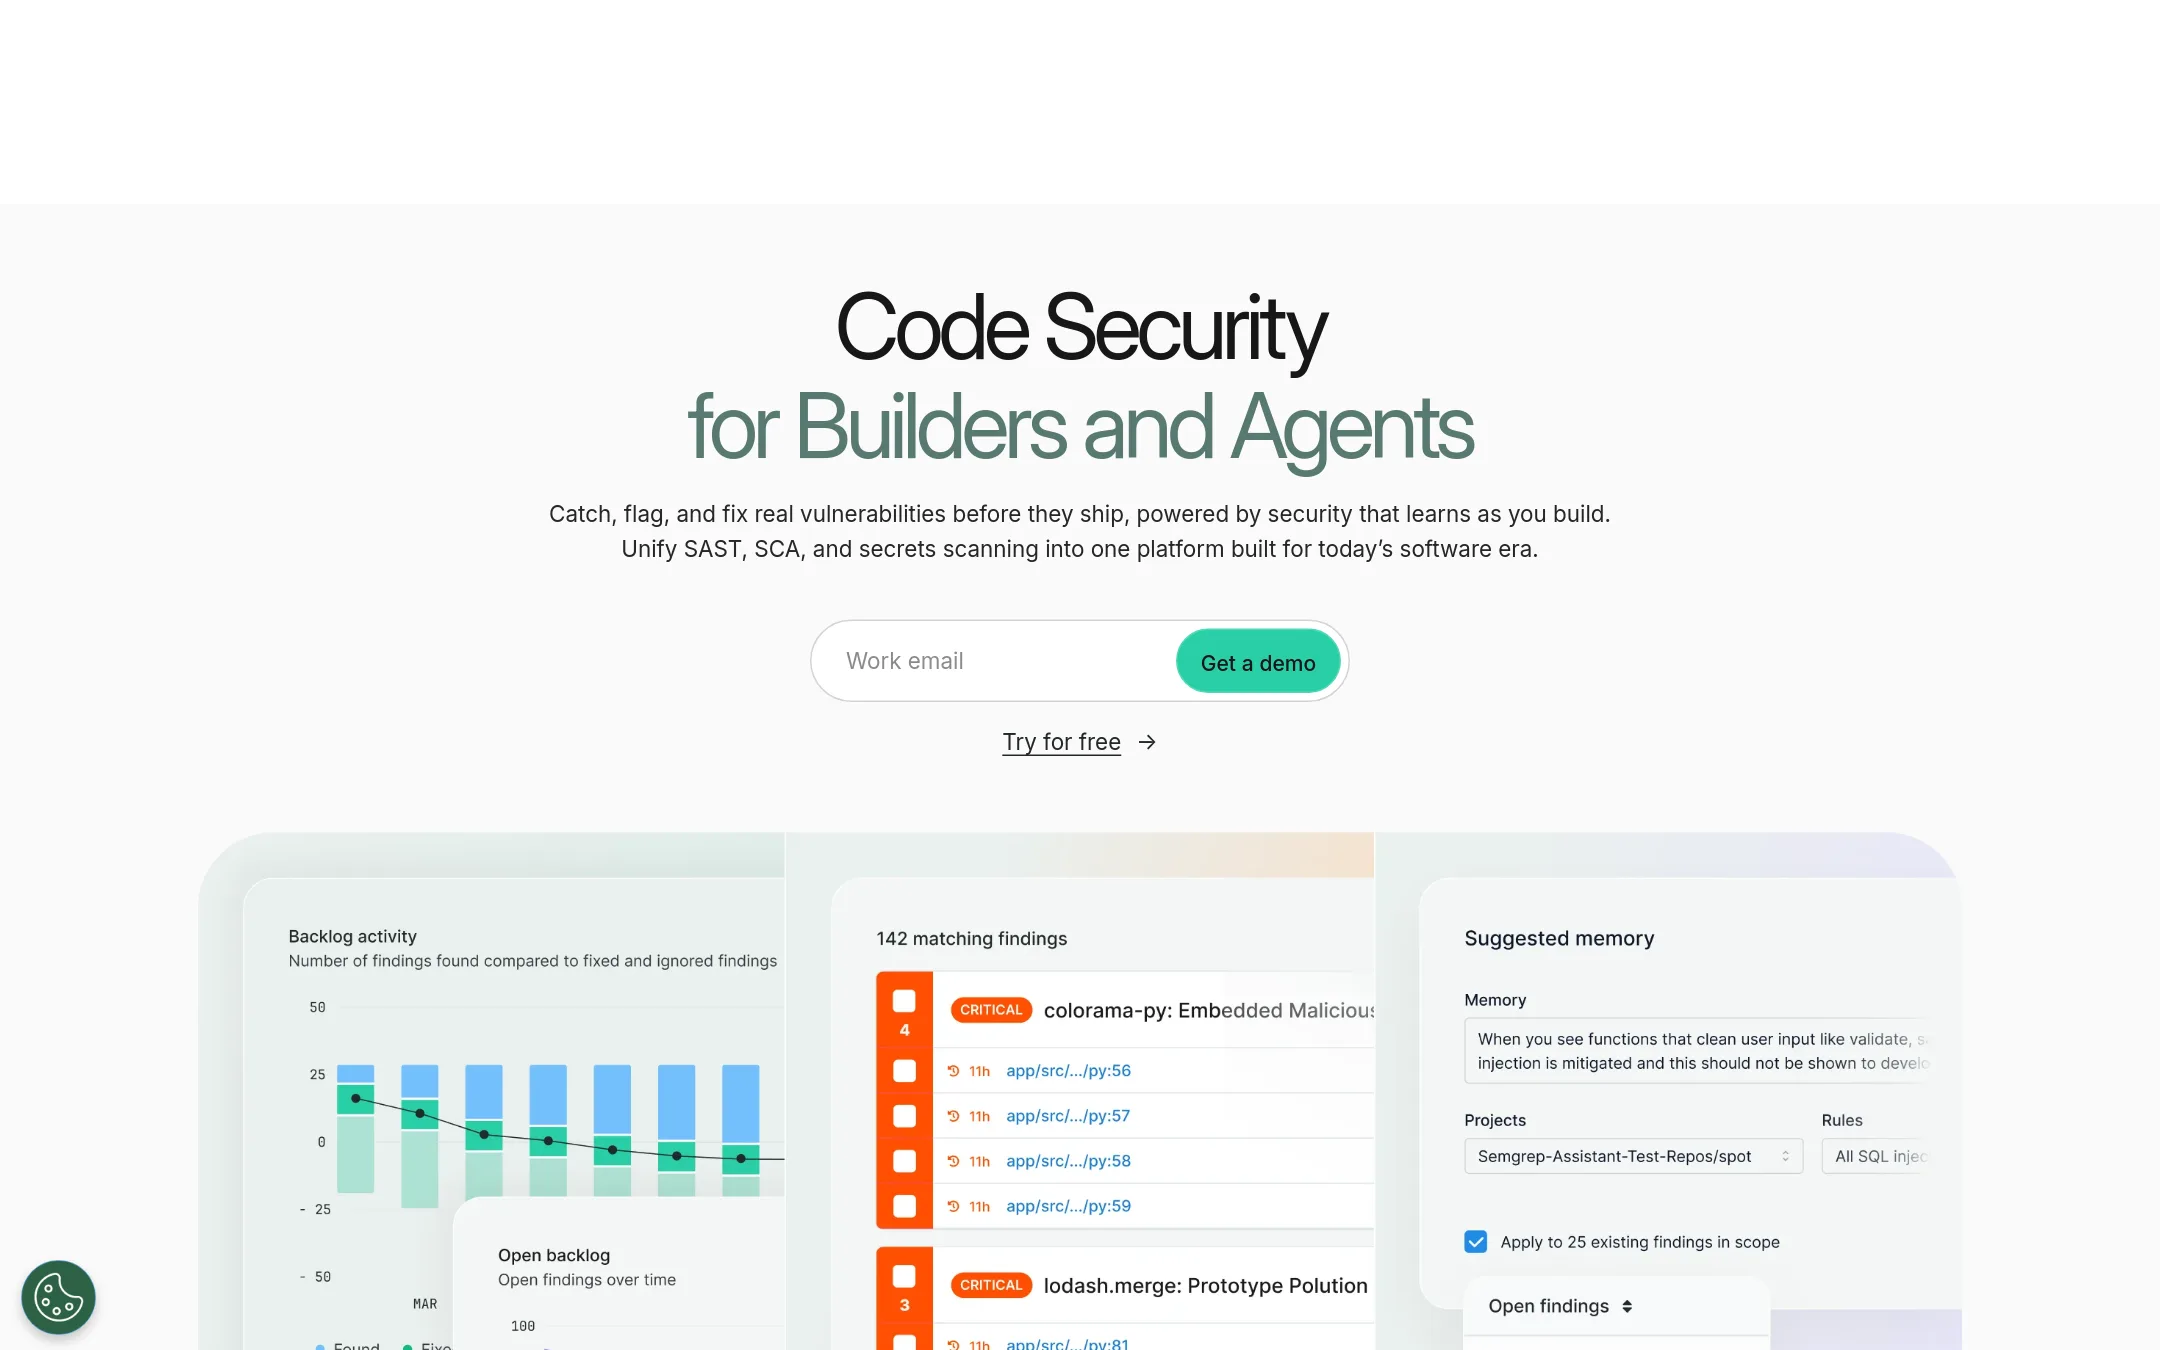
Semgrep is an application security platform that scans source code with static analysis, plus supply chain and secrets detection, and adds AI to triage false positives and suggest fixes in pull requests and IDEs. Teams choose it over Gecko Security when they want a widely used scanner that runs in their own CI, integrates into many developer tools, and gives them control over custom rules and self-managed scanning.
Where it is strong
- Runs in your CI or locally, and source code does not leave your environment for scans that run there
- Connects to GitHub, GitLab, Bitbucket, Azure, IDEs and AI tools such as Cursor through MCP
- Triage decisions are remembered, so repeated false positives are suppressed on later scans
Where it falls short
- AI credits are limited per developer on each plan, and heavy use may need more
- Business logic and multi-step attack chain detection is described as an AI addition on top of rule-based analysis, not the core focus
- Pricing:
- Semgrep lists a free tier for up to 10 repositories and 10 contributors, a Teams plan at $30 per month per contributor for Code or Supply Chain and $15 for Secrets, and custom Enterprise pricing.
- Custom quote
3.Checkmarx
Best for: Enterprise AppSec teams that need SAST, SCA, DAST and AI governance from one platform.
- Pricing
- Custom quote
- Category
- Security & Privacy
Checkmarx is a large application security platform covering SAST, SCA, API security, DAST, secrets detection and AI component inventory in one product. Teams that already run a big AppSec program, or that need many scan types and AI supply chain governance under one vendor, tend to choose it over Gecko Security. The gap is focus: Gecko concentrates on business logic flaws, attack chains and fixing whole vulnerability classes at the root, while Checkmarx covers a broader range of tools.
Where it is strong
- Covers SAST, SCA, DAST, API security, IaC, containers and secrets detection in one platform
- Has a large malicious package threat database and an AI inventory for models, MCP servers and agents
- Offers tiered packages and a shared prepaid credit balance across Fusion SAST, triage and remediation
Where it falls short
- Pricing is built around quotes and prepaid credits, which makes costs harder to predict before a consultation
- The breadth of modules means more configuration and more to govern than a focused tool
- Pricing:
- Checkmarx publishes tiered plans (Essentials, Professional, Enterprise) and per-credit rates for Fusion SAST, Triage Assist and Remediation Assist, but the page does not list a single headline price for each tier.
- VNot published
4.Veracode
Best for: Large enterprises that need governance, compliance reporting and software supply chain visibility across many applications
- Pricing
- Not published
- Category
- Other
Veracode is an application risk management platform that covers code, dependencies, pipelines and runtime signals, with AI-driven fixes and governance reporting. Enterprises choose it when they need broad compliance reporting, policy control and visibility across many applications and teams rather than a focused code-level tool.
Where it is strong
- Covers code, dependencies, containers and runtime in one platform
- Offers AI-driven fix guidance inside existing developer tools
- Provides policy control and reporting for leadership and compliance
Where it falls short
- The site does not say whether it targets business logic flaws or multi-step attack chains the way Gecko does
- Pricing and trial terms are not published, so cost has to come from a sales conversation
- Pricing:
- Pricing is not published on the site.
- ATiered, plus Custom qu
5.Aikido Security
Best for: Engineering teams that want code, cloud, pentest and runtime security in one platform, with a free starting tier for small repo counts
- Pricing
- Tiered, plus Custom qu
- Category
- Other
Aikido Security is a single platform covering code, cloud, pentesting and runtime protection. Teams pick it when they want one vendor across AppSec, cloud posture and runtime defense, rather than a tool focused only on code-level root cause fixes like Gecko.
Where it is strong
- Covers code, cloud, pentesting and runtime defense in one platform
- Plans scale by repos, domains, cloud accounts and protected requests
- Offers AI AutoFix with a monthly allowance on the entry plan
Where it falls short
- Its flagship pitch is broad platform coverage, not root-cause fixing of whole vulnerability classes as Gecko emphasizes
- Enterprise features like local scanning and internal pentesting sit behind a custom quote
- Pricing:
- Pricing is published by plan and module: the entry plan includes 10 repos, 2 container images, 1 domain, 1 cloud account, 10 AI AutoFixes per month and 250k protected requests per month, with higher tiers scaling to 500 repos and 50M protected requests per mon
- From $0 per user / mo
6.GitHub Projects
Best for: Engineering teams already hosting code on GitHub that want task tracking in the same place as their repositories

- Pricing
- From $0 per user / mo
- Category
- Productivity & Project Management
GitHub Projects is a planning and tracking tool that lives next to your code, so issues, pull requests and boards share one place. A team would pick it over Gecko Security when the need is managing work and code workflow rather than finding and fixing exploitable vulnerabilities. The supplied facts do not show security scanning as part of Projects itself.
Where it is strong
- Sits inside the same platform where your code, pull requests and reviews already live
- Free plan covers unlimited public and private repositories with Issues and Projects
- Large ecosystem with Actions, Codespaces and a very large developer community
Where it falls short
- Planning and tracking is not a security product, so it does not find or prioritize vulnerabilities the way Gecko Security does
- Security features such as Code Security and Secret Protection are sold separately on top of the base plans
- Pricing:
- The Free plan is $0 per user per month, Team is $4 per user per month, and Enterprise is $21 per user per month, with Copilot access included on Enterprise.
See more comparisons in Security & Privacy alternatives.
FAQ
Questions about Gecko Security alternatives
Which alternative is closest to Gecko Security's focus on fixing root causes?
None of the entries describes root-cause fixing of whole vulnerability classes in the same way Gecko does. Semgrep comes closest in practice, since it offers AI-suggested fixes in pull requests and remembers triage decisions across scans. Checkmarx and Veracode cover code-level fixing as part of broader platforms.
Which options publish clear pricing?
Snyk and Semgrep publish plan prices, including a free tier for Snyk and a free tier for up to 10 repositories on Semgrep. Aikido Security also publishes prices by plan and module. Checkmarx uses quotes and prepaid credits, and Veracode does not publish pricing.
Which alternative is best for a large enterprise with compliance needs?
Veracode is aimed at enterprises that need policy control, compliance reporting and visibility across many applications. Checkmarx is also suited to enterprise AppSec teams that want SAST, SCA, DAST and AI governance under one vendor.
Which tool suits a small team that wants to start for free?
Snyk has a free plan for individual developers and small teams that covers SCA, SAST, IaC and container scanning. Semgrep's free tier covers up to 10 repositories and 10 contributors. Aikido Security also has an entry plan for small repository counts.
Is GitHub Projects a security alternative?
Not really. GitHub Projects is a planning and tracking tool for code work, and its security features such as Code Security are sold separately. Teams would consider it when the need is managing tasks alongside code rather than finding and prioritizing exploitable vulnerabilities.
Last updated November 22, 2026.