
Midship alternatives
8 products compared · Updated November 12, 2026
The short answer
Vanta suits startups and mid-market companies that need SOC 2 or ISO 27001 quickly, with automated evidence collection. Diligent suits fintechs and banks that need to automate KYC and AML reviews and screening alert triage. Archer suits regulated enterprises such as banks and insurers that need a full GRC system covering regulatory change, third-party risk and audit.
Your shortlist, at a glance
Read the comparisons ↓- SServiceNow GRCSee websiteEnterprise governance, risk and compliance platform
 MetricStreamNot publishedLarge regulated enterprises in banking, insurance, healthcare, transport or energy that need connected GRC across risk, compliance, cyber and audit
 DiligentNot publishedFintechs and banks that need to automate KYC/AML reviews, merchant risk checks and screening alert triage
 LogicGateNot publishedEnterprise risk and compliance teams that want one configurable platform for several GRC programs, including third-party risk and cyber risk.
 ArcherNot publishedRegulated enterprises such as banks and insurers that need a full GRC system covering regulatory change, third-party risk and audit
 VantaNot publishedStartups and mid-market companies that need SOC 2 or ISO 27001 quickly and want automated evidence collection
 DrataNot publishedStartups and mid-size SaaS companies that need SOC 2 or ISO 27001 readiness and continuous compliance across multiple frameworks.
 HyperproofNot publishedSecurity and compliance teams that need one control set mapped across many frameworks and a trust center for customer questionnaires
About Midship and its alternatives
Midship is a SOX testing product in the Finance & Accounting category. Its site presents it as an AI-driven platform for automating SOX testing, which is the work of checking that a company's financial controls operate as designed.
When comparing alternatives in this category, weigh the pricing structure first, since many vendors in this space do not publish prices and quotes require a sales conversation. Then check which regions and frameworks the tool covers, which integrations it offers with your existing systems, how much support and implementation help is included, and what the contract terms look like.
Explore the alternatives
- SSee website
1.ServiceNow GRC
Security & Privacy
ServiceNow's Integrated Risk Management suite covers governance, risk and compliance workflows for enterprises, overlapping with Optro's core GRC platform.
- Not published
2.MetricStream
Best for: Large regulated enterprises in banking, insurance, healthcare, transport or energy that need connected GRC across risk, compliance, cyber and audit
- Pricing
- Not published
- Category
- Finance & Accounting
MetricStream is an enterprise GRC platform covering governance, risk, compliance, cyber and audit, with AI agents and assistants that flag emerging risks, recommend controls and generate board-ready briefings. Teams in regulated industries such as banking, insurance, healthcare, transport and energy tend to pick it when they need one connected system across many GRC functions rather than a narrow tool. Someone would choose it over Midship when the job is broad program management instead of SOX testing alone.
Where it is strong
- Covers governance, risk, compliance, cyber and audit in one platform
- AI agents and assistants recommend actions and can execute approved steps within set guardrails
- Large footprint with over 1M users across hundreds of Fortune 500 and Global 1000 organizations in 35+ countries
Where it falls short
- Built for large enterprises, so it may be heavy for a small startup team
- Public materials do not show a published price, so cost comparison requires a sales conversation
- Pricing:
- Pricing is not published on the site.
- Not published
3.Diligent
Best for: Fintechs and banks that need to automate KYC/AML reviews, merchant risk checks and screening alert triage
- Pricing
- Not published
- Category
- AI & Machine Learning
Diligent builds AI agents that automate KYC and AML operations for fintechs and banks. It runs merchant risk investigations, clears false positive alerts from sanctions and PEP screening tools, and verifies customer documents. Someone would pick it over Midship when their pain is manual KYC/AML review queues rather than SOX testing or enterprise GRC.
Where it is strong
- Focused on KYC/AML and merchant risk, the workflows fintech compliance teams handle daily
- Connects by API, through its portal, or via native integrations with screening tools
- Keeps humans in the loop with analyst review before scaling automation, and leaves an auditable trail
Where it falls short
- Built for financial crime and onboarding workflows, so it does not cover SOX testing or broad enterprise GRC the way Midship does
- The site does not publish pricing, so cost has to come from a sales conversation
- Pricing:
- Pricing is not published on the site.
- Not published
4.LogicGate
Best for: Enterprise risk and compliance teams that want one configurable platform for several GRC programs, including third-party risk and cyber risk.
- Pricing
- Not published
- Category
- Finance & Accounting
LogicGate is an AI-powered GRC platform built around 30+ purpose-built applications for enterprise risk, third-party risk, cyber risk and compliance, connected through a no-code graph database. A team would choose it over Midship when they need a broad, configurable GRC system covering many programs rather than a focused tool for SOX testing and audit workflows.
Where it is strong
- Covers 30+ GRC applications, including enterprise risk, third-party risk, cyber risk and compliance, in one platform.
- No-code configuration and a graph database connect controls, assets and risks without rigid SQL silos.
- Integrates with 200+ tools so risk data can flow in without manual exports.
Where it falls short
- Its homepage focus is broad GRC rather than SOX testing, so a team needing that specific workflow may find Midship more targeted.
- Pricing depends on applications and Power User licenses, and the exact costs are not published on the site.
- Pricing:
- Pricing is not published on the site.
- Not published
5.Archer
Best for: Regulated enterprises such as banks and insurers that need a full GRC system covering regulatory change, third-party risk and audit
- Pricing
- Not published
- Category
- Security & Privacy
Archer is an integrated risk management platform that connects risks, controls, obligations and evidence to business objectives, with a strong focus on regulatory change management. Teams choose it over Midship when they need a broad GRC system of record covering enterprise, IT, operational and third-party risk, not just SOX testing. It fits organizations with heavy regulatory exposure, such as banks and insurers, that want audit lineage from source to obligation, control and evidence.
Where it is strong
- Covers risk, compliance, audit, third-party and IT security in one platform
- Tracks regulatory change from source to obligation, control and evidence
- Can run alongside an existing Archer GRC setup without a full migration
Where it falls short
- Aimed at large, highly regulated enterprises, so it may be heavy for a small team
- Pricing is not published, so cost has to be found through a sales conversation
- Pricing:
- Pricing is not published on the site.
- Switching from Midship:
- Archer Evolv can be deployed standalone or alongside Archer GRC, on-premises or SaaS, without a costly migration or rebuild, though the site does not describe steps for moving from Midship specifically.
- Not published
6.Vanta
Best for: Startups and mid-market companies that need SOC 2 or ISO 27001 quickly and want automated evidence collection
- Pricing
- Not published
- Category
- Security & Privacy
Vanta automates compliance work for SOC 2, ISO 27001, HIPAA, GDPR and other frameworks, with continuous monitoring and a Vanta Agent that drafts policies and completes security questionnaires. Teams pick it over Midship when their main problem is getting a security certification and answering customer security reviews, rather than running SOX testing for a public company's financial controls.
Where it is strong
- Covers many frameworks, including SOC 2, ISO 27001, HIPAA, GDPR and FedRAMP
- The Vanta Agent helps with policies and security questionnaires
- Continuous monitoring shows control gaps as they appear between audits
Where it falls short
- Built around security and privacy frameworks rather than SOX financial controls testing
- Pricing requires a demo request to get personalized figures
- Pricing:
- Pricing is not published on the site.
- Not published
7.Drata
Best for: Startups and mid-size SaaS companies that need SOC 2 or ISO 27001 readiness and continuous compliance across multiple frameworks.
- Pricing
- Not published
- Category
- Security & Privacy
Drata is an AI-native compliance and trust platform that automates evidence collection, control monitoring, and audit readiness across frameworks like SOC 2, ISO 27001, and HIPAA. Teams pick it over Midship when their main problem is getting and staying compliant with security frameworks, not SOX testing for public company finance controls. It also covers third-party risk, customer trust centers, and questionnaire automation.
Where it is strong
- Automates evidence collection and monitors controls continuously across the stack
- Covers multiple frameworks such as SOC 2, ISO 27001, GDPR, HIPAA and PCI DSS from one mapped control set
- Includes a Trust Center and AI-drafted questionnaire responses to shorten sales security reviews
Where it falls short
- Built around security and privacy compliance, so it is a weaker fit for SOX testing and finance audit workflows than Midship
- Public pricing is not listed, so budgeting requires a sales conversation
- Pricing:
- Pricing is not published on the site.
- Not published
8.Hyperproof
Best for: Security and compliance teams that need one control set mapped across many frameworks and a trust center for customer questionnaires
- Pricing
- Not published
- Category
- Security & Privacy
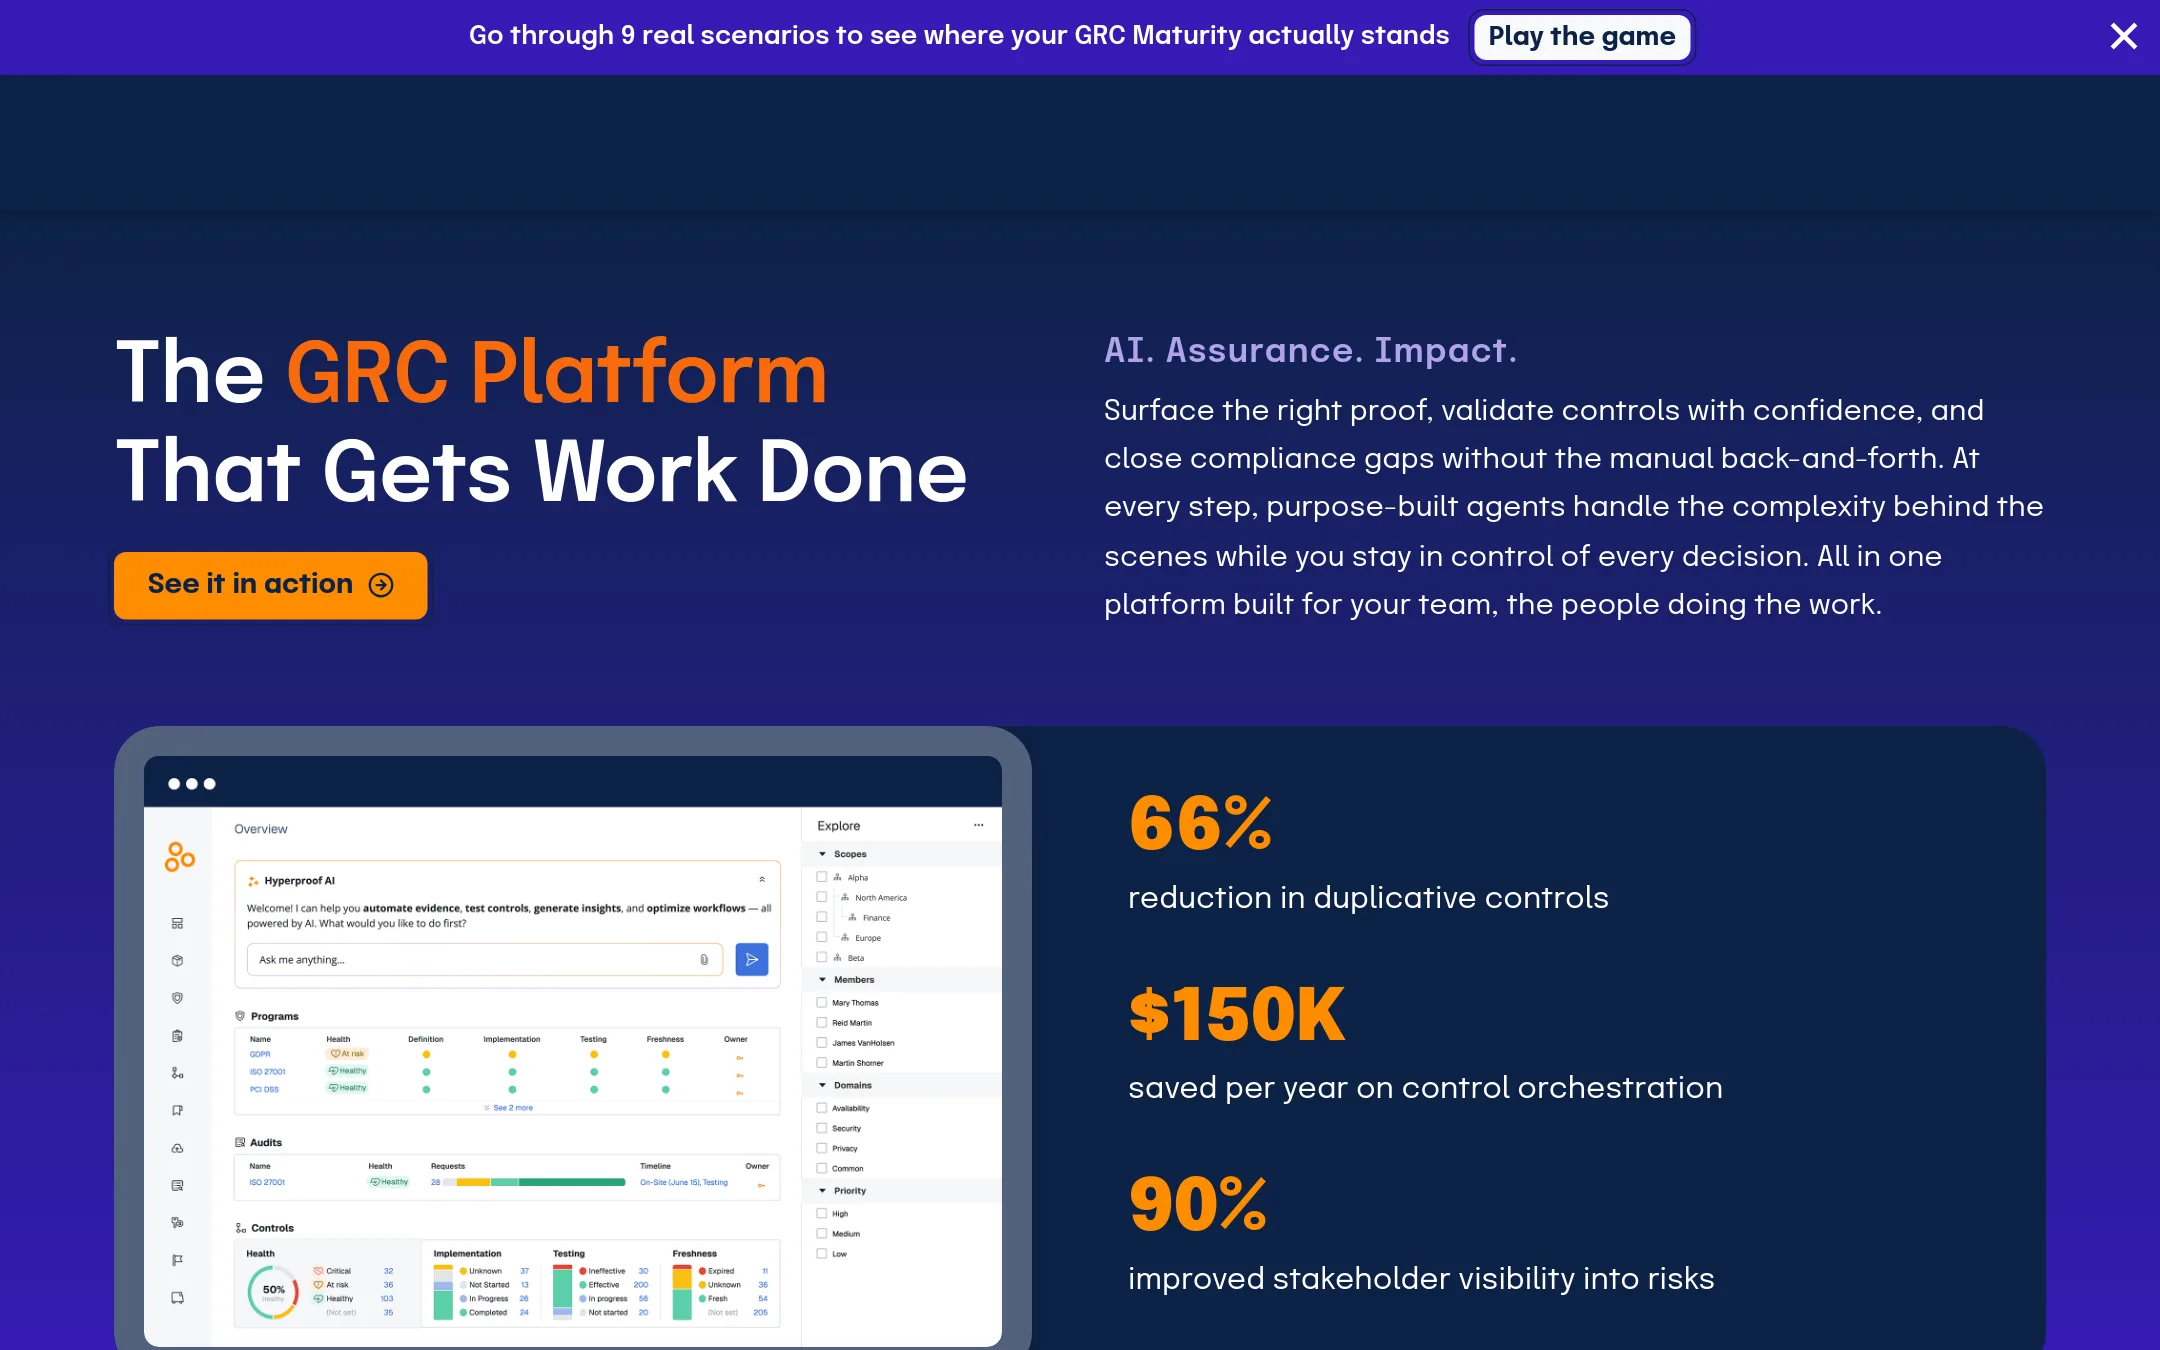
Hyperproof is a GRC platform for teams that need continuous compliance, risk, audit, trust center, third-party risk and policy management in one place. It suits organizations that want to map one common control set across many frameworks and cut duplicate control work. A company would pick it over Midship if its need is broad GRC coverage rather than SOX testing specifically.
Where it is strong
- Covers compliance, risk, audit, trust, third-party risk and governance from one platform
- Lists over 160 pre-built frameworks
- Offers a FedRAMP Certified Class C (Rev5) environment for high-security organizations
Where it falls short
- Its homepage stresses framework breadth, so it is less of a SOX testing specialist than Midship
- Its homepage gives no published pricing, so cost comparison needs a sales conversation
- Pricing:
- Pricing is not published on the site.
See more comparisons in Finance & Accounting alternatives.
FAQ
Questions about Midship alternatives
What is the best Midship alternative for a startup that needs SOC 2 quickly?
Vanta is the entry aimed at this need. It automates compliance work for SOC 2, ISO 27001, HIPAA and GDPR, with continuous monitoring and a Vanta Agent that drafts policies and completes security questionnaires. Drata is a close second, covering similar frameworks with automated evidence collection and a Trust Center.
Which alternative is best if I need SOX testing rather than security certification?
The entries here focus mostly on security, privacy, financial crime or broad enterprise GRC rather than SOX financial controls testing, which is Midship's specialty. Archer and MetricStream cover broader enterprise governance and audit, so they may come closer for large regulated firms, but a dedicated SOX comparison should be made by checking each vendor directly.
Which alternatives suit fintechs and banks?
Diligent is built for fintechs and banks that need to automate KYC and AML operations, including merchant risk investigations and clearing false positive alerts from sanctions and PEP screening. Archer suits larger banks and insurers that need regulatory change tracking and a full GRC system of record.
Do these alternatives publish their prices?
None of the entries on this page list published pricing on their sites. Vanta, Diligent, Drata, Hyperproof, Archer, LogicGate and MetricStream all require a sales conversation or a demo request to get cost figures, so budget comparisons will need direct quotes.
Which alternative covers the most frameworks in one platform?
Hyperproof lists over 160 pre-built frameworks and is built around mapping one common control set across many of them. LogicGate covers 30+ GRC applications and connects with 200+ tools. Drata also covers multiple frameworks including SOC 2, ISO 27001, GDPR, HIPAA and PCI DSS from one control set.
Last updated November 12, 2026.